Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • Cloud Mining Revealed: How Bitcoin Investors Can Earn Up to $99,999 in 10 Days!
  • Technique

Cloud Mining Revealed: How Bitcoin Investors Can Earn Up to $99,999 in 10 Days!

Do Son October 1, 2025 2 minutes read
Img_2025_10_02_21_05_15

Still regretting missing out on Bitcoin’s early dividends? Now’s your chance! Open Miner’s intelligent cloud mining platform revolutionizes traditional mining methods, allowing you to easily participate in the crypto wealth bonanza!

Sign up and get $500! Sign in and earn!

New users simply register to instantly receive $500 in hashrate trial credits, allowing you to participate in mining and earn money without any entry barriers! Even better, sign in daily to receive a $1 cash bonus – truly earn while you play!

What is cloud mining?

By saying goodbye to the high costs and complex technical challenges of mining machines, Open Miner provides you with remote computing power from top data centers around the world. You don’t need to purchase equipment, worry about electricity costs, or maintain it. All you need is a phone or computer to easily enjoy the benefits of mining.

Joining is super easy.

Visit the official website at https://openminer.biz, register with your email address, receive a $500 trial bonus, select a hash rate contract, activate it, and start your mining journey. Sign in daily to receive $1, and earn every day! View your earnings in real time on the dashboard.


(Some contracts are shown below) β†’ [Click here to find more hashrate contracts]
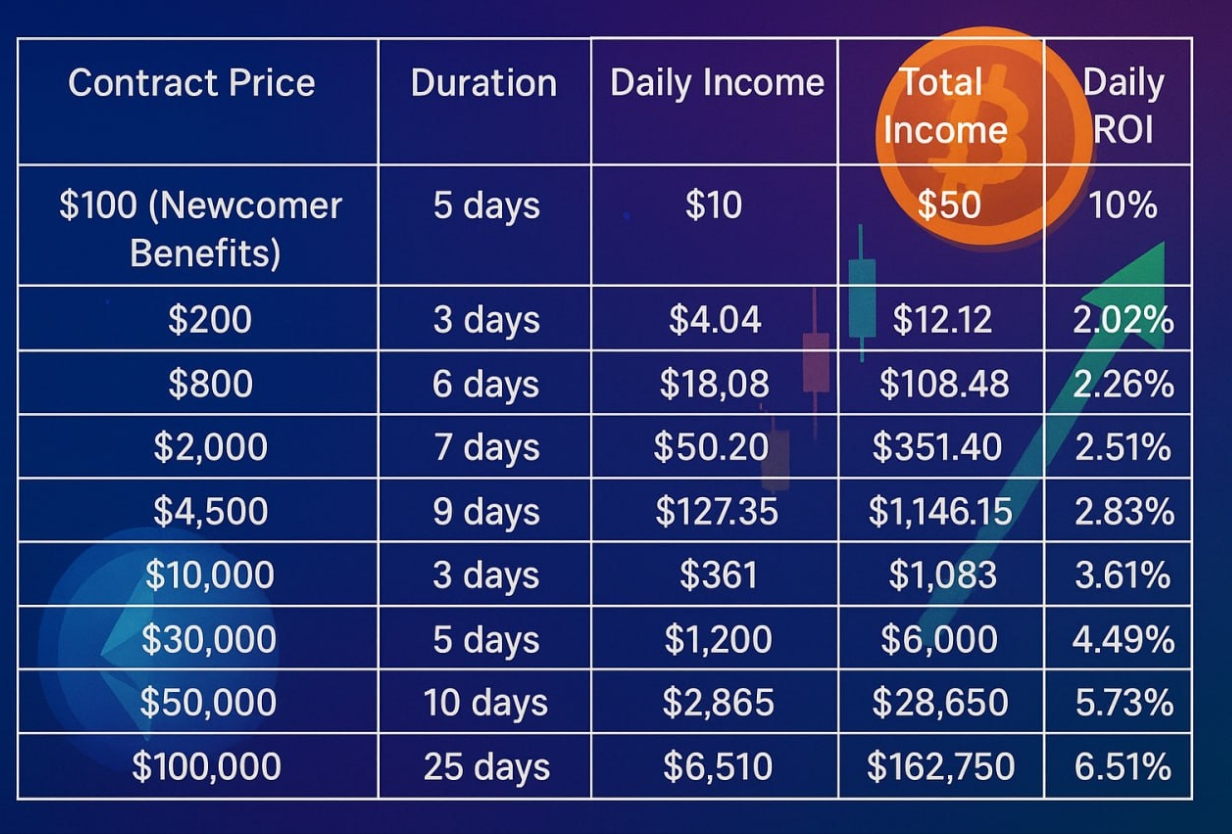
Why choose Open Miner?

Intelligent Management: AI algorithms automatically optimize mining efficiency for higher returns!

Low Entry: Zero-cost experience, sign up and start earning!

Guaranteed Principal and Interest: The only platform on the internet that guarantees principal!

Internationally Authoritative Certification: FCA-certified for added security!

Profit anytime, anywhere: One-click operation on your phone, 24/7 automatic mining!

Summary

Open Miner is more than just a cloud mining platform; it’s your new starting point on the path to digital wealth freedom. Join us now and earn daily in popular cryptocurrencies like BTC, ETH, XRP, DOGE, USDT, and more, making every day filled with unexpected returns!

For more details, please visit the official website: https://openminer.biz
Company Name: Open Miner. Media Inquiries: info@OpenMiner.net

#BitcoinMining

#AICloudMining

#CryptoPassiveIncome

#DogecoinMining

#Cryptomining

Disclaimer: This is a Press Release provided by a third party who is responsible for the content. Please conduct your own research before taking any action based on the content.

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2014-125131CVSS 5.1
    DedeCMS 5.6 and 5.7 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2015-20124CVSS 8.7
    Aspose Importer & Exporter plugin for WordPress before 3.0 contains a path traversal vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2016-20102CVSS 5.1
    JavaMelody before 1.60.0 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by supplying...
    Watchtower Verified📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-112327CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in TMS Amelia ameliabooking allows...
    📅 Updated: Oct 22, 2026
  • CVE-2026-112241CVSS 9.8
    Authentication Bypass by Spoofing vulnerability in Brainstorm Force SureCart surecart allows Authentication Abuse.This issue affects SureCart: from n/a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-15143CVSS 9.3
    A flaw was found in the file_type content detector of guardrails-detectors. This vulnerability allows a remote attacker to...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114220CVSS 9.3
    NT OneAPP developed by NewType Infortech has an Improper Certificate Validation vulnerability. Unauthenticated network-adjacent attackers can perform a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114219CVSS 9.1
    NT OneAPP developed by NewType Infortech has a Hard-coded Credentials vulnerability. Unauthenticated remote attackers can obtain the hard-coded...
    📅 Updated: Oct 22, 2026
  • CVE-2026-107081CVSS 9.8
    SQL injection via identifier injection in the tableName and tableFields POST parameters of admin AJAX endpoints (admin/AJAX_lookup_handler.php, admin/AJAX_check_id.php,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.