Criminal IP Launches AITEM to Connect Asset Discovery with AI-Powered Exposure Management
 cybernewswire
Torrance, California, USA, November 19th, 2026, CyberNewswire
Criminal IP, a cyber threat intelligence platform developed by AI SPERA, officially launched Criminal IP AITEM (AI-Powered Threat Exposure Management) on November 18, 2026. An evolution of Criminal IP ASM, AITEM combines internet-facing asset discovery with AI-assisted investigation, public-source exposure analysis, and dark web monitoring. It also introduces AI Pentest to help security teams assess and validate security risks in their web assets.
Discovering an unfamiliar server or a leaked credential is the first step. Analysts still need to establish how it relates to their organization, assess the surrounding threat signals, and decide whether it requires immediate attention. Criminal IP AITEM brings these findings and their context together so teams can understand what is exposed and decide where to act.
A Broader View of Organizational Exposure
Forgotten servers, publicly accessible configuration files, and compromised credentials can be difficult to assess when findings are scattered across separate tools. Criminal IP AITEM brings these exposures into a single view so teams can investigate them in the context of their environment.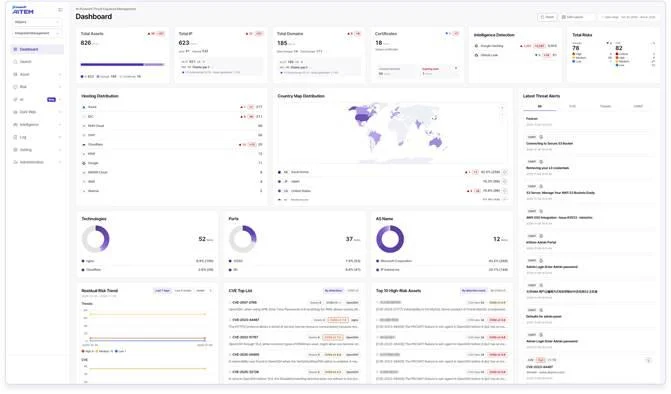
Criminal IP AITEM dashboard summarizes asset inventory, risk distribution, recent findings, and exposure trends
The dashboard gives teams an overview of discovered assets and detected risks. Analysts can drill down into individual assets to investigate specific findings and explore related infrastructure.
Criminal IP AITEM continuously discovers internet-facing assets and collects information such as IP addresses, domains, certificates, open ports, cloud assets, and technologies. Analysts can use these details to understand how an unfamiliar system connects to their organization.
Exposure Beyond Managed Infrastructure
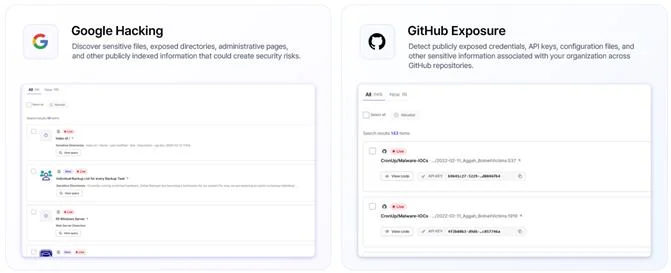
Criminal IP AITEM identifies publicly accessible information through search engine analysis and GitHub exposure detection
Public-source exposure analysis helps teams find sensitive files, administrative pages, and exposed directories indexed by search engines. GitHub exposure detection helps uncover publicly accessible credentials, API keys, and configuration files associated with the organization.
Dark web monitoring surfaces leaked credentials, exposed information, and mentions of the organization across monitored sources. Available source details help analysts assess each finding and decide what to investigate next.
AI Across the Exposure Lifecycle
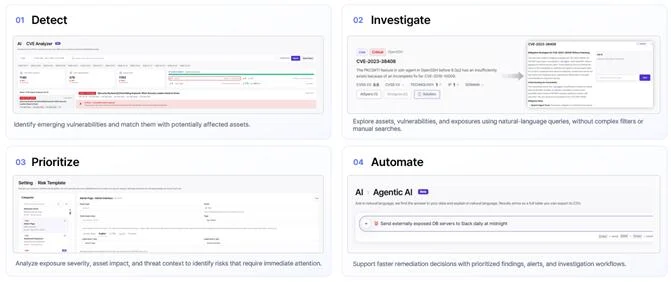
AI-Powered at Every Step: Detect, Investigate, Prioritize, and Automate
Criminal IP AITEM applies AI across detection, investigation, prioritization, and automation. It connects emerging vulnerabilities with potentially affected assets and supports natural-language queries across assets, vulnerabilities, and exposures, reducing the need for complex filters and repeated manual searches.
Prioritization considers exposure severity, asset impact, and threat context to help teams decide which findings need attention first. Automated alerts and investigation workflows support follow-up and reduce manual tracking as risks change.
For example, when Criminal IP AITEM discovers an unfamiliar server, analysts can review its open ports, exposed services, SSL/TLS configurations, and related CVEs. Criminal IP threat intelligence adds context through connected infrastructure, malicious activity, abuse history, and associated threat indicators. Together, these details help analysts assess the server’s potential impact and decide what to investigate first.
Validating Web Asset Risks with AI Pentest
Criminal IP AITEM’s AI Pentest capability enables security teams to run AI-powered penetration tests on their web assets. Teams can use it to identify potential vulnerabilities and validate suspected security weaknesses, giving them additional evidence to decide which findings require remediation.
Continuous Monitoring as Exposure Changes
As organizations deploy services and work with external suppliers, their exposure changes. Criminal IP AITEM uses daily scans, historical tracking, and automated notifications to help teams follow those changes. Monitoring can also extend to partners and suppliers.
With Criminal IP AITEM, Criminal IP connects asset visibility with exposure investigation and ongoing monitoring. Security teams can better understand what is exposed, why a finding matters, and where to focus their next action.
Learn more about Criminal IP AITEM.
About Criminal IP
Criminal IP is AI SPERA’s flagship cyber threat intelligence platform. Used in more than 150 countries, it provides comprehensive threat visibility through Criminal IP Search, Criminal IP ASM, Criminal IP FDS, and Criminal IP TI Feed.
Criminal IP continues to expand its global security ecosystem through integrations and strategic partnerships. Its threat intelligence is also accessible through major cloud and data marketplaces, including Amazon Web Services, Microsoft Azure, and Snowflake.
Contact
Michael Sena
AI SPERA
support@aispera.com