Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • Does Asus WiFi Extender Truly Protect the Home Network?
  • Technique

Does Asus WiFi Extender Truly Protect the Home Network?

Do Son February 4, 2022 4 minutes read
ASUS DSL Router, Authentication Bypass Cyclops Blink malware

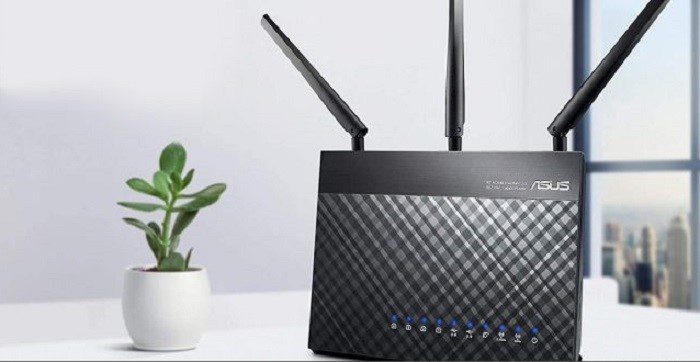
Taiwan-based Asus multinational phone and computer hardware and electronics firm with its headquarters in the Beitou District of Taipei. Asus WiFi extenders offer the most secure home network and are considered among the company’s best products.

If you are wondering, does Asus extender truly protect the home network? You are at the right place! Stay stick to this guide to get the answer!

How does Asus WiFi Extender protect the home network?

Asus extenders offer AiProtection to ensure enterprise-level security in the home. AiProtection eliminates a vulnerability in your home gateway by first evaluating your router’s configuration for potentially harmful gaps and then deleting those vulnerabilities from the configuration.

Moreover, while browsing the internet, AiProtection, in conjunction with web reputation service (WRS) and DPI, continuously defends and prevents you from unintentionally visiting potentially harmful websites.

In addition, AiProtection protects against incursion from several cyber threats, including malware, malicious websites, and system vulnerabilities. In conclusion, alarms are generated when a device on your network is hacked and displays suspicious activity.

Assess Security Settings

Many seemingly little issues might jeopardize security, such as a weak router password, unencrypted WiFi, or allowing remote access, among others.

It is also possible that hackers will be able to modify your network settings and circumvent your firewall to manage gadgets, steal sensitive personal information, or even utilize your IP camera remotely if your settings are incorrect.

Asus extenders review all fundamental security settings and ensure all of the devices linked to your home network are safe and secure against external intrusion. You’ll have the confidence in knowing that hackers will be kept away that your data will be kept secure.

Block Malicious Websites

Malicious sites blocking can prevent you from accessing malicious websites, therefore preventing your computers from being infected with Trojans or abused accidentally. In conjunction with Trend Micro’s Web Reputation Services, Ai Protection assists you in identifying harmful URLs.

Trend Micro’s web reputation technology monitors the trustworthiness of online domains using one of the world’s biggest domain-reputation databases, which Trend Micro maintains.

Vulnerability Protection

Securing the growing number of Internet of Everything (IoE)-enabled devices that are becoming available online is the most pressing security concerns of the current era. There may be vulnerabilities in your IoE-enabled devices.

In most cases, IoE-enabled devices are based on ancient versions of unpatched open-source software, making them more susceptible to exploitation. Your IoE-enabled device suppliers may be hesitant to patch your devices because of the risks involved.

Incompatibilities may arise due to patching a susceptible device, resulting in the device failing to work correctly. Therefore, device manufacturers may be hesitant to offer security fixes for your devices until they have completed appropriate testing.

Moreover, your IoE-enabled device suppliers may never deliver security updates. Vendors of Internet-of-Things-enabled devices may not have given much attention to issuing security fixes for their devices, and they may never provide security patches for your gadgets.

As a result of the fact that all of your Internet of Things (IoT)-enabled devices are linked to the internet via your home network, and since IoE-enabled devices may include vulnerabilities, the need for vulnerability prevention on home routers is more than ever before.

Luckily, Asus extenders with AiProtection assist in preventing the exploitation of a known vulnerability even when the affected systems have not yet been patched with the latest security updates.

AiProtection has a built-in DPI engine that can recognize and prevent known assaults before the attacking packets reach the susceptible connected devices. It also prevents malicious communication from reaching IoE-enabled devices, ensuring that they are never compromised.

Detect and Block Infected Devices

An infected host will connect invisibly to a malicious server, commonly known as a Command-and-Control server, to receive orders from the attacker when infected with a bot or Trojan.

This host machine gets transformed into a zombie computer for the Botnet. The rogue server provides the attacker with the ability to take command of the compromised host. Then, the attacker can also steal the victim’s sensitive information.

If the device’s log reveals that a host attempted to connect to a malicious server but was denied access, this is an indicator that the host has been infected with malware.

So, Asus WiFi extenders with AiProtection assist you in identifying the Command-and-Control server by sending you an alert email. Also check out, how to secure your online accounts.

The Bottom Line

Asus WiFi extenders offer fast, stable, and secure internet connections. AiProtection continuously monitors the security and safety of your home network. In sum, Asus extenders truly protect your home network.

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-90908CVSS 9.3
    A vulnerability in the GenericAdminAuthenticator component of Azul Payara Server and Azul Payara Micro allows a remote, unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-110003CVSS 9.3
    A vulnerability in the administration REST interface of Azul Payara allows a remote, unauthenticated attacker to bypass secure-admin...
    📅 Updated: Nov 12, 2026
  • CVE-2026-8333CVSS 9.4
    A stored cross-site scripting vulnerability in Microchip the TimePictra platform could allow an authenticated, low-privileged attacker to store...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12591CVSS 9.9
    Zohocorp ManageEngine M365 Manager Plus versions below 4818 is affected by an authenticated technician may exploit insufficient permission validation in the delegated administration...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12507CVSS 9.1
    Zohocorp ManageEngine AssetExplorer versions below 7860, ServiceDesk Plus versions below 15290, ServiceDesk Plus MSP versions below 15150, and...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107935CVSS 9.3
    A path traversal vulnerability was found in gvproxy, the network forwarder provided by the gvisor-tap-vsock package. The unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-125883CVSS 9.3
    Improper restriction of XML external entity reference vulnerability in N-able N-central allows XML Schema Poisoning. This issue affects...
    📅 Updated: Nov 12, 2026
  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 12, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.