Skip to content
October 29, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Data Leak
  • Hackers openly sell Nvidia LHR algorithm source code
  • Data Leak

Hackers openly sell Nvidia LHR algorithm source code

Do Son March 3, 2022 2 minutes read
Nvidia LHR algorithm source code
Add Daily CyberSecurity as a preferred source on Google

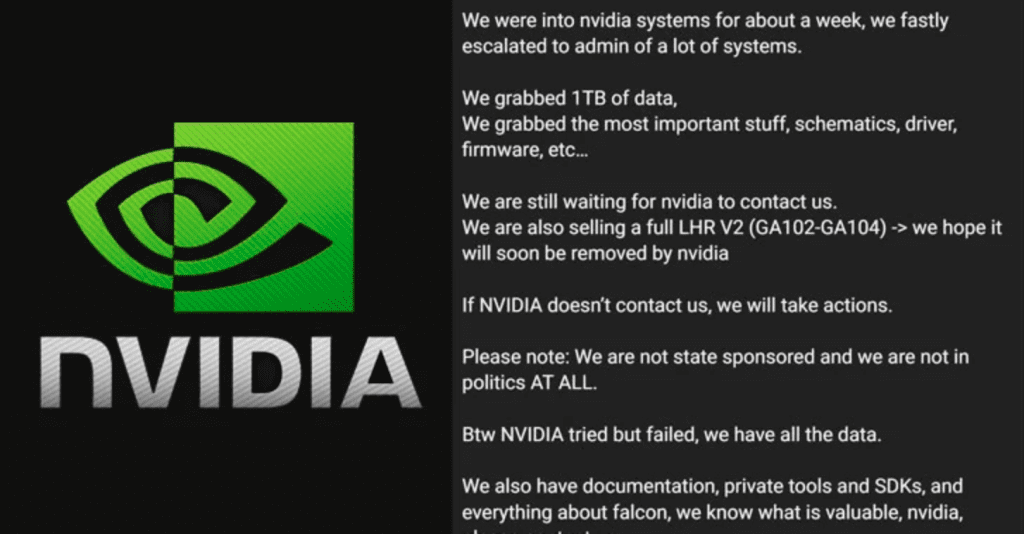
After some tossing, Nvidia has not had any contact with the South American hacker group Lapsus Group. The delusional ransom of this hacker group is naturally out of the question, so now the hackers are ready to publicly sell the Nvidia LHR algorithm source code.

The value of this source code may be useful to Ethereum miners. The LHR algorithm is expected to crack the mining restrictions imposed by NVIDIA on the RTX 30 series graphics cards and restore the hash rate from the limited 50% to the normal state, which is 100%, which can significantly speed up the mining efficiency of miners.

Nvidia has issued a response yesterday saying that the data stolen by hackers will not affect the normal operation of Nvidia’s business. Of course, even so, the confidential data stolen by hackers will still have potential impacts, including but not limited to LHR algorithms, NVIDIA’s various designs, driver and firmware source codes, etc.

At present, the hacker has published an open message on his Telegram channel to sell the LHR source code for $1 million, of course, with a slight discount. “We request that NVIDIA commits to completely open-source (and distribute under a FOSS license) their GPU drivers for Windows, macOS, and Linux, from now on and forever,” the cybercriminals posted on their Telegram group. It is difficult to say whether miners will buy it eventually, the price is too high for individual miners and there is no technical ability to lift the restriction. Buying such copyrighted content can be sued by companies, so it is too risky to buy.

It is worth noting that the hackers even asked Nvidia to open source the graphics card drivers. If Nvidia does not open source, the relevant source code stolen by the hackers will also be made public. In some respects, it would be foolish to ask Nvidia to open-source drivers, since these are proprietary software with potentially a lot of secret technology inside.

Related coverage

  • Open Access: How a Simple Fiverr Config Error Exposed 30,000 Private Documents to Google
  • AI-Driven TEMPEST Attacks: Uruguay Team Reveals Method to Intercept Screen Data
  • Facebook Launches Data Abuse Bounty Program
  • Zhao’s Bribes Unveiled: Selling US Navy’s Critical Secrets
  • Microsoft workers uploaded sensitive login credentials to Microsoft’s own systems to GitHub
  • Critical VSCode Supply Chain Flaw: 550+ Secrets Leaked Via Extensions, Exposing 100K+ Users to Malware
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: hacker Nvidia LHR algorithm source code

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
  • CVE-2026-101767CVSS 9.8
    Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-62018CVSS 9.8
    Unauthenticated PHP Object Injection in Gunslinger
    📅 Updated: Oct 29, 2026
  • CVE-2026-62131CVSS 9.8
    Unauthenticated PHP Object Injection in Zoho Flow
    📅 Updated: Oct 29, 2026
  • CVE-2026-62017CVSS 9.8
    Unauthenticated PHP Object Injection in Good Homes
    📅 Updated: Oct 29, 2026
  • CVE-2026-62016CVSS 9.8
    Unauthenticated PHP Object Injection in Gamic
    📅 Updated: Oct 29, 2026
  • CVE-2026-62015CVSS 9.8
    Unauthenticated PHP Object Injection in Gamezone
    📅 Updated: Oct 29, 2026
  • CVE-2026-62014CVSS 9.8
    Unauthenticated PHP Object Injection in EmojiNation
    📅 Updated: Oct 29, 2026
  • CVE-2026-62013CVSS 9.8
    Unauthenticated PHP Object Injection in Edge Decor
    📅 Updated: Oct 29, 2026
  • CVE-2026-62012CVSS 9.8
    Unauthenticated PHP Object Injection in Coinpress
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.