Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • iSeePassword Dr.PDF: A Simple Yet Effective Way to Crack PDF Password
  • Technique

iSeePassword Dr.PDF: A Simple Yet Effective Way to Crack PDF Password

Do Son January 11, 2021 5 minutes read
settings

Securing important PDFs with a password is a great way to ensure your data and privacy remains invulnerable. However, there are times when a password-protected PDF document becomes a cause of annoyance. In fact, if you lose or forget the password, you cannot access your data, which is pretty frustrating.

If you do some googling, you should find many PDF password recovery tools, but keep in mind that a lot of them are scams to take your money. Falling for one of these guys, you might end up losing the use of your PDF file and your important notes fall into the wrong hands. Edit, merge, convert, compress, sign & secure your documents in just a few clicks with SODAPDF.

Using a third-party service is not ideal for all users out there. However, if you have exhausted all the possibilities, but nothing works, this could be an option. We have tried iSeePassword Dr.PDF and it worked like a charm. iSeePassword successfully cracked open our PDF files with no problems and no hidden fees, so we feel confident in recommending it. 

Why Not Using Command Line-based PDF Cracking Tool

Cracking PDF password is not a new topic and dozens of tools are available for download. However, most of them are command line based, such as Hashcat, PDFCrack, or John the Ripper. One of the biggest disadvantages for command line tools is that you have to extract the hash value from PDF first. This is not something we recommend to you as it is boring and sometimes does not work for everybody. 

Cons of Command Line PDF Password Cracker:

  • Not able to extract hash from PDF file.
  • Does not support 256-bit PDF encryption.
  • Complex and risky command line parameters.
  • Time consuming process.

But this is not the case for iSeePassword Dr.PDF, all of the necessary steps are done under a simple user interface.

So, What is iSeePassword Dr. PDF and How Does it Work?

Dr.PDF stands out as one of the most effective ways to crack or recover PDF passwords. However, it is not limited to recovering your PDF password as it is a bigger deal than you think. In fact, the tool also includes the ability to remove PDF copying, editing, printing restrictions you impose on your PDF file. 

Unlike other PDF cracking tools, Dr.PDF cracks open your PDF password using 4 configurable attacks, which guarantees to get the job done. These attacks include Brute-force Attack, Brute-force with Mask Attack and Dictionary Attack. While Brute-force attack scans all possible passwords to open your PDF, the other two search passwords based on your custom settings. 

More features include:

  • Multi-core CPU Processing: Dr.PDF takes advantage of your computer’s high-speed CPU to boost the password recovery process without compromising the overall performance.
  • GPU Acceleration: Dr.PDF includes a support for the GPU Acceleration feature that allows for 10x faster cracking speed. 
  • Batch Remove: The tool allows you to import multiple PDF files and remove the passwords at the same time
  • Continue Last Searching History: The tool offers an automatic saving feature that ensures your last searching history remains available. 
  • Cross-platform support: It works on latest Windows 10 and macOS Big Sur.


How to Crack PDF Password with Dr.PDF

The process is so simple and completely safe. You can follow our step below. 

Step 1: Download iSeePassword Dr.PDF from its official page The tool now offers a free trial that lets you enjoy its full premium features without any hidden fees. 

Step 2: Once the download is complete, install it on your computer. To do this, just follow the on-screen prompts.

Step 3: From its main user interface, you will be presented with two cracking options: Recover Open Password from PDF and Remove Owner Password from PDF.

Step 4: Select Recover Open Password from PDF and click the Add File button to import your password-protected PDF file. 

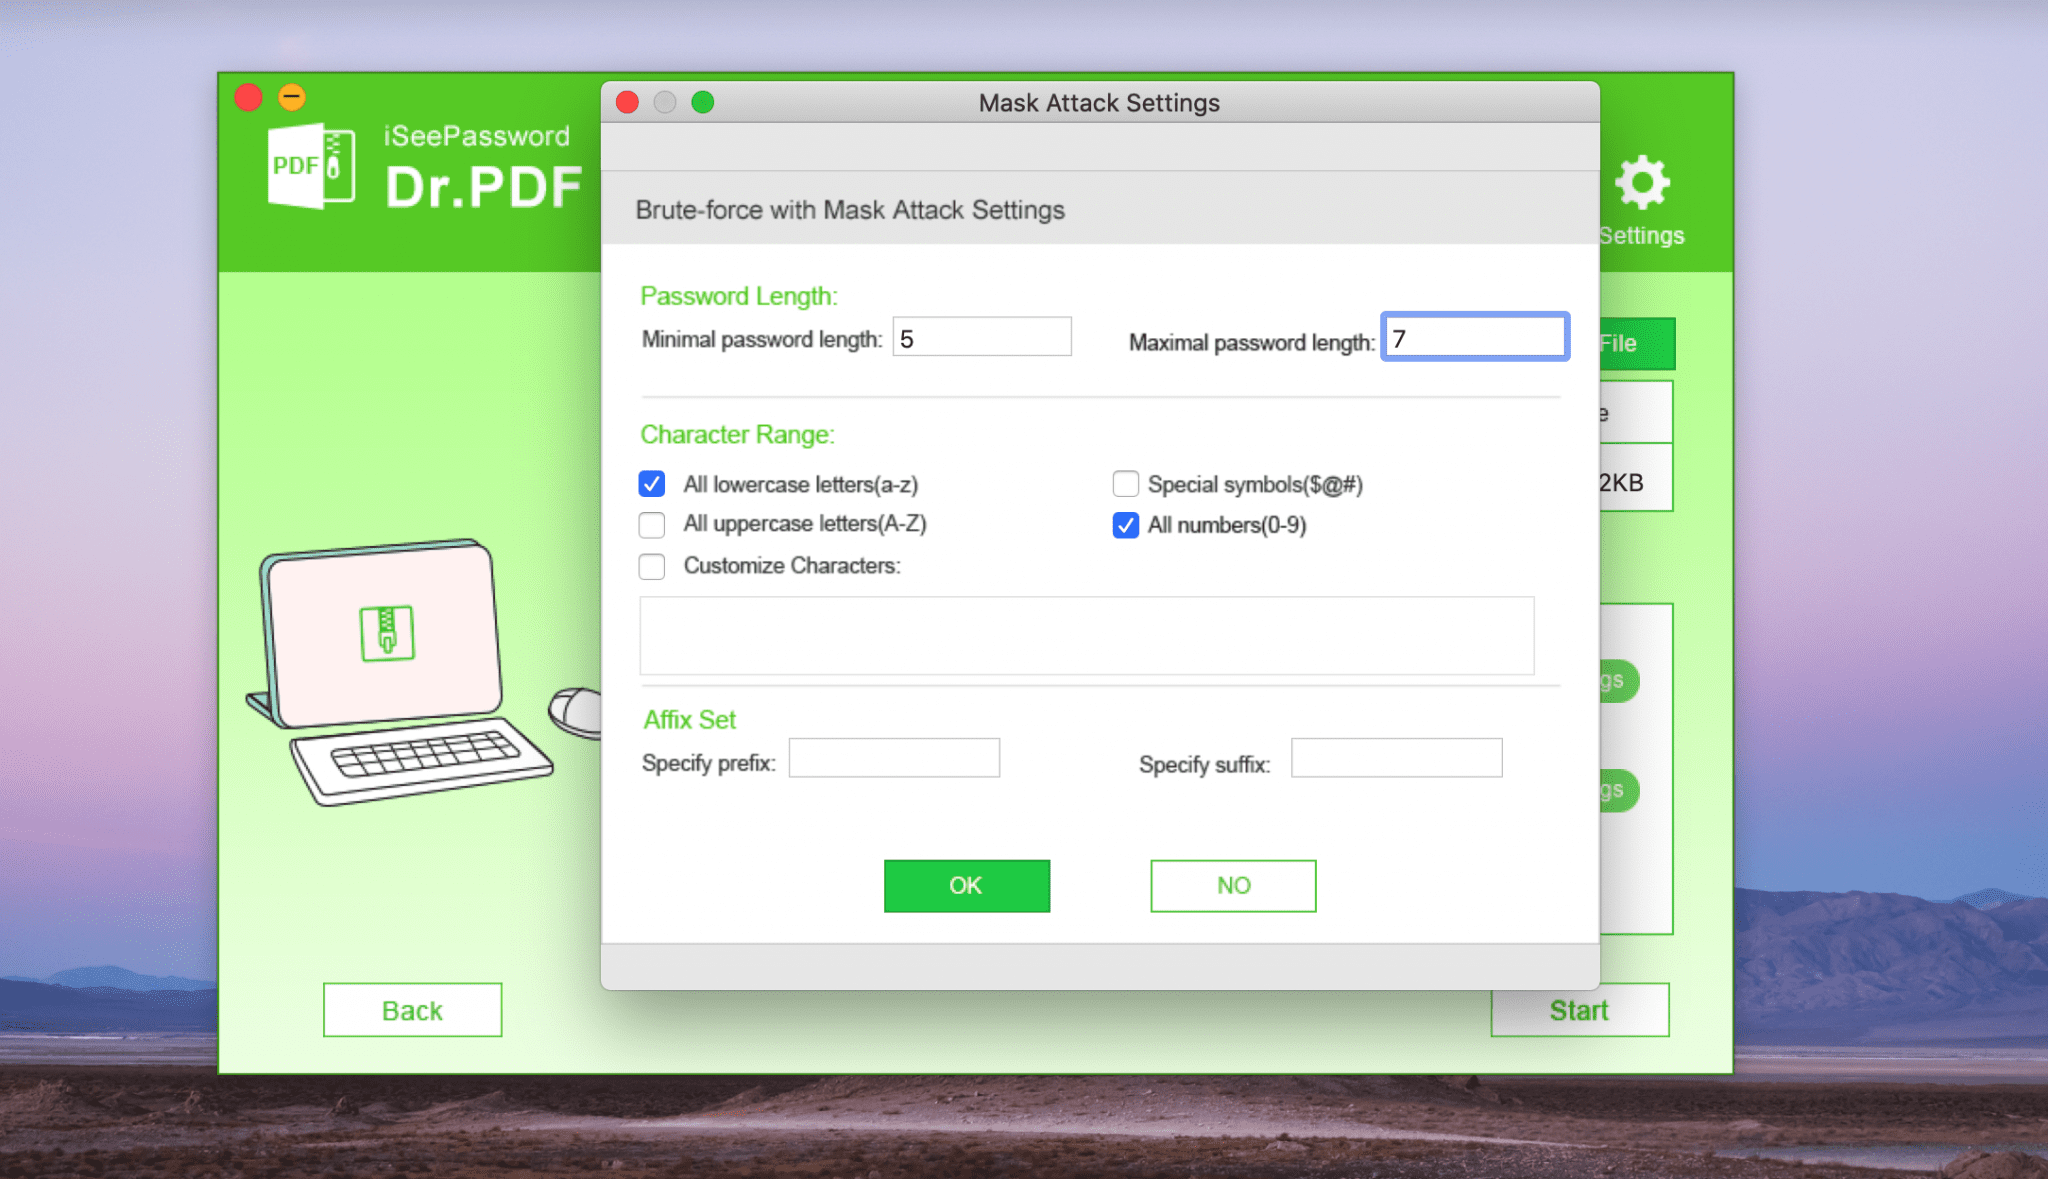
Step 5: Now, select the Attack type from the list. If you have no clues about your old password, go for Brute Force attack, but this may take longer than usual. Once you are done, hit the Start button.  For Mask attach, you can set a number of parameters to accelerate the password cracking process.

Step 6: The process should begin. As mentioned above, if you have a computer with multi-core CPU, it may take seconds. Once it is done, you can use the newly-recovered password to access your PDF file. 
Note: If you forget the owner password of the PDF file, you are restricted to viewing its content. In this case, you need to remove the owner password so that you can edit the file. To do this, select tRemove Owner Password from PDF option from the main menu, then select your file. After that, select where you want to save your PDF file and proceed with hitting the Start button. 

The Bottom Line

Accessing a password-protected PDF file has become much easier thanks to Dr. PDF. It’s reliable, fast, and won’t damage your data. The coolest part is that it supports all types of PDF password and uses the safe method to crack open your file. If you are now in the market for a trusted PDF cracking tool, iSeePassword Dr.PDF is our number one recommendation.

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2017-20287CVSS 8.7
    Javo Spot theme for WordPress before 3.0.0 contains a path traversal vulnerability that allows unauthenticated attackers to read...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2017-20288CVSS 5.1
    QCubed 2.2.0 through 3.1.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject scripts through...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2017-20289CVSS 7.7
    Broadstreet Ad Widget plugin for WordPress 2.2.0 before 2.12.0 contains a local file inclusion vulnerability that allows authenticated...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115324CVSS 9.2
    mem0 0.1.117 before 1.0.8 contains an sql injection vulnerability in mem0/vector_stores/databricks.py that allows attackers to inject SQL by...
    📅 Updated: Oct 22, 2026
  • CVE-2021-48016CVSS 9.3
    DedeCMS through 5.8.1-beta contains a PHP code injection vulnerability in ShowMsg() where the HTTP Referer header is written...
    📅 Updated: Oct 22, 2026
  • CVE-2021-48014CVSS 9.3
    FineReport 9.0 contains a path traversal vulnerability in the /WebReport/ReportServer design_save_svg operation that allows unauthenticated attackers to write...
    📅 Updated: Oct 22, 2026
  • CVE-2026-112327CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in TMS Amelia ameliabooking allows...
    📅 Updated: Oct 22, 2026
  • CVE-2026-112241CVSS 9.8
    Authentication Bypass by Spoofing vulnerability in Brainstorm Force SureCart surecart allows Authentication Abuse.This issue affects SureCart: from n/a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-15143CVSS 9.3
    A flaw was found in the file_type content detector of guardrails-detectors. This vulnerability allows a remote attacker to...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114220CVSS 9.3
    NT OneAPP developed by NewType Infortech has an Improper Certificate Validation vulnerability. Unauthenticated network-adjacent attackers can perform a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114219CVSS 9.1
    NT OneAPP developed by NewType Infortech has a Hard-coded Credentials vulnerability. Unauthenticated remote attackers can obtain the hard-coded...
    📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.