Skip to content
November 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Data Leak
  • NB65 leaked the Kaspersky antivirus source code
  • Cyber Security
  • Data Leak

NB65 leaked the Kaspersky antivirus source code

Do Son March 9, 2022 3 minutes read
Kaspersky antivirus source code

The international hacker organization Anonymous announced a cyberwar against Russia after Russia attacked Ukraine. At present, Anonymous has hacked several Russian government websites. Most of these attacks just make these websites inaccessible, but there are also serious consequences, such as the theft of some Russian government websites and bank data.

On February 28, the Anonymous affiliate group Network Battalion 65 (NB65) attacked the Russian Institute for Nuclear Security, stealing 40,000 documents and containing certain sensitive data. At that time, the autonomous system of a Russian operator was also attacked, which hosted a large number of information systems of Russian government organizations and even military departments.

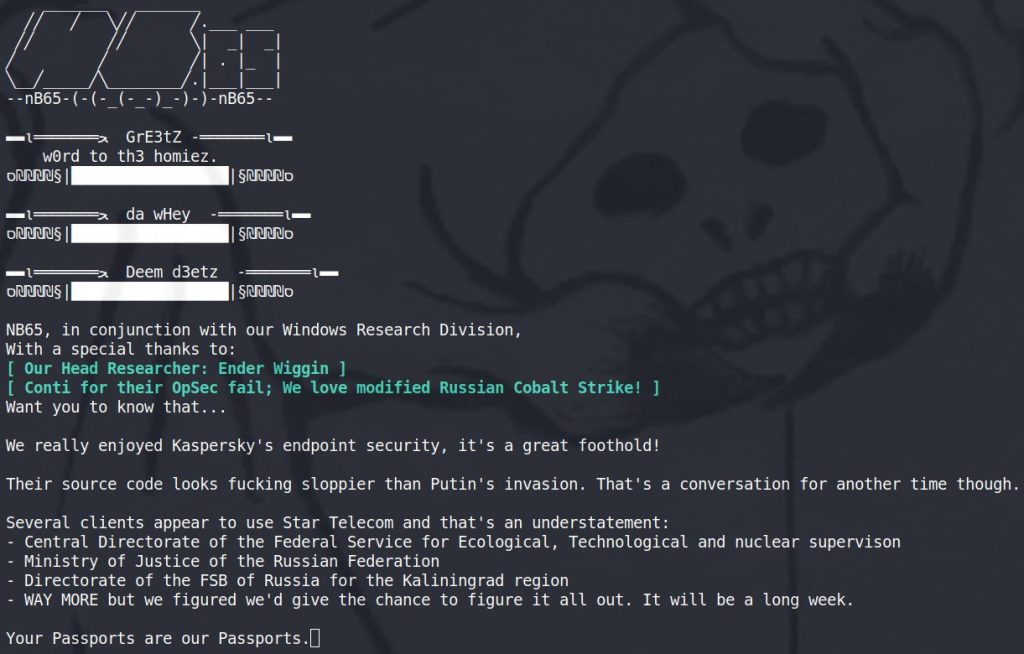
Some content related to Kaspersky can also be seen in the autonomous system, and it is suspected that Kaspersky provides security services for these websites and information systems. The latest news is that the hacker group has stolen the Kaspersky antivirus source code, and the screenshots released by the hackers show that the successful intrusion time is March 7, 2022.

Last night, NB65 released a message saying that please wait patiently for the Kaspersky source code to be released, and then released a message saying that everyone will see interesting code.

Stay tuned for Kaspersky source code leak. #Ukraine️

— NB65 (@xxNB65) March 8, 2022

Previously released screenshots can see the words Kaspersky’ Endpoint security, it is not clear whether the system will be leaked or the source code of antivirus software. The hacker has announced in advance that the stolen data will be released within 12 hours.

Update 1: NB65 released the Kaspersky antivirus source code

@Nb65Lead @ITarmyUA @YourAnonNews pic.twitter.com/09I80UTm14

— NB65 (@xxNB65) March 10, 2022

Update 2: 

After downloading the files and reviewing them, we simply looked at the data and found no sensitive data. A large amount of data is stored in various sub-sites of Kaspersky, including webpage codes, security patches, certain configuration files, certain documentation, etc. Some of these data may be regarded as Kaspersky’s corporate trade secrets, but they have absolutely nothing to do with sensitive or confidential data and source code.

After the data download address was made public, a security boss @S0ufi4n3 who was active on Twitter quickly checked it and then tweeted that it was a good way to attract attention. Another Twitter user @dmknght also believes that the hacker is purely to gain attention, because the data released has no value, and it has nothing to do with the so-called source code. He said that 90% of the data are index.html and robots.txt, and other files can be found on the PC where Kaspersky is installed.

Recently, due to the successive hacking of Nvidia and Samsung and the leakage of a large amount of sensitive data, the security industry has paid attention to all Kaspersky-related news.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • APT29 Targets European Diplomats with Wine-Themed Phishing
  • SloppyLemming’s Espionage Campaign Targets South Asia
  • Cyber Threats Intensify in Mexico: Insights from Mandiant on Espionage and Extortion
  • Cyber Attack Disrupts Operations at Australian Ports
  • Romance Scammers Target Cryptocurrency Investors with Social Engineering and Fake Exchanges
  • CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Kaspersky antivirus source code

🚨 Active Exploits in the Wild

  • CVE-2026-123890CVSS 9.8
    A malicious actor with network access to vCenter may exploit this issue to bypass authentication and gain unauthorized...
    Watchtower Verified📅 Updated: Nov 19, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-115560CVSS 9.2
    Session serializer mismatch can lead to remote code execution. PHP's session upload progress feature can write attacker-controlled data...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129182CVSS 9.2
    Use-after-free via repopulation of last_fatal_error_backtrace global after shutdown. As part of CVE-2026-109619 (GHSA-6wmf-4rv5-p3rp), PHP 8.5.12 fixes a generic...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129496CVSS 9.2
    Timezone cache use-after-free can lead to remote code execution. PHP can retain a reference to a freed timezone...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129481CVSS 9.2
    Use-after-free after interrupted session shutdown. PHP can retain a pointer to a script filename after session shutdown is...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129474CVSS 9.2
    Use-after-free in magic method backtraces can lead to remote code execution. PHP can access freed memory when collecting...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129289CVSS 9.2
    PHP-FPM request smuggling through an unread HTTP request body. PHP can fail to discard unread bytes from an...
    📅 Updated: Nov 19, 2026
  • CVE-2026-126714CVSS 9.2
    Partially overwritten session files can lead to remote code execution. PHP's file-based session handler can leave a session...
    📅 Updated: Nov 19, 2026
  • CVE-2026-123890CVSS 9.8
    A malicious actor with network access to vCenter may exploit this issue to bypass authentication and gain unauthorized...
    📅 Updated: Nov 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.