Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
FreeBSD DHCP Client Flaw Opens Door to Remote Code Execution as Root Privilege FreeBSD Wi-Fi RCE Vulnerability CVE-2026-45255 Patch FreeBSD dhclient Root Exploit CVE-2026-42511 FreeBSD Vulnerability - CVE-2024-7589 FreeBSD Jail Escape CVE-2025-15576
  • Vulnerability Report

FreeBSD DHCP Client Flaw Opens Door to Remote Code Execution as Root Privilege

Do Son May 4, 2026 0

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!

Active Exploitation in the Wild: Critical Qinglong Bypasses Fuel Covert Cryptomining Campaign Qinglong Vulnerability Active Exploitation GhostGrab Hybrid Malware, Monero Mining
  • Vulnerability Report

Active Exploitation in the Wild: Critical Qinglong Bypasses Fuel Covert Cryptomining Campaign

Do Son May 4, 2026 0

Snyk warns of active in-the-wild exploitation of the Qinglong platform. Two authentication bypass flaws grant attackers RCE to deploy .fullgc cryptominers.
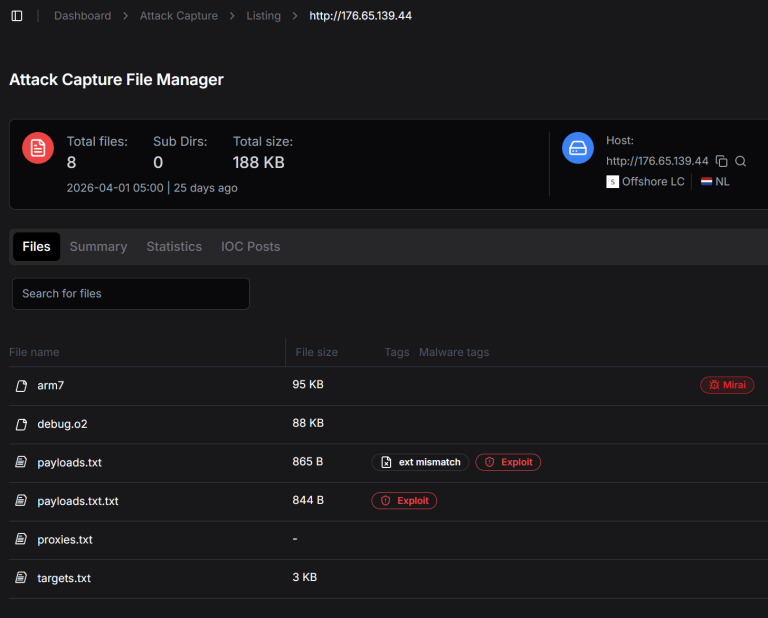
The Tadashi Files: Inside the xlabs_v1 Botnet Targeting 4 Million Android Devices xlabs_v1 Botnet ADB Port 5555 Exploit
  • Malware

The Tadashi Files: Inside the xlabs_v1 Botnet Targeting 4 Million Android Devices

Do Son May 3, 2026 0

Hunt Intelligence dismantles xlabs_v1, a Mirai-derived botnet targeting 4M Android devices via port 5555. See how an exposed server leaked the entire toolkit.
40,000+ Sites Exposed: Critical 9.8 CVSS Flaw Grants Total WordPress Account Takeover WordPress Account Takeover CVE-2026-7567
  • Vulnerability Report

40,000+ Sites Exposed: Critical 9.8 CVSS Flaw Grants Total WordPress Account Takeover

Do Son May 2, 2026 0

A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
Cybersecurity Pros Sentenced for Running ALPHV BlackCat Ransomware ALPHV BlackCat Affiliates Ransomware Insider Threat
  • Cybercriminals

Cybersecurity Pros Sentenced for Running ALPHV BlackCat Ransomware

Do Son May 2, 2026 0

Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.
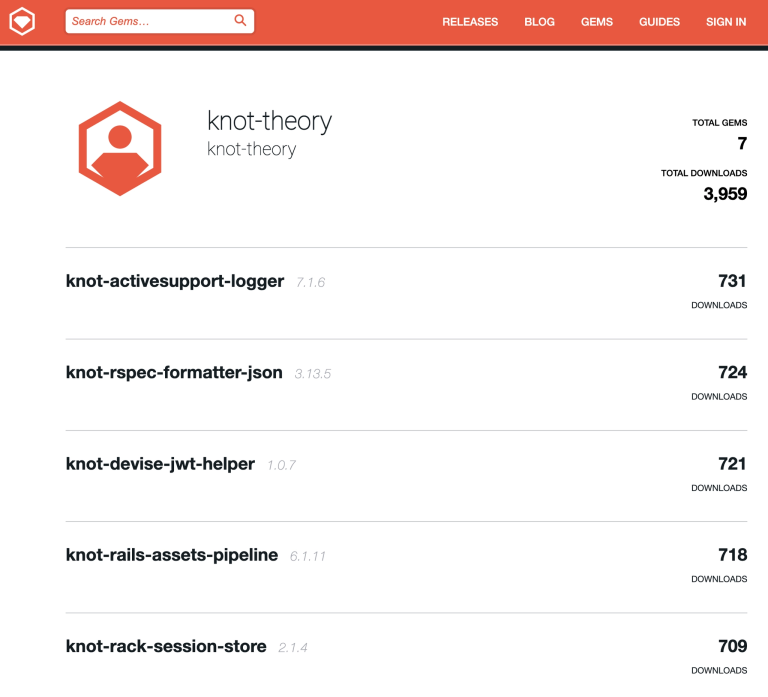
Waking the Sleepers: The BufferZoneCorp Campaign Poisoning Ruby and Go Ecosystems BufferZoneCorp Supply Chain Go and Ruby Malware
  • Malware

Waking the Sleepers: The BufferZoneCorp Campaign Poisoning Ruby and Go Ecosystems

Do Son May 2, 2026 0

Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!

The Fall of Versus: Dark Web Mastermind Extradited to the US to Face Life Behind Bars Versus Project Dark Web Extradition
  • Cybercriminals

The Fall of Versus: Dark Web Mastermind Extradited to the US to Face Life Behind Bars

Do Son May 2, 2026 0

The alleged mastermind behind the massive "Versus Project" dark web market has been extradited to the US. He faces life in prison for cybercrime and drugs.
AI’s Supply Chain Nightmare: The Lightning Framework Worm and the “Silence Developer” Meme Lightning Framework Attack TEAM PCP Supply Chain
  • Malware

AI’s Supply Chain Nightmare: The Lightning Framework Worm and the “Silence Developer” Meme

Do Son May 2, 2026 0

Lightning framework v2.6.2 & 2.6.3 are malicious. The "TEAM PCP" worm steals cloud secrets and poisons repos. Downgrade to 2.6.1 and rotate keys immediately!

“TanStack”: Malicious Name-Squatting Campaign Steals Environment Secrets TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

“TanStack”: Malicious Name-Squatting Campaign Steals Environment Secrets

Do Son May 2, 2026 0

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.
The Worm Turns to PHP: Mini Shai-Hulud’s 20-Million-Install Hijack of Intercom Mini Shai-Hulud Packagist Supply Chain Attack
  • Malware

The Worm Turns to PHP: Mini Shai-Hulud’s 20-Million-Install Hijack of Intercom

Do Son May 2, 2026 0

Socket uncovers a massive Mini Shai-Hulud breach in the Intercom PHP SDK. Malicious version 5.0.2 steals cloud secrets and GitHub tokens. Rotate keys now!

Active In-The-Wild Exploit: “Copy Fail” Grants Root Privileges on Millions of Linux Systems Copy Fail CVE-2026-31431 Linux Root Privilege Exploit
  • Vulnerability Report

Active In-The-Wild Exploit: “Copy Fail” Grants Root Privileges on Millions of Linux Systems

Do Son May 2, 2026 0

CISA warns "Copy Fail" (CVE-2026-31431) is exploited in the wild. Millions of Linux systems since 2017 are vulnerable to instant root privilege takeover.
44,000 IPs Hijacked: cPanel’s 9.8 CVSS Authentication Bypass Triggers Global Ransomware Surge cPanel Authentication Bypass CVE-2026-41940
  • Vulnerability Report

44,000 IPs Hijacked: cPanel’s 9.8 CVSS Authentication Bypass Triggers Global Ransomware Surge

Do Son May 2, 2026 0

CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!

Criminal IP and Securonix ThreatQ Collaborate to Enhance Threat Intelligence Operations 1200_700_1776732787DlSbx2MTHb
  • Press Release

Criminal IP and Securonix ThreatQ Collaborate to Enhance Threat Intelligence Operations

cybernewswire May 1, 2026 0
Torrance, United States / California, 1st May 2026, CyberNewswire
Read More Read more about Criminal IP and Securonix ThreatQ Collaborate to Enhance Threat Intelligence Operations
Crashing the Shield: The One-Line Script Taking Down ModSecurity v3 WAFs libmodsecurity3 Denial of Service WAF Security Vulnerability CVE-2025-27110 ModSecurity vulnerability, JSON DoS
  • Vulnerability Report

Crashing the Shield: The One-Line Script Taking Down ModSecurity v3 WAFs

Do Son May 1, 2026 0

libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.

Operation Road Trap: Inside the 79,000-Message Smishing Wave Hitting Drivers Worldwide Smishing Operation
  • Cybercriminals

Operation Road Trap: Inside the 79,000-Message Smishing Wave Hitting Drivers Worldwide

Do Son May 1, 2026 0

Bitdefender uncovers a massive smishing campaign targeting drivers with fake toll and parking fines. Over 79,000 messages sent across 12 countries.
New DDoS Botnet Exploits Jenkins to Target Gaming Servers Jenkins DDoS Botnet Gaming Industry Cyberattacks
  • Malware

New DDoS Botnet Exploits Jenkins to Target Gaming Servers

Do Son May 1, 2026 0

Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.

Unmasking the Phoenix System’s Rogue BTS Smishing Empire Phoenix System PhaaS Rogue BTS Smishing
  • Cybercriminals

Unmasking the Phoenix System’s Rogue BTS Smishing Empire

Do Son May 1, 2026 0

Group-IB unmasks the Phoenix System: a PhaaS platform using rogue cell towers and live-dashboards to bypass MFA across 2,500+ domains. Read the full report.

PromptMink Tricked AI Agents into Planting Malware PromptMink Campaign AI Agent Deception LIMINAL PANDA UNC1549 DLL Hijacking, VDI Breakout
  • Malware

PromptMink Tricked AI Agents into Planting Malware

Do Son May 1, 2026 0

ReversingLabs uncovers PromptMink: A DPRK campaign using LLM-generated npm packages to trick AI coding agents into installing crypto-stealing malware.
The 11-Step Trap: How a Fake DHL OTP Trick Steals Your Password DHL Phishing OTP Social Engineering
  • Cybercriminals

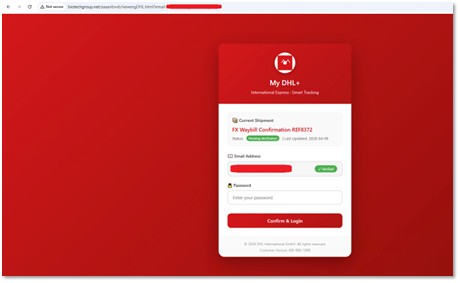
The 11-Step Trap: How a Fake DHL OTP Trick Steals Your Password

Do Son May 1, 2026 0

Forcepoint X-Labs uncovers a clever 11-step DHL phishing scam using a fake OTP interface to build trust and steal passwords. See how the trick works.
Minirat’s Stealth Supply Chain Attack Targets macOS Developers Minirat macOS Malware Go-based RAT
  • Malware

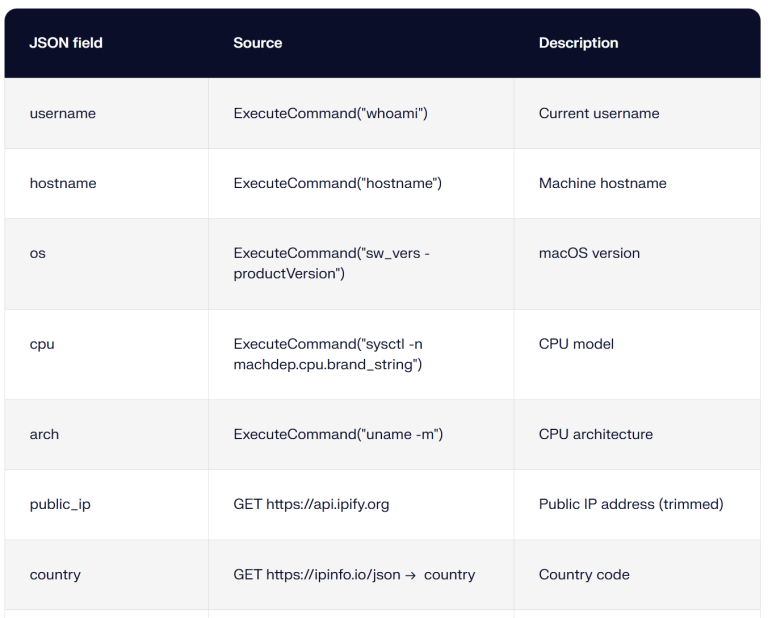
Minirat’s Stealth Supply Chain Attack Targets macOS Developers

Do Son May 1, 2026 0

Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.

Single Actor Bypassed Open VSX Security with “Disposable” Tools Open VSX Malware String-Fragment Reconstruction DarkCloud Stealer, steganography APT 35 Charming Kitten cyclops
  • Cybercriminals

Single Actor Bypassed Open VSX Security with “Disposable” Tools

Do Son May 1, 2026 0

Yeeth Security uncovers a sophisticated Open VSX campaign using string-fragment reconstruction to hide malware. 16 malicious extensions identified.

CoreDNS Security Alert: Multiple High-Severity Vulnerabilities Patched in Version 1.14.3 CoreDNS Security Encrypted DNS Vulnerabilities CoreDNS vulnerability, DNS cache poisoning
  • Vulnerability Report

CoreDNS Security Alert: Multiple High-Severity Vulnerabilities Patched in Version 1.14.3

Do Son April 30, 2026 0

CoreDNS 1.14.3 addresses 5 critical flaws in DoH, DoQ, and gRPC. Fix authentication bypasses and DoS risks by upgrading your DNS infrastructure today.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-63939CVSS 9.8
    Improper input handling in /Grocery/search_products_itname.php, in anirudhkannan Grocery Store Management System 1.0, allows SQL injection via the sitem_name...
    📅 Updated: Nov 4, 2026
  • CVE-2025-65133CVSS 9.8
    A SQL injection vulnerability exists in the School Management System (version 1.0) by manikandan580. An unauthenticated or authenticated...
    📅 Updated: Nov 4, 2026
  • CVE-2025-65135CVSS 9.8
    In manikandan580 School-management-system 1.0, a time-based blind SQL injection vulnerability exists in /studentms/admin/between-date-reprtsdetails.php through the fromdate POST parameter.
    📅 Updated: Nov 4, 2026
  • CVE-2025-70023CVSS 9.8
    An issue pertaining to CWE-843: Access of Resource Using Incompatible Type was discovered in transloadit uppy v0.25.6.
    📅 Updated: Nov 4, 2026
  • CVE-2025-70067CVSS 9.8
    Buffer Overflow vulnerability exists in Assimp versions up to 6.0.2 in the FBX Importer. The vulnerability occurs in...
    📅 Updated: Nov 4, 2026
  • CVE-2025-63703CVSS 9.8
    npm package parse-ini v1.0.6 is vulnerable to Prototype Pollution in index.js().
    📅 Updated: Nov 4, 2026
  • CVE-2025-63704CVSS 9.8
    NPM package query-parser-string 1.0.0 is vulnerable to Prototype Pollution. The package does not properly sanitize user supplied query...
    📅 Updated: Nov 4, 2026
  • CVE-2025-67887CVSS 9.8
    1C-Bitrix through 25.100.500 allows Remote Code Execution because an actor with SOURCE/WRITE permissions for the Translate Module can...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.