Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
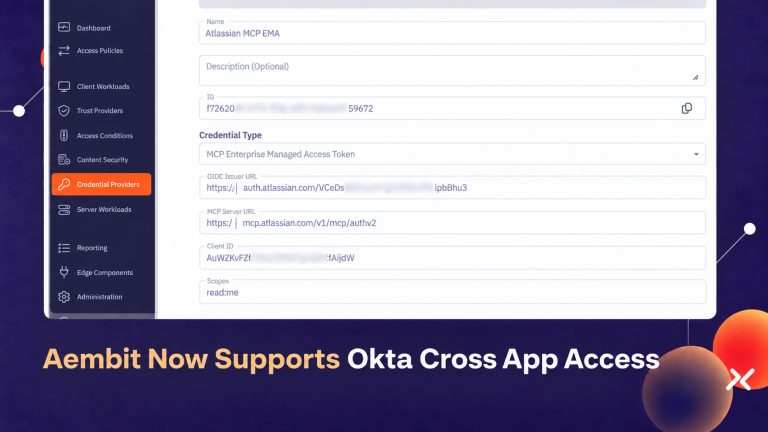
Aembit Launches Support for Okta Cross App Access, Extending Enterprise Identity Controls to AI Agents xaa_1790023632b9zu5nUa3S
  • Press Release

Aembit Launches Support for Okta Cross App Access, Extending Enterprise Identity Controls to AI Agents

cybernewswire September 22, 2026 0
Silver Spring, Maryland, USA, 22nd September 2026, CyberNewswire
Read More Read more about Aembit Launches Support for Okta Cross App Access, Extending Enterprise Identity Controls to AI Agents
Windows File History Bug Disrupts Data Backups Windows File History bug error screen and backup failure warning
  • Windows

Windows File History Bug Disrupts Data Backups

Do Son September 22, 2026 0

Discover how the recent September update caused a critical Windows File History bug. Learn about backup failures and how to protect your essential data now.
Amazon Blocks Meta Muse AI Assistant Amazon blocks Meta Muse AI shopping cart warning screen
  • Technology

Amazon Blocks Meta Muse AI Assistant

Do Son September 22, 2026 0

Discover why Amazon blocks Meta Muse AI from automated shopping. Learn about the security concerns, negotiation breakdowns, and advertising revenue impacts.
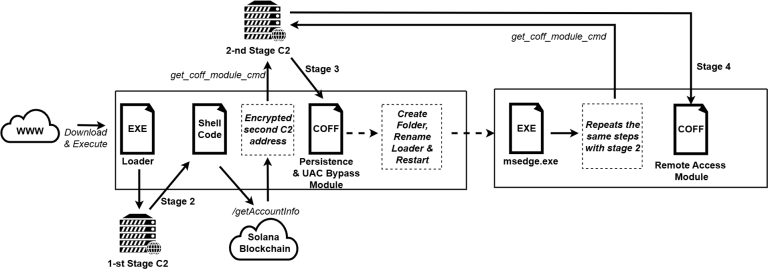
MovieReaper Malware Spreads via Compromised Torrents The MovieReaper malware torrent attacks infection chain
  • Malware

MovieReaper Malware Spreads via Compromised Torrents

Do Son September 22, 2026 0

Learn how the MovieReaper malware compromises torrents. Experts warn that MovieReaper malware torrent attacks use Solana blockchain for command and control.
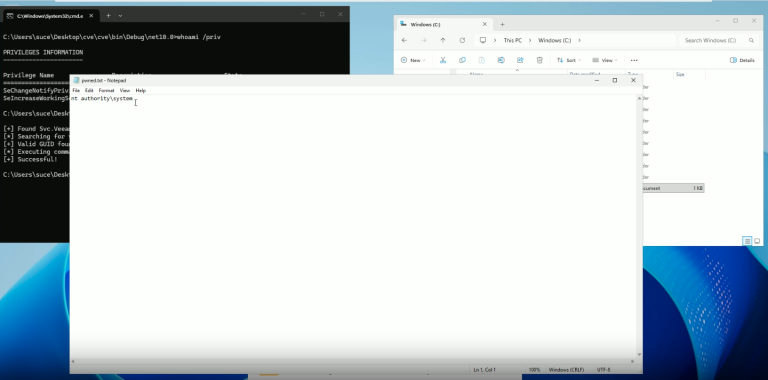
Actively Exploited Veeam Agent Vulnerability PoC Disclosed Diagram explaining the actively exploited Veeam Agent vulnerability and CVE-2026-32996
  • Vulnerability Report

Actively Exploited Veeam Agent Vulnerability PoC Disclosed

Do Son September 22, 2026 0

A critical exploited Veeam Agent vulnerability (CVE-2026-32996) is under active attack. Public PoC exploit code has been disclosed. Update systems now.
Operation RapidRust APT36 Campaign Targets Governments Half-click exploits chain showing webmail zero-days used by TA488 and TA458 against Zimbra, SOGo and Roundcube mailservers
  • Cybercriminals

Operation RapidRust APT36 Campaign Targets Governments

Do Son September 22, 2026 0

Explore how the Operation RapidRust APT36 malware campaign by Zscaler ThreatLabz exposes new tools like RUSTYSHADE and RUSTYMOVE targeting governments.
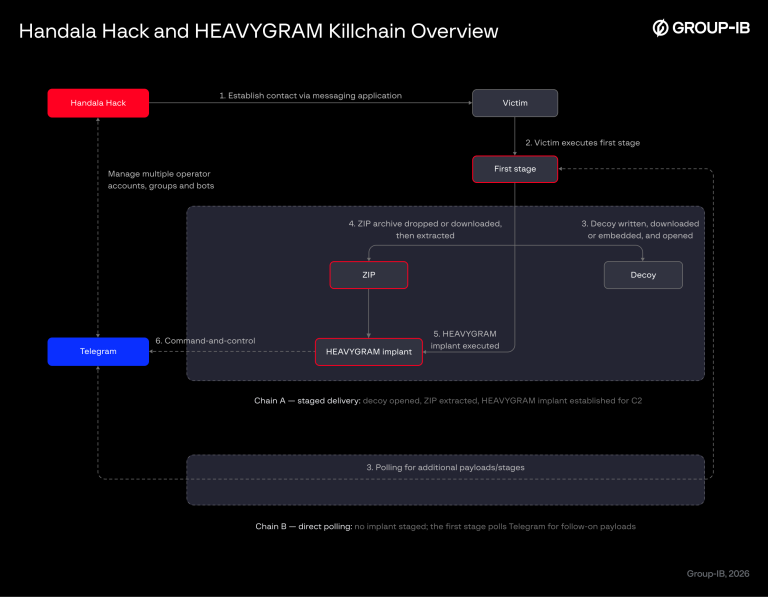
HEAVYGRAM Malware Abuses Telegram for Cyberespionage Diagram of Iranian HEAVYGRAM malware illustrating how HEAVYGRAM malware compromises endpoints
  • Malware

HEAVYGRAM Malware Abuses Telegram for Cyberespionage

Do Son September 22, 2026 0

Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
Exploited VeloCloud Vulnerability CVE-2026-93952 Hits 10 Network diagram of the exploited VeloCloud vulnerability tracked as CVE-2026-93952
  • Vulnerability Report

Exploited VeloCloud Vulnerability CVE-2026-93952 Hits 10

Do Son September 22, 2026 0

An exploited VeloCloud vulnerability with a 10.0 CVSS score hits Arista appliances. Patch the critical VeloCloud vulnerability to stop active attacks.
OpenAI Races to Counter Grok Bot and Meta’s Muse OpenAI developing personal AI agent features to counter SpaceXAI Grok Bot and Meta Muse
  • Technology

OpenAI Races to Counter Grok Bot and Meta’s Muse

Do Son September 22, 2026 0

OpenAI is building a personal AI agent to counter SpaceXAI's Grok Bot and Meta's Muse, hiring the OpenClaw creator to lead its Codex Bot effort.
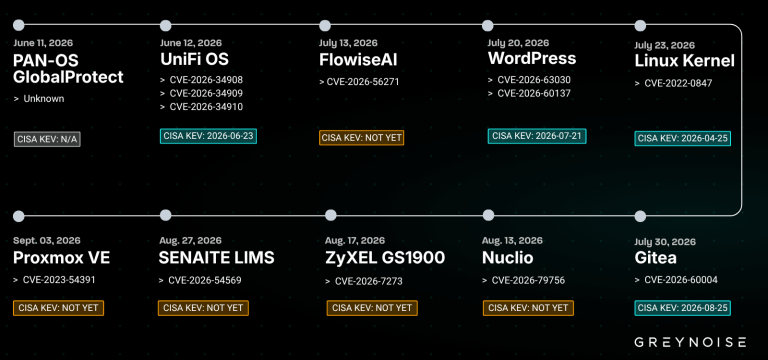
Kapibala WordPress Exploitation Attacks Hit Governments Diagram showing Kapibala WordPress exploitation attacks and Kapibala WordPress exploitation timeline
  • Cybercriminals

Kapibala WordPress Exploitation Attacks Hit Governments

Do Son September 22, 2026 0

New Kapibala WordPress exploitation attacks steal records. GreyNoise warns that Kapibala WordPress exploitation hits governments.
X Content Farm Lawsuit Targets Engagement Fraud X content farm lawsuit and creator revenue fraud investigation
  • Technology

X Content Farm Lawsuit Targets Engagement Fraud

Do Son September 22, 2026 0

Discover the details of the X content farm lawsuit. Elon Musk's social network takes legal action to recover $278,000 lost to creator revenue fraud.
DPC Imposes Massive GDPR Penalty on Google Google location data fine announcement building
  • Technology

DPC Imposes Massive GDPR Penalty on Google

Do Son September 22, 2026 0

Discover why the DPC hit Google with a 403 million euro location data fine for GDPR violations, marking a major turning point for tech privacy standards.
D-Link DIR-822A Vulnerabilities Details and PoC Disclosed Diagram of critical D-Link DIR-822A vulnerabilities and D-Link DIR-822A vulnerabilities buffer overflow flaws
  • Vulnerability Report

D-Link DIR-822A Vulnerabilities Details and PoC Disclosed

Do Son September 22, 2026 0

Public PoC exploit details emerge for critical D-Link DIR-822A vulnerabilities. Learn how these D-Link DIR-822A vulnerabilities impact unpatched devices.
Pega Platform SAML Authentication Bypass: Critical 9.5 Flaw Patched Pega Platform SAML authentication bypass advisory showing critical and high severity SSO vulnerabilities and patch remediation
  • Vulnerability Report

Pega Platform SAML Authentication Bypass: Critical 9.5 Flaw Patched

Do Son September 22, 2026 0

Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.
Exploited Zyxel Switch Vulnerability Added to CISA KEV Graphic showing an exploited Zyxel switch vulnerability tracked as CVE-2026-7273
  • Vulnerability Report

Exploited Zyxel Switch Vulnerability Added to CISA KEV

Do Son September 22, 2026 0

CISA warned of an exploited Zyxel switch vulnerability in GS1900 devices. Patch the Zyxel switch vulnerability now to prevent network compromise.
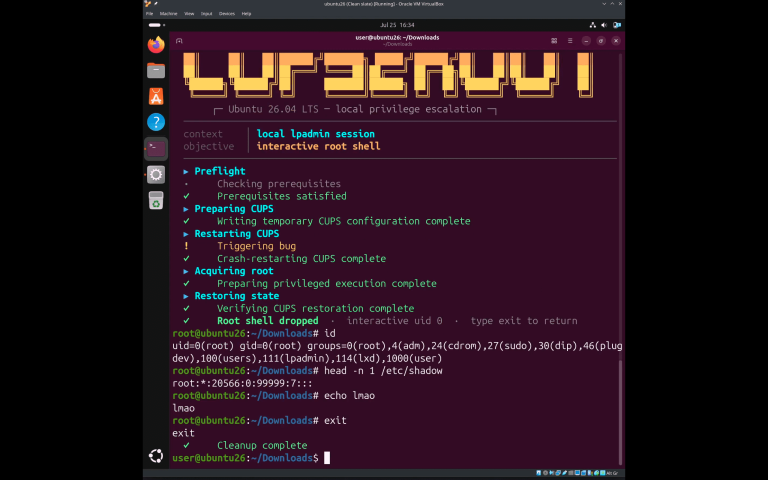
cups2root: Public PoC Exploit Escalates lpadmin to Root on CUPS cups2root CUPS privilege escalation 0-day exploit chain escalating lpadmin group to root shell on Ubuntu Linux
  • Vulnerability Report

cups2root: Public PoC Exploit Escalates lpadmin to Root on CUPS

Do Son September 22, 2026 0

A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
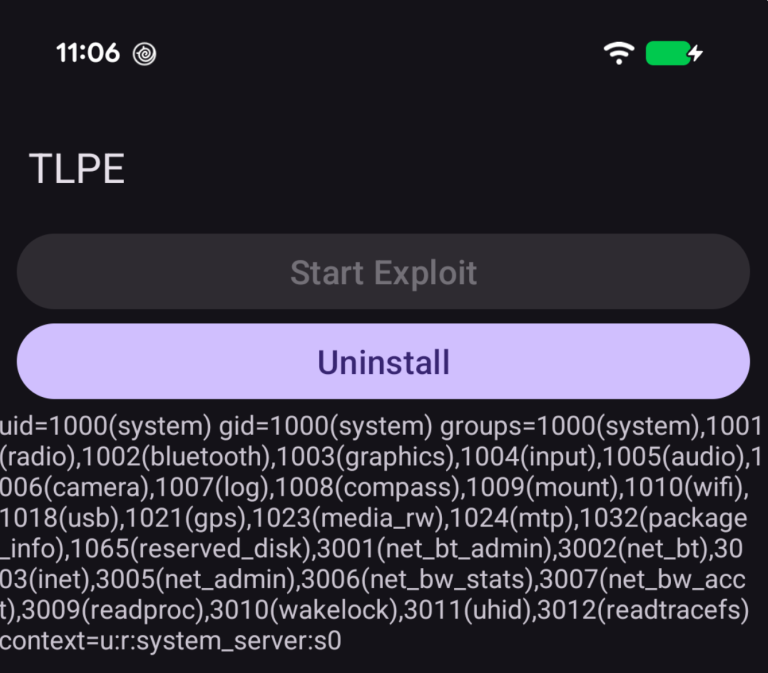
Public PoC Disclosed for Android Telecom Vulnerability CVE-2026-49881 Diagram illustrating the exploitation flow of Android Telecom Vulnerability CVE-2026-49881
  • Vulnerability Report

Public PoC Disclosed for Android Telecom Vulnerability CVE-2026-49881

Do Son September 22, 2026 0

A critical Android Telecom vulnerability (CVE-2026-49881) allows remote code execution. Read the analysis and learn how to secure your device today.
Five Network Headaches a DNS Appliance Solves in Under 30 Days AISelect_20260922_071849_Docs
  • Technique

Five Network Headaches a DNS Appliance Solves in Under 30 Days

Do Son September 22, 2026 0
If you are operating a business in the US, you will likely face several networking challenges. Some...
Read More Read more about Five Network Headaches a DNS Appliance Solves in Under 30 Days
Qualcomm and Google Unveil the Revolutionary Googlebook Snapdragon X Elite Googlebook rendering with Gemini AI
  • Technology

Qualcomm and Google Unveil the Revolutionary Googlebook

Do Son September 21, 2026 0

Discover the new Snapdragon X Elite Googlebook by Dell and HP. Experience native Android gaming, seamless cross-device synergy, and advanced Gemini AI today.
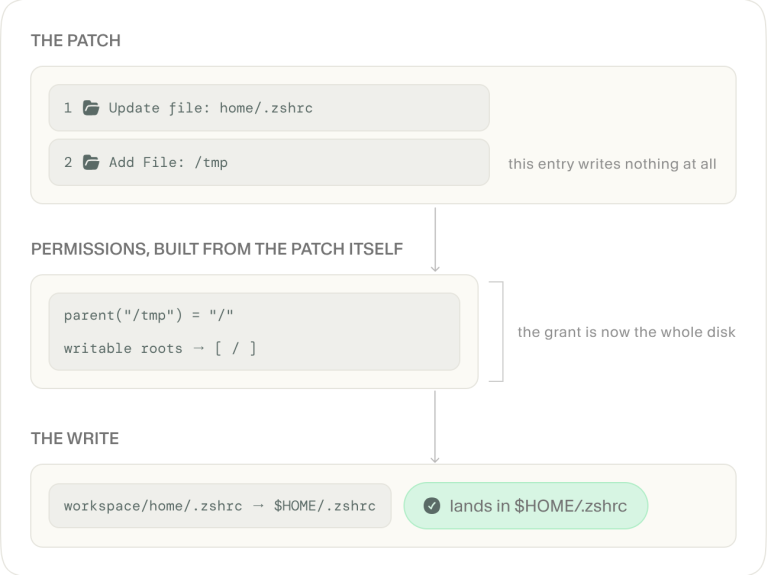
OpenAI Codex Sandbox Escape Vulnerabilities Disclosed OpenAI Codex sandbox escape diagram showing vulnerability exploit
  • Vulnerability Report

OpenAI Codex Sandbox Escape Vulnerabilities Disclosed

Do Son September 21, 2026 0

Discover the critical OpenAI Codex sandbox escape vulnerability. Learn how attackers bypass read-only modes and how to patch your CLI and desktop apps now.
Dropbox Will Delete Inactive Accounts After 6 Months Dropbox new terms of service 2027 shortening inactive account deletion to six months
  • Technology

Dropbox Will Delete Inactive Accounts After 6 Months

Do Son September 21, 2026 0

Dropbox's new terms bring inactive account deletion to 6 months from January 2027, plus same-email suspension linkage and a looser refund policy.
Spain Blocks Archive.today Over Copyright Infringement Spanish warning page blocking access to Archive today mirror sites
  • Technology

Spain Blocks Archive.today Over Copyright Infringement

Do Son September 21, 2026 0

Discover why Spain blocks Archive today over copyright claims. Learn about the impact on researchers and the controversy surrounding this snapshot platform.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-118333CVSS 9.3
    Missing authorization in Video in Google Chrome prior to 156.0.8078.73 allowed a remote attacker to bypass web origin...
    📅 Updated: Oct 30, 2026
  • CVE-2026-118337CVSS 9.3
    Improper access control in Forms in Google Chrome prior to 156.0.8078.73 allowed a remote attacker to bypass web...
    📅 Updated: Oct 30, 2026
  • CVE-2026-104339CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.3 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107327CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107328CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107329CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-110186CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.