Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • Start your cloud mining journey with one click on your smartphone, earning $7,275 a day
  • Technique

Start your cloud mining journey with one click on your smartphone, earning $7,275 a day

Do Son June 30, 2025 2 minutes read
Exploit Jupyter Notebooks

Bitcoin (BTC) broke through the $108,000 mark, an increase of about 5%. As a result, more and more people have joined the cloud mining platform. Faced with the equipment and time investment required for personal mining, they are controlled within a few hours every day. Now join Earn Mining cloud mining to experience all-weather mining without waiting. Let you use a smartphone to start a new mining process.
You can register your account with an email address, and then select the contract you need to purchase, and you can check your contract and income at any time in one stop

Why are more and more users choosing the Earn Mining platform?

Earn Mining was established in 2018 and is headquartered in London, UK. It is a cloud mining service platform with a formal license. The platform’s cooperative mining machine manufacturers include industry giants such as Bitmain and Canaan Creative, with stable computing power, energy saving and high efficiency. Most importantly, Earn Mining supports a variety of mainstream currencies such as BTC, ETH, XRP, DOGE, LTC, etc. No matter which crypto asset you prefer, you can flexibly configure your mining strategy.

Platform advantages include:

Register now: New users will receive a $15 bonus, and $0.6/day will be given for signing in

Fixed daily income, and the principal will be automatically returned at the end of the contract

No technical background is required, and automatic operation and maintenance

Minimum investment of $100, support for multi-currency settlement

6 million users worldwide, transparent and open data

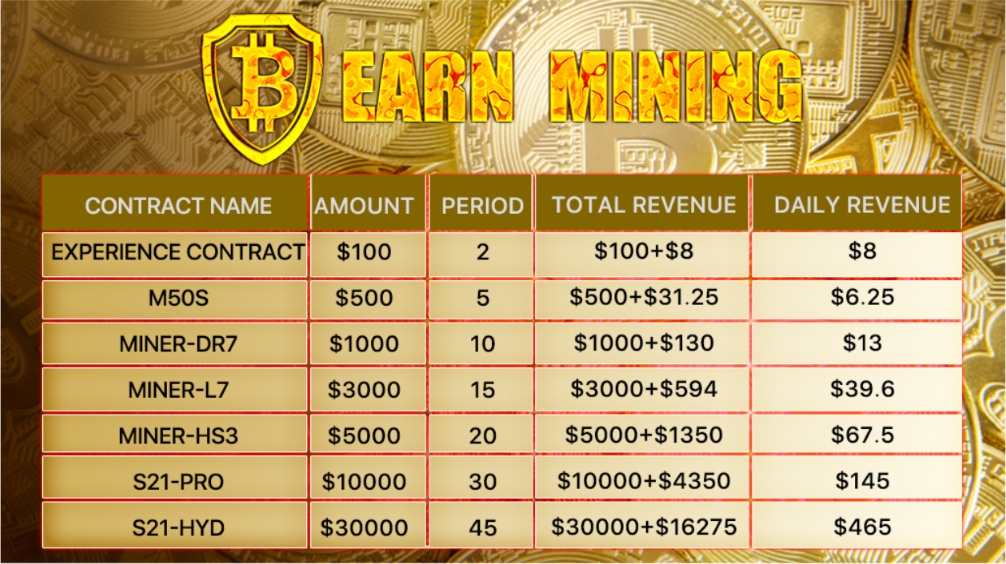
Real return display (selected contracts):
Conclusion:

Whether you are a crypto novice or an investor pursuing stable returns, Earn Mining can provide you with a safe, transparent and automated mining experience. Join us now and start your smartphone miner journey, and let passive income work for you every day.

Register now and receive a $15 free bonus >

No need to download complicated programs, you can start cloud mining with a mobile phone

Official website: https://earnmining.com/

Click to download the APP now

Customer service email: info@earnmining.com

Search

Translation

CVE ALERTS
๐Ÿ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

๐ŸŽฏ

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

๐Ÿ›ก๏ธ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

๐Ÿ™

GitHub Issues
Auto-create alert tickets without duplication.

๐Ÿ“ฌ

Weekly Digest
Clean summaries, eliminating email spam.

๐Ÿท๏ธ

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

๐Ÿ”€

Smart Routing
Route chat channels based on severity levels.

๐Ÿšจ

RBP Tracker
Early warning detection and tracking system.

Subscribe โ€“ $7/mo or try free for 14 days โ†’

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2014-125131CVSS 5.1
    DedeCMS 5.6 and 5.7 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2015-20124CVSS 8.7
    Aspose Importer & Exporter plugin for WordPress before 3.0 contains a path traversal vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2016-20102CVSS 5.1
    JavaMelody before 1.60.0 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by supplying...
    Watchtower Verified📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-112327CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in TMS Amelia ameliabooking allows...
    📅 Updated: Oct 22, 2026
  • CVE-2026-112241CVSS 9.8
    Authentication Bypass by Spoofing vulnerability in Brainstorm Force SureCart surecart allows Authentication Abuse.This issue affects SureCart: from n/a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-15143CVSS 9.3
    A flaw was found in the file_type content detector of guardrails-detectors. This vulnerability allows a remote attacker to...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114220CVSS 9.3
    NT OneAPP developed by NewType Infortech has an Improper Certificate Validation vulnerability. Unauthenticated network-adjacent attackers can perform a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114219CVSS 9.1
    NT OneAPP developed by NewType Infortech has a Hard-coded Credentials vulnerability. Unauthenticated remote attackers can obtain the hard-coded...
    📅 Updated: Oct 22, 2026
  • CVE-2026-107081CVSS 9.8
    SQL injection via identifier injection in the tableName and tableFields POST parameters of admin AJAX endpoints (admin/AJAX_lookup_handler.php, admin/AJAX_check_id.php,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Hereโ€™s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
ยฉ 2017 - 2026 Daily CyberSecurity. All Rights Reserved.