Skip to content
October 13, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • 2FA Theft

2FA Theft

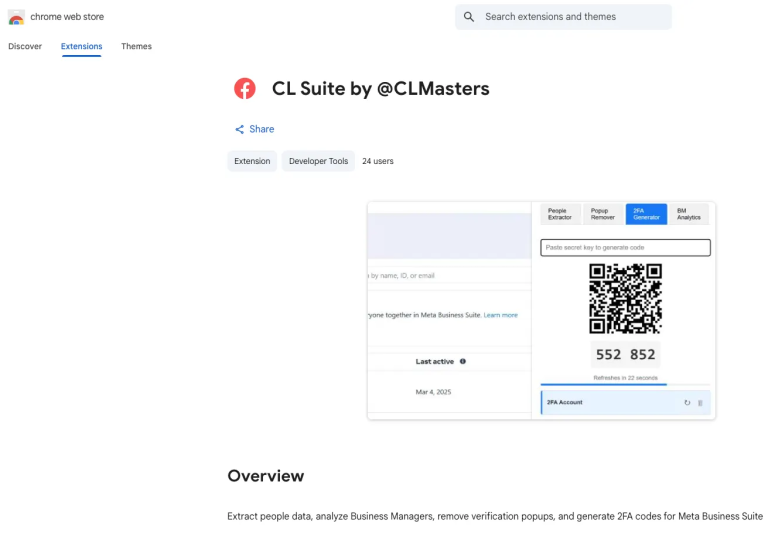
“CL Suite” Deception: Malicious Chrome Extension Steals 2FA Secrets and Meta Business Data CL Suite Malicious Extension Meta Business Suite Security
  • Malware

“CL Suite” Deception: Malicious Chrome Extension Steals 2FA Secrets and Meta Business Data

Do Son February 17, 2026 0
A malicious Google Chrome extension posing as a productivity tool for Meta Business Suite has been caught...
Read More Read more about “CL Suite” Deception: Malicious Chrome Extension Steals 2FA Secrets and Meta Business Data
Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-65173CVSS 9.1
    NVIDIA AIStore for Linux contains a missing authentication vulnerability in the token-revocation endpoint where an unauthenticated remote attacker...
    📅 Updated: Oct 13, 2026
  • CVE-2026-65162CVSS 10.0
    NVIDIA AIStore for Linux contains a vulnerability in the legacy ETL Kubernetes PodSpec initialization API where a remote...
    📅 Updated: Oct 13, 2026
  • CVE-2026-63350CVSS 9.4
    Affected devices do not properly restrict executable content contained in imported trace files. This could allow an attacker...
    📅 Updated: Oct 13, 2026
  • CVE-2026-73642CVSS 9.2
    Dayforce ESS Excelity is vulnerable to Path Traversal  in file download functionality. An unauthenticated attacker can sent GET...
    📅 Updated: Oct 13, 2026
  • CVE-2026-73640CVSS 9.3
    Dayforce ESS Excelity is vulnerable to Time Based-Blind SQL Injection in password recovery functionality. The unauthenticated attacker can...
    📅 Updated: Oct 13, 2026
  • CVE-2026-108598CVSS 9.3
    Floci 1.1.0 before 2.2.0 contains a code injection vulnerability in VtlTemplateEngine that allows unauthenticated attackers to execute commands...
    📅 Updated: Oct 13, 2026
  • CVE-2026-108549CVSS 9.2
    cc-connect through 1.5.0 contains a missing authentication vulnerability in the MAX platform adapter webhook mode in platform/max/max.go that...
    📅 Updated: Oct 13, 2026
  • CVE-2026-108268CVSS 9.1
    Enclave OS Virtual runs container workloads inside confidential virtual machines with end-to-end attestation. Prior to tdx-v0.2.43 and tdx-gpu-v0.6.27,...
    📅 Updated: Oct 13, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.