 Do Son
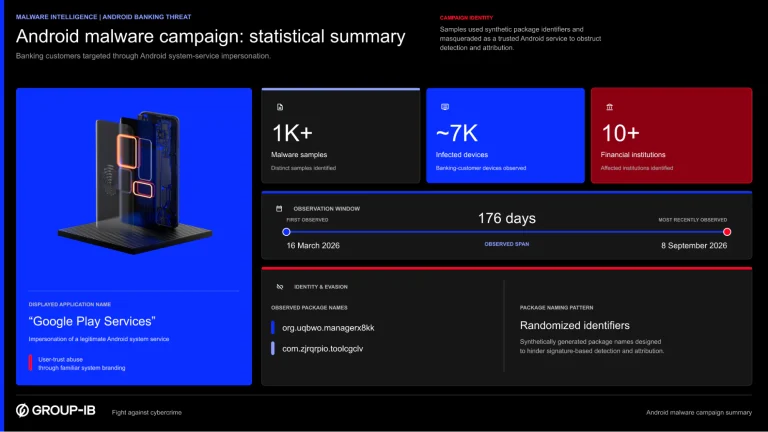
The Mirax Android RAT, a device takeover malware posing as Google Play Services, has infected thousands of phones to drain META bank accounts.
Android Banking Trojan
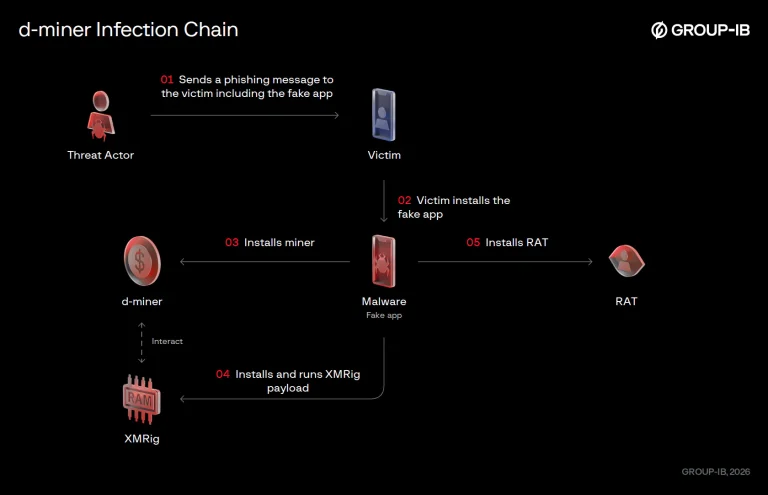
Group-IB exposes CyberDakait Android malware. The Indian CyberDakait Android malware campaign uses 7 trojans to infect 17,960 phones and steal 7.6M SMS.

A Copybara Android RAT campaign impersonates N26 in Italy. Vishing calls and a Fake Control 1.0 phishing panel push the malware onto phones.
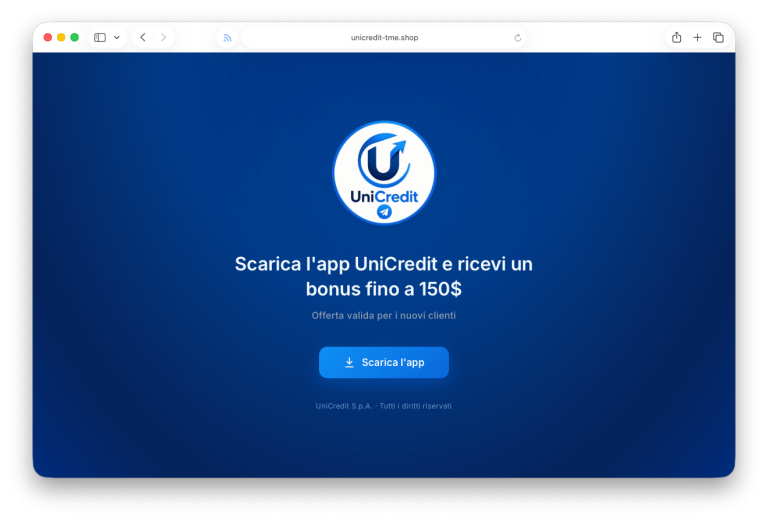
Albiriox malware spreads via a fake UniCredit reward and a Telegram bot. The Android banking trojan abuses Accessibility to steal OTPs and hijack devices.
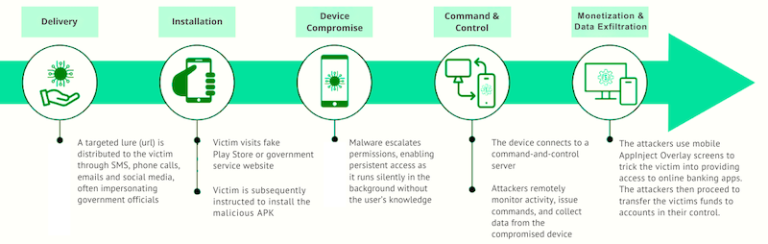
Infoblox uncovers the K99 compound: a brutal MaaS operation using human trafficking to power biometric hijacking and global Android banking fraud.

Cyfirma exposed Android/BankBot-YNRK, a Trojan cloning Indonesia’s Digital ID app to steal credentials and crypto assets. It uses anti-emulation checks and JobScheduler for persistent device takeover.

A new BankBot campaign targets Android users in Indonesia and Vietnam. The malware uses spoofed app stores and a WebSocket-based download for stealth.

Uncover the threat of OctoV2, an Android banking Trojan that deceives users through fake AI chatbot applications.

Uncover the dangers of the Mamont Android banking Trojan. Protect yourself from malicious parcel tracking apps and photo identification scams.

Beware of the new Android banking trojan targeting Indian users. Learn how this sophisticated malware steals financial information through phishing campaigns.

Beware of the BlankBot Android banking trojan! Discover how this sophisticated malware targets mobile users and gains complete control of infected devices.

Cybersecurity researchers at Zscaler ThreatLabz have uncovered a sophisticated Android banking trojan called Anatsa (also known as TeaBot)