 Do Son
A new SectopRAT malware variant hides inside legitimate audio software. Learn how SectopRAT malware extracts data and controls devices.
Arechclient2

Elastic Security Labs reveals SHELLTER Elite v11.0 is being abused to deploy LUMMA, RHADAMANTHYS, and ARECHCLIENT2 infostealers, leveraging advanced evasion techniques to bypass AV/EDR
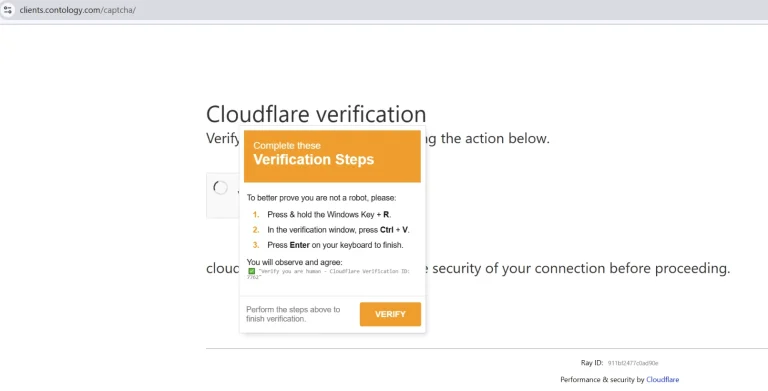
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

Learn about Emmenhtal, a stealthy malware loader that employs LOLBAS tactics to deliver undetected malware strains like Lumma and Amadey.
Transport and logistics companies in North America targeted in a sophisticated cyberattack. Learn about the tactics used and how to protect your business.