
 Do Son
RTO Challan malware hijacks Android devices in India using a fake traffic ticket lure, a malicious VPN, and SMS interception to steal UPI PINs and Aadhaar data.
Banking Trojan
Water Saci Campaign Uses LLMs to Convert Malware to Python, Spreads Banking Trojan Via WhatsApp Worm

Water Saci Campaign Uses LLMs to Convert Malware to Python, Spreads Banking Trojan Via WhatsApp Worm
Trend Micro exposed Water Saci, a campaign using LLMs to convert malware from PowerShell to Python, accelerating its spread via a WhatsApp worm. The multi-stage attack deploys a trojan capable of VNC mirroring and overlay attacks.

Meet Albiriox, a new Russian Android banking Trojan sold as a service. Learn how its "AcVNC" tech enables on-device fraud against 400+ global apps.
Sophos exposed STAC3150, a campaign using fake "View Once" messages to deploy Astaroth banking trojan. The malware hijacks WhatsApp Web sessions via WPPConnect/Selenium for self-propagation.

Trustwave exposed Eternidade Stealer, a sophisticated Brazilian Trojan. The Python WhatsApp worm steals contact lists and uses IMAP email for covert C2 retrieval to launch banking overlays.

Zimperium exposed Fantasy Hub, a Russian MaaS Android RAT. It uses a Telegram bot for subscriptions and WebRTC to covertly stream live video and audio, targeting Russian banks with dynamic overlays.

CERT Polska exposed NGate, an Android malware that tricks users into tapping their card against their phone to steal NFC EMV data and PINs. The data is then relayed to an ATM for cash withdrawal.

BitSight uncovered a Lampion banking Trojan campaign using ClickFix lures and a 700MB bloatware DLL to evade AV. The VBScript loader establishes persistence via the Windows Startup folder.

GhostGrab is a hybrid Android malware that steals banking credentials and OTPs via phishing WebView overlays while secretly running a Monero miner in the background to monetize the victim's device.

SEQRITE exposed CAPI, a .NET trojan targeting Russian FinTech with malicious LNK resumes. It uses rundll32 for execution and a hidden "Security" scheduled task for persistence.

Kaspersky exposed Maverick, a sophisticated fileless banking Trojan targeting Brazil. It hijacks WhatsApp Web using WPPConnect for self-propagation and installs phishing overlays to steal UPI/banking data.
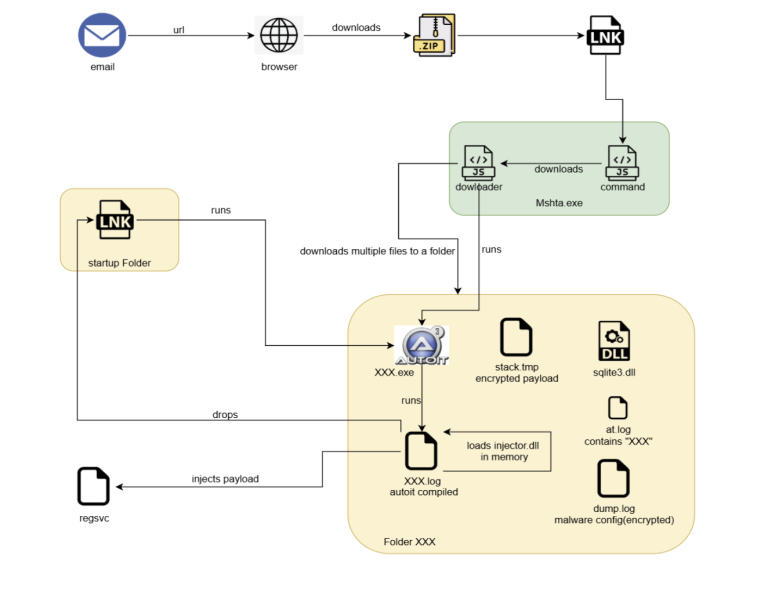
McAfee uncovered the Astaroth banking Trojan using GitHub for C2 backup, hiding encrypted configuration data via steganography in images to target Brazilian financial and crypto users.

Cleafy uncovers Klopatra, a new Android RAT using commercial Virbox obfuscation and native code to target banks in Spain/Italy, allowing invisible remote device control.Export to Sheets

After nearly two years of silence, Zloader (a.k.a. Terdot, DELoader, or Silent Night) has returned with new...

A new Android banking trojan, RatOn, merges overlay fraud with NFC relay attacks, automated money transfers, and crypto wallet theft, posing a new threat to users.

A new report reveals a mobile malware campaign in Indonesia impersonating the state pension fund TASPEN to steal financial and personal data from civil servants.

A new report reveals the Hook Android trojan has evolved into a hybrid threat with ransomware-style overlays, lockscreen bypasses, and stealthy screen-streaming.

A new report reveals the Anatsa banking trojan is now targeting over 831 financial institutions worldwide. The malware is distributed via fake apps on Google Play.

A new Android banking trojan, dubbed "Lazarus Stealer," is using sophisticated overlay attacks to steal financial credentials from users of Russian banks.

McAfee uncovers a new Android malware campaign targeting Indian users. The malware impersonates major banks to steal financial data and silently mines Monero in the background.

Cyble uncovers RedHook, a new Android banking trojan targeting Vietnamese users with sophisticated phishing, remote access, screen capture, and keylogging for full device takeover.

Akamai confirms Coyote, a Latin America-focused banking trojan, is the first malware to exploit Microsoft's UI Automation (UIA) framework in the wild for credential theft.