 Do Son
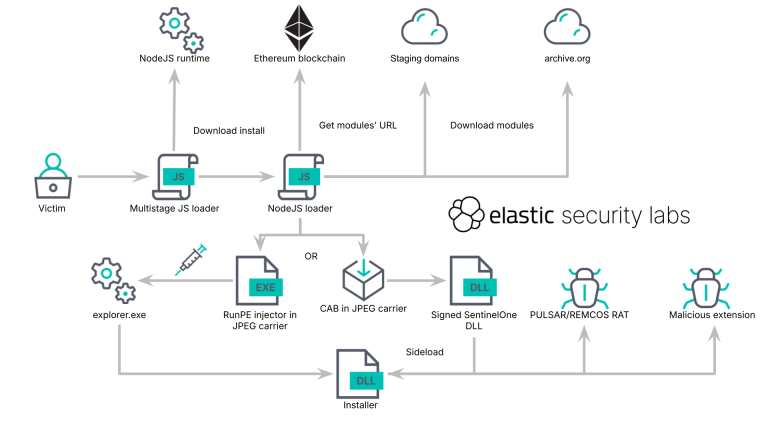
Learn how Brazilian KREMLIN banking malware steals credentials using fake browser extensions. Elastic Security Labs details the KREMLIN banking malware.
Banking Trojan
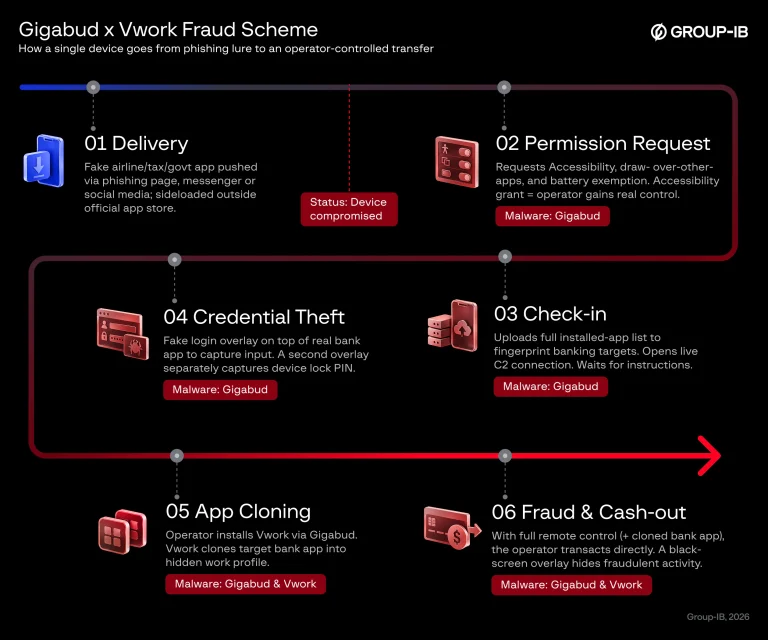
Group-IB uncovered how the Gigabud Vwork Android malware chain clones apps. Discover how Vwork Android malware evades bank detection.
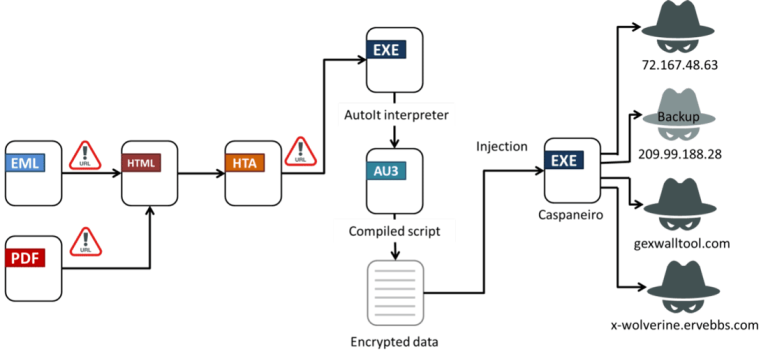
A new Casbaneiro banking trojan campaign hits Latin America. Learn how the Casbaneiro banking trojan evades detection and targets bank logins.
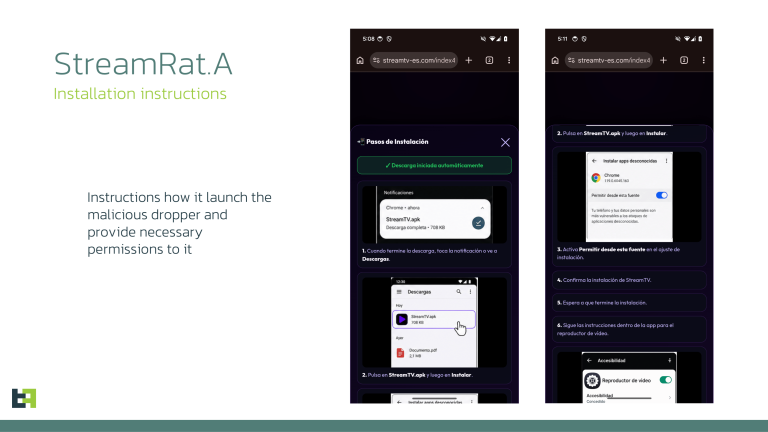
A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.
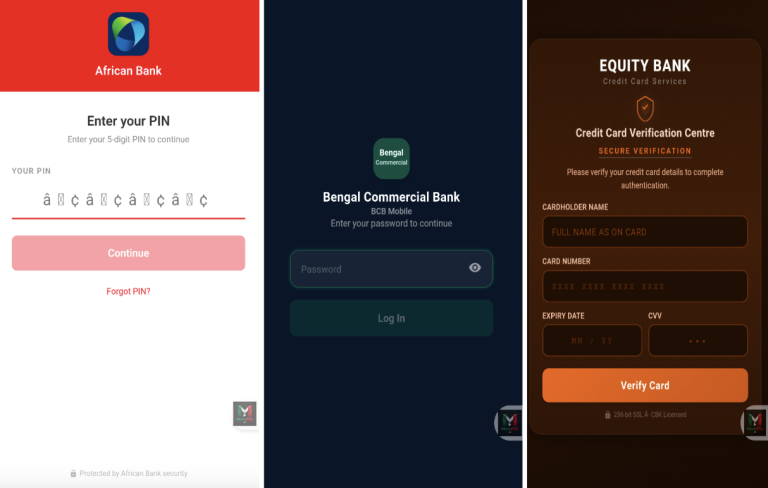
The new ToxicPanda 2.0 banking Trojan attacks target hundreds of financial apps globally. Learn how this ToxicPanda 2.0 banking Trojan steals credentials.

Grandoreiro banking trojan resurfaces in a DLL sideloading campaign that abuses Duplicate Files Finder to hit Mexico and Latin America.
A Lampion malware campaign is hitting Portugal. The Portugal phishing campaign uses fake SAPO transfer pages to drop a multistage VBS infection chain.
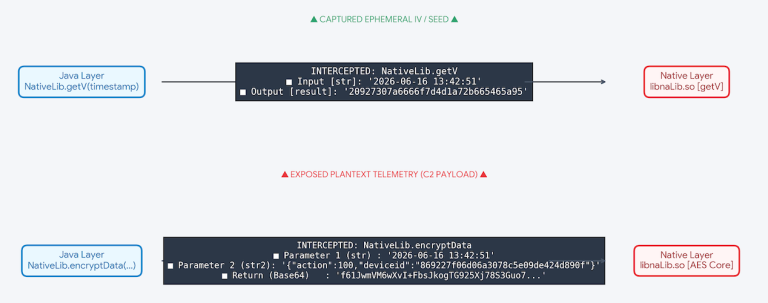
The GoldPickaxe banking Trojan returns, stealing biometric data, SMS, and lock screens from Android users across Asia, Zimperium warns.
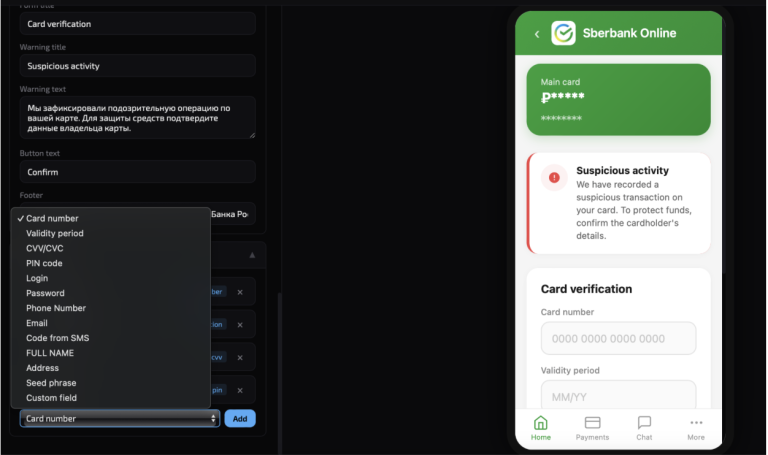
RedWing Android malware is a rental spyware sold as malware-as-a-service on Telegram. It steals banking logins, intercepts 2FA, and hijacks phones.
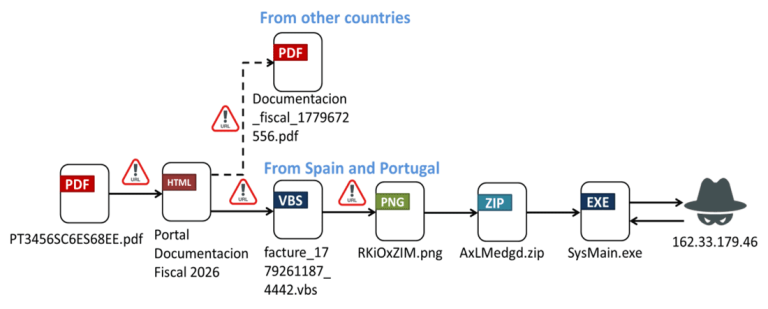
FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.
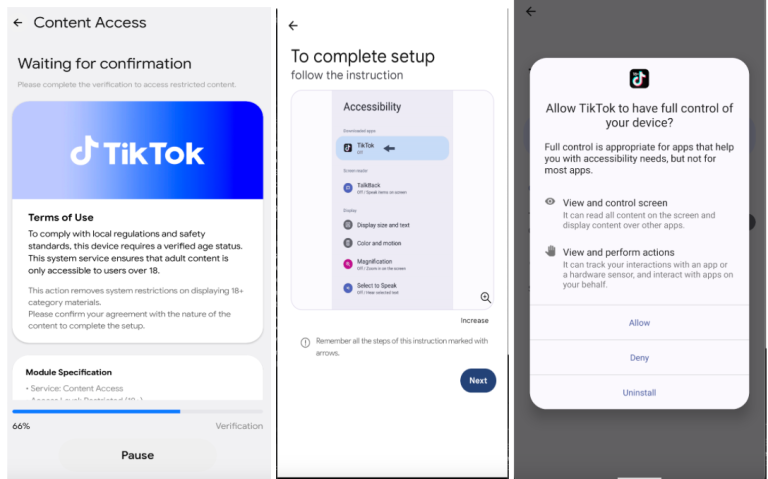
The Rokarolla Android banking trojan executes a complete device takeover. It targets 217 apps and steals credentials through fake overlays and keyloggers.
The dangerous Grandoreiro banking trojan returns. Discover how it utilizes an advanced DLL side loading technique to bypass corporate defenses.

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.
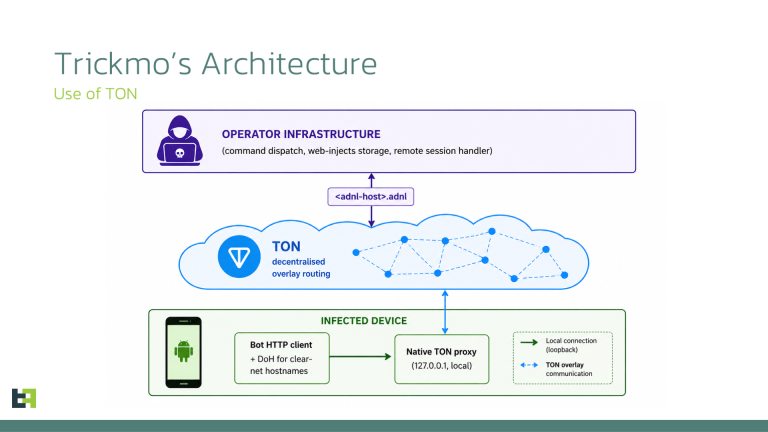
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
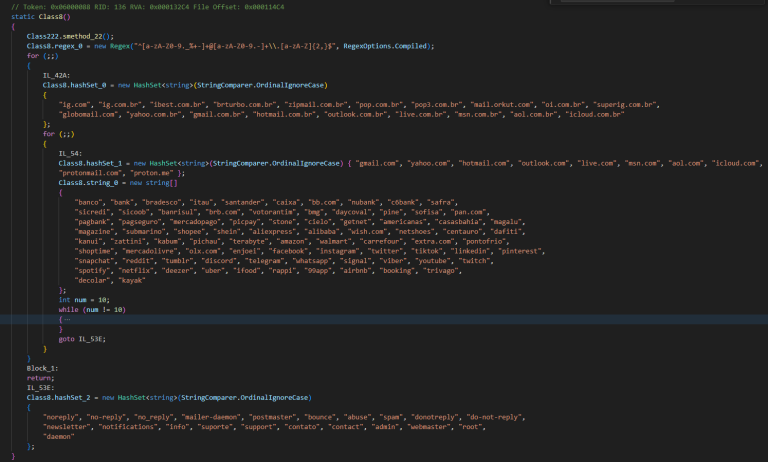
Elastic Security Labs exposes TCLBANKER, an advanced banking trojan that hijacks WhatsApp to spread while blinding defenders with invisible WPF overlays.
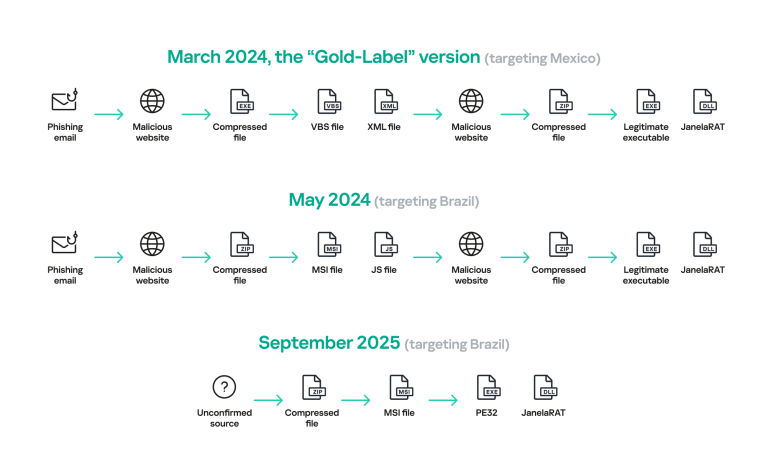
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.
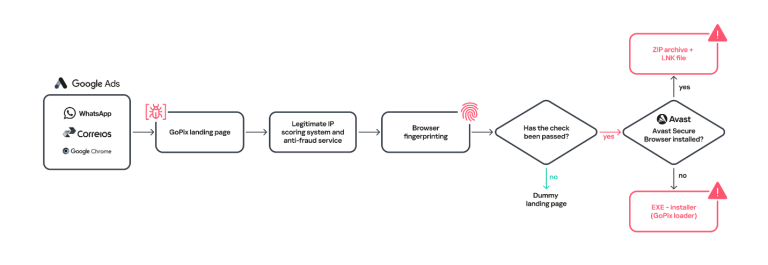
Kaspersky Labs details GoPix, a highly advanced Brazilian banking Trojan using memory-only implants and MitM attacks to target Pix and crypto.
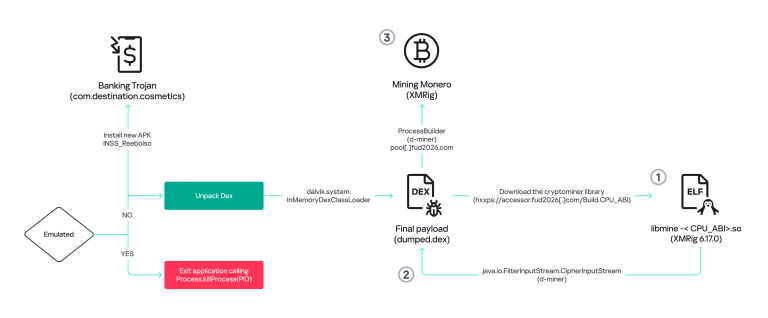
Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.

In a troubling convergence of trusted developer infrastructure and cybercrime, Bitdefender researchers have uncovered a sophisticated Android...

New deVixor Android malware combines banking fraud with ransomware. Targeting Iranian users, it steals credentials and locks devices. Avoid APKs.

New Astaroth campaign "Boto Cor-de-Rosa" uses a Python worm to hijack WhatsApp Web. It auto-messages your contacts to spread banking malware globally.

Group-IB uncovers "Wonderland," a bidirectional Android SMS stealer in Uzbekistan that uses Telegram droppers to drain bank accounts and hijack sessions.