 Do Son
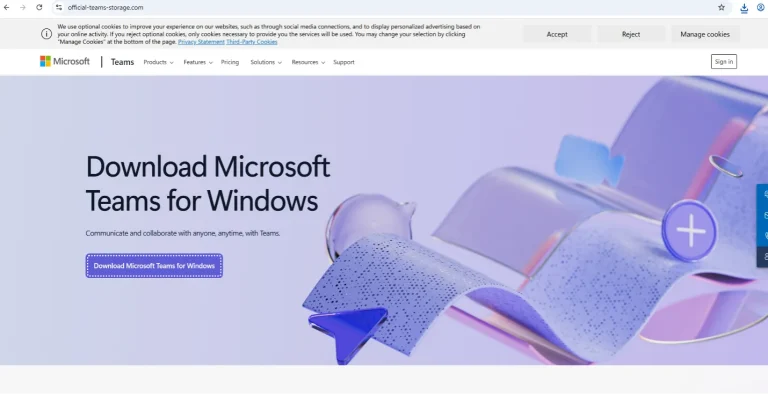
BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.
BlueVoyant

BlueVoyant exposes Blitz Brigantine's new tactics: using email bombing, Microsoft Teams lures, and covert DNS MX tunneling to deploy AOBackdoor.

BlueVoyant uncovers a shift in Mercenary Akula (UAC-0050) tactics, targeting European financial institutions via spoofed judicial lures and RMS malware.