Skip to content
October 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • CASTLESTEALER

CASTLESTEALER

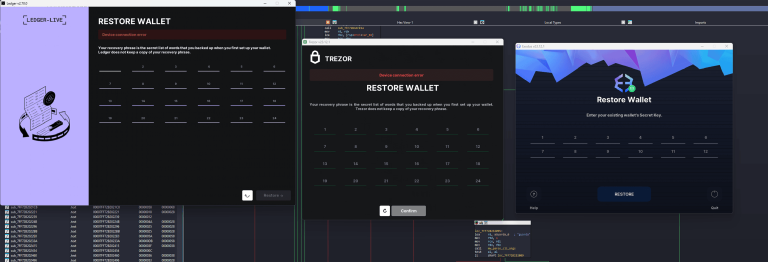
CastleLoader Malware Now Delivers NeedleStealer Wallet and Browser Spoofers CastleLoader malware infection chain delivering NeedleStealer crypto wallet spoofer and NetSupport RAT
  • Malware

CastleLoader Malware Now Delivers NeedleStealer Wallet and Browser Spoofers

Do Son August 3, 2026 0
At a glance Malware family CastleLoader (loader); payloads include CastleStealer, NetSupport RAT, Lobshot, and NeedleStealer Threat actor...
Read More Read more about CastleLoader Malware Now Delivers NeedleStealer Wallet and Browser Spoofers
Starland RAT Campaign by Russian-Speaking Actor UAT-11795 Targets Crypto Users in the US and Europe Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

Starland RAT Campaign by Russian-Speaking Actor UAT-11795 Targets Crypto Users in the US and Europe

Do Son July 22, 2026 0
At a glance Actor / group UAT-11795 (suspected Russian-speaking, financially motivated) Activity type Credential and cryptocurrency theft...
Read More Read more about Starland RAT Campaign by Russian-Speaking Actor UAT-11795 Targets Crypto Users in the US and Europe
OXLOADER Malware Loader Spreads CASTLESTEALER via Fake Node.js Ads TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

OXLOADER Malware Loader Spreads CASTLESTEALER via Fake Node.js Ads

Do Son June 26, 2026 0
At a Glance Malware family OXLOADER (loader) delivering CASTLESTEALER (.NET infostealer) Threat actor Unnamed; suspected Russian-speaking and...
Read More Read more about OXLOADER Malware Loader Spreads CASTLESTEALER via Fake Node.js Ads

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    CISA KEV📅 Added to KEV: Oct 26, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    CISA KEV📅 Added to KEV: Oct 26, 2026
  • CVE-2026-106173CVSS 9.8
    A improper limitation of a pathname to a restricted directory (\'path traversal\') vulnerability in Fortinet FortiSIEM 7.5.0 may...
    Admin intel📅 Updated: Oct 25, 2026
  • CVE-2014-125133CVSS 8.7
    NativeChurch theme for WordPress before 1.6.2 contains a path traversal vulnerability that allows unauthenticated attackers to download arbitrary...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2015-20128CVSS 8.8
    FooSun DotNetCMS 1.0 and 2.0 contains an SQL injection vulnerability that allows unauthenticated attackers to manipulate MSSQL queries...
    Watchtower Verified📅 Updated: Oct 24, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-91323CVSS 9.8
    Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected...
    📅 Updated: Oct 27, 2026
  • CVE-2026-87302CVSS 9.1
    Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected...
    📅 Updated: Oct 27, 2026
  • CVE-2026-110063CVSS 10.0
    Improper link resolution before file access ('link following') in VM Inspector for Azure Virtual Machines allows an unauthorized...
    📅 Updated: Oct 27, 2026
  • CVE-2026-10757CVSS 9.8
    There is a SQL injection vulnerability in Esri ArcGIS Server versions 12.1 and earlier on Windows and Linux...
    📅 Updated: Oct 27, 2026
  • CVE-2026-107656CVSS 9.8
    An authentication bypass using an alternate path or channel vulnerability in Fortinet FortiSandbox 5.0.0 through 5.0.6, FortiSandbox 4.4.0...
    📅 Updated: Oct 27, 2026
  • CVE-2026-109391CVSS 9.2
    Square Squash through commit e73f280 contains an insecure deserialization vulnerability that allows unauthenticated attackers to store crafted YAML...
    📅 Updated: Oct 27, 2026
  • CVE-2026-105223CVSS 9.1
    maclof kubernetes-client 0.17.0 before 0.32.0 disables TLS certificate verification in parseKubeconfig() and parseKubeconfigFile() when a kubeconfig lacks certificate-authority-data,...
    📅 Updated: Oct 27, 2026
  • CVE-2026-105216CVSS 9.1
    go-micro before 6.0.0 contains an improper certificate validation vulnerability that allows network attackers to impersonate services because the...
    📅 Updated: Oct 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.