 Do Son
CVE-2026-1207 is a Django SQL injection flaw (CVSS 8.3) in PostGIS raster lookups. Canada's CCCS says it is exploited in the wild. Patch now.
Crowdsec
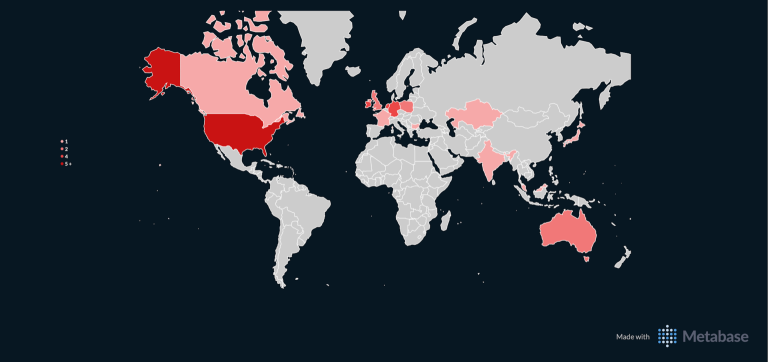
Urgent: CrowdSec warns CVE-2024-9643 in Four-Faith routers has hit mass exploitation phase. Attackers abuse hardcoded logins to build botnets. Patch now!

Discover how CrowdSec is revolutionizing the security of network infrastructures. Learn about its cutting-edge behavior detection engine and its community-powered protection.