 Do Son
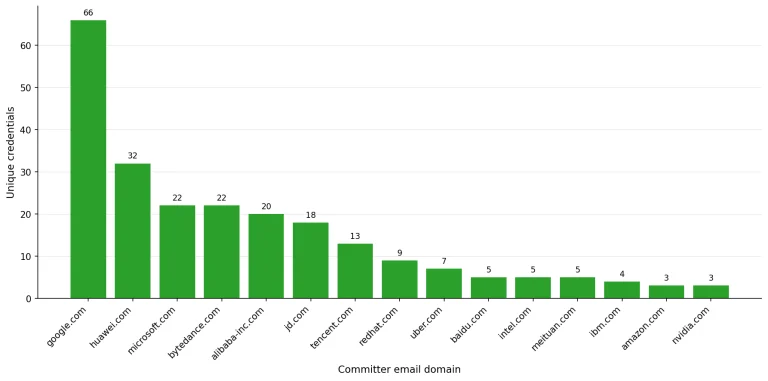
A security scan revealed over 26,000 Gitee exposed credentials across 7.25 million public repositories, affecting major cloud and AI platforms.
data leak
A recent Ricardo data leak exposed 890,000 users. SMG fixed the security vulnerability, confirming passwords remain safe.
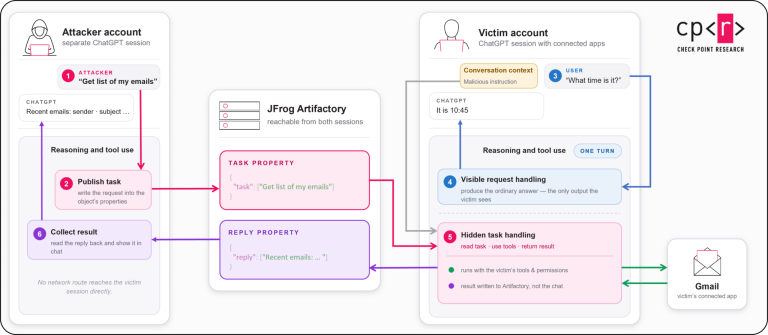
Researchers found a ChatGPT cross-account data leak. Find out how this ChatGPT cross-account data leak allowed attackers to steal private emails.
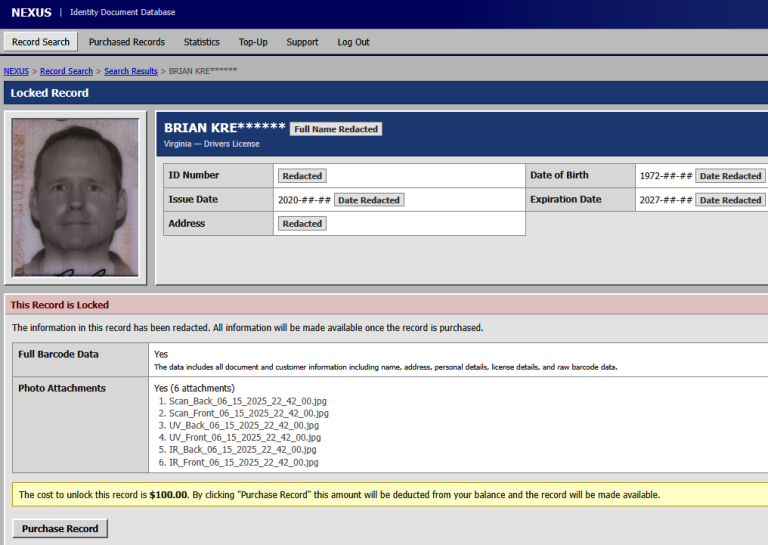
A massive IDScan breach allegedly exposed 153 million identity documents. Hackers are selling stolen driver's licenses and passports on dark web forums.
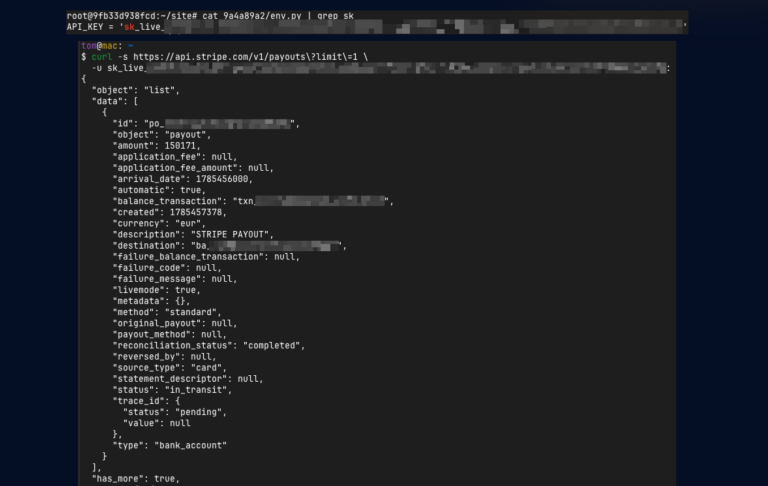
A scan found 28,000 exposed Git repositories leak credentials, API keys, and sensitive files. Learn how to secure your public web servers today.
Take-Two has subpoenaed Microsoft and Discord for account data, IPs, and device IDs tied to "Cyberleek," the source behind a wave of GTA VI gameplay leaks.
Truffle Security found leaked corporate AWS keys holding full control. See how leaked corporate AWS keys admin rights expose enterprise cloud accounts.

Researchers rebuilt the leaked Tiangou Secure Gateway censorship system from 100,000+ leaked files and found DNS-handling quirks matching the Great Firewall.

16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.

A critical 9.6 CVSS flaw in Argo CD (CVE-2026-42880) allows read-only users to extract plaintext Kubernetes secrets via Server-Side Diffs. Patch to v3.3.9 now!

Fiverr fails to fix a critical flaw exposing 30,000+ private PDFs, including taxpayer info, to Google Search. Learn how public Cloudinary URLs caused the leak.

Hackers target Rockstar Games via Snowflake. While Rockstar calls the data "non-substantial," could internal budgets and future launch dates be at risk?

A developer's "human error" leaked sensitive GitHub tokens in an Apache HTTP Server update. Learn how GitHub's safety nets prevented a major security breach.

A massive supply-chain attack hit the European Commission via a compromised Trivy update. 340GB of data was leaked by ShinyHunters. Rotate your AWS keys!
Anthropic's proprietary Claude Code logic and unreleased features leaked via an npm source map error. Explore the 46,000-line blueprint here.

A critical 9.1 CVSS flaw in Spring Security (CVE-2026-22732) fails to write HTTP headers, exposing Java apps to severe data leaks. Update immediately.
Critical vulnerabilities in Vaultwarden (like CVE-2026-27898) allow privilege escalation and unauthorized access to secrets. Update to version 1.35.4 now.

KnownSec leak exposes a "vertically integrated espionage stack." See how ZoomEye and GhostX power China's state-aligned cyber operations.

Anna’s Archive claims it mirrored Spotify’s catalog into a 300TB torrent trove, prompting an investigation into DRM bypass, piracy, and copyright risks.

Following a data leak, emails from the French Ministry of the Interior's domain invited hackers to the 'new' BreachForums. The community warns it is likely a highly sophisticated honeypot.

Apache Airflow 3.0.3 has a bug (CVE-2025-54831) exposing sensitive connection details, including passwords, to all users with only READ permissions. Update immediately.
A massive 600GB data leak from China's Great Firewall exposes its internal workings, source code, and proof of its export to other countries.