 Do Son
Discord announced that Discord public messages from discoverable servers will soon be indexed by search engines and published on the open web.
Discord
Take-Two has subpoenaed Microsoft and Discord for account data, IPs, and device IDs tied to "Cyberleek," the source behind a wave of GTA VI gameplay leaks.

A fake Xeno cheat spreads Xeno Roblox malware, a Java stealer that grabs accounts and crypto wallets and spies via webcam. Learn how to stay safe.
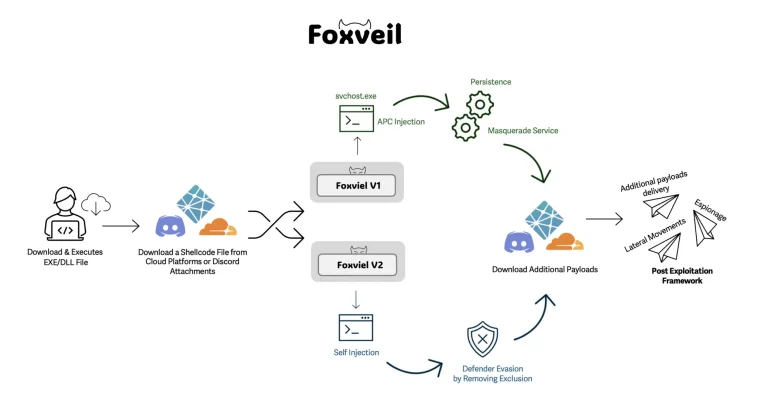
Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

Kaspersky exposed Tomiris APT using a "polyglot" strategy (Go/Rust/Python) and Telegram/Discord for covert C2. The group targets foreign ministries with implants that steal file paths and reconnaissance data.

Malicious packages across npm, PyPI, and RubyGems are exploiting Discord webhooks as stealthy, resilient C2 endpoints to exfiltrate developer config files and sensitive host data.

eSentire discovered ChaosBot, a Rust-based malware deployed via DLL sideloading that uses Discord channels as a covert C2 platform to perform reconnaissance and command execution.

A new campaign uses a malicious LNK shortcut sent via Discord to deploy a multi-functional RAT that hijacks legitimate Windows binaries to evade detection.

A new report reveals Inf0s3c Stealer, a stealthy Python malware that abuses Discord to exfiltrate passwords, crypto wallets, and other sensitive data from victims.

Elastic Security Labs exposes NOVABLIGHT, a NodeJS-based infostealer-botnet MaaS disguised as an "educational tool," actively distributed via Telegram and targeting victims with fake game installers.

AhnLab uncovers SVF Bot, a Python-based DDoS botnet abusing Discord as its C&C channel to target misconfigured Linux servers and launch HTTP/UDP floods.
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

Katz Stealer, a new MaaS infostealer, targets browsers, crypto wallets, and Discord using advanced evasion and UAC bypass techniques.

New lightweight PupkinStealer malware silently steals browser data, messaging sessions, and desktop files, sending it all via Telegram.

Inferno Drainer returns stronger than ever, using Discord phishing and blockchain obfuscation to steal millions in crypto.

Cyfirma uncovers a Python-based RAT using Discord for command and control. It can lock screens, simulate BSOD, move the mouse, and steal data.

Explore the dangers of RAT, a Python-based Discord Trojan exploited by cybercriminals on popular gaming platforms.

Learn how a massive malvertising campaign exploited illegal streaming websites to deliver information-stealing malware.

Learn about ROOST, the non-profit organization formed by Roblox, Discord, OpenAI, and Google to develop advanced open-source security tools for a safer online environment, particularly for children.

Discover the latest deanonymization attack exposed by security researcher Daniel. Learn how this 0-click attack leverages Cloudflare’s caching mechanisms to pinpoint user locations.

Beware of the malicious PyPI package targeting Discord developers. Learn how typosquatting can lead to token theft and backdoor installation.