 Do Son
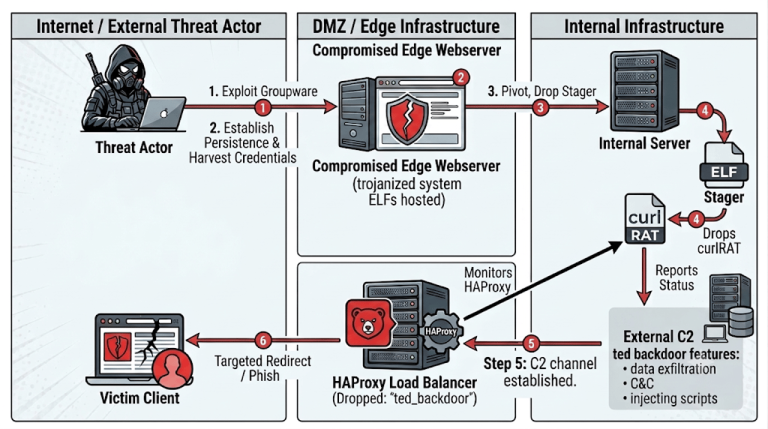
The ted backdoor is DPRK Linux malware hidden inside HAProxy. It pairs with curlRAT to spy on South Korean media and automotive firms, Rapid7 reports.
DPRK APT

ENKI exposed a Kimsuky APT campaign using a dual PE/PowerShell payload that switches based on Windows Defender status to deploy KimJongRAT. The malware steals Chrome AppBound keys via GitHub Releases C2.

Orange Cyberdefense’s CyberSOC and CSIRT teams have uncovered a new wave of Operation DreamJob attacks, revealing updated...