 Do Son
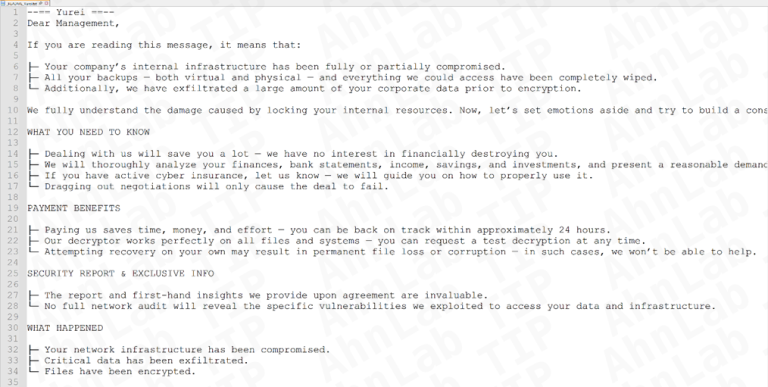
ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.
ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.