 Do Son
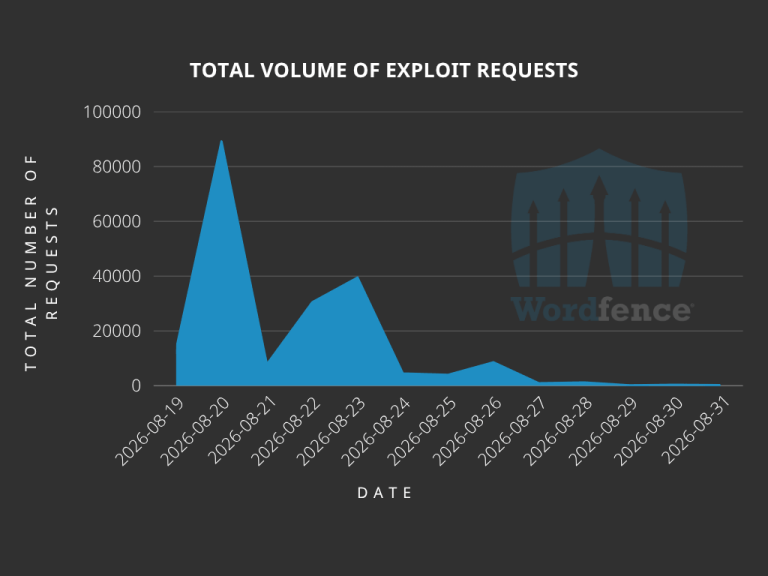
Attackers exploit a critical Elementor Pro vulnerability (CVE-2026-32475) in the wild. Patch this Elementor Pro vulnerability to prevent site takeover.
Elementor Pro
CVE-2026-32475 (CVSS 9.8) is an Elementor Pro arbitrary file upload flaw risking complete site compromise across 6 million WordPress sites. Update to 4.2.2.