
 Do Son
New "Exfil Out&Look" attack uses OWA add-ins to steal emails without leaving logs. Microsoft has no immediate fix for this blind spot.
Email Security
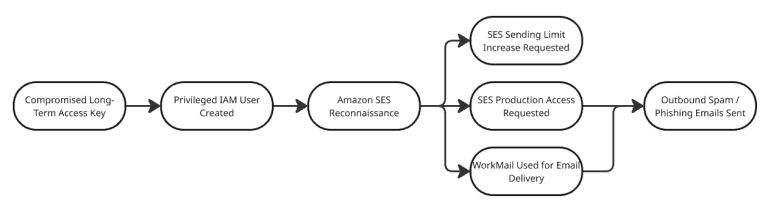
Attackers are bypassing AWS SES sandbox limits by pivoting to WorkMail. Rapid7 reveals how this abuse creates a blind spot for defenders.

Google officially ended POP3 fetching and Gmailify in Jan 2026. External emails will no longer reach your web inbox unless you set up auto-forwarding.

Attackers exploit complex mail routing to spoof "internal" emails using Tycoon2FA. Learn how to fix misconfigured DMARC policies and stop the breach.

SmarterMail hits a 10/10 CVSS severity! CVE-2025-52691 allows unauthenticated RCE via arbitrary file uploads. Update to Build 9413 immediately!

Zimbra patches a high-severity LFI (CVE-2025-68645) allowing unauthenticated file access and a Flickr Zimlet credential leak. Upgrade to v10.1.13!

Fortra unmasks Scripted Sparrow, a global BEC collective sending 3M+ targeted emails monthly via spoofed executive chains to steal millions.

Roundcube patches two High-severity flaws: an SVG-based XSS and a CSS sanitizer bypass. Protect your inbox—update to v1.6.12 or v1.5.12 now.

SonicWall patched a critical flaw (CVE-2025-40604) in its Email Security appliances. The bug allows persistent RCE by exploiting a lack of integrity checks when loading the root filesystem image from the VM datastore.

Libraesva has issued an urgent advisory for a command injection flaw in its ESG. The bug, which has been exploited, allows remote command execution via a malicious email.

Cloudflare exposes a phishing campaign that abuses link wrapping services like Proofpoint and Intermedia, making malicious URLs appear legitimate to bypass security and trick users.

Varonis uncovers a widespread phishing campaign abusing Microsoft 365's Direct Send, spoofing internal users to bypass email security and harvest credentials.

Clicking unsubscribe links can be risky, confirming your email is active or leading to phishing. Use email client features or block senders to stay safe.

Cofense Intelligence reports a new phishing tactic using blob URIs to bypass Secure Email Gateways. Attackers use these local URIs to hide phishing pages.

The CoGUI phishing kit uses advanced evasion to target Japan with high-volume campaigns impersonating Amazon, PayPay, and more.

Proofpoint uncovers TA2900, a French-speaking BEC actor exploiting rental payments via fake IBANs and compromised education accounts to steal funds.

A sophisticated DKIM Replay Attack spoofed Google, bypassing email security. Learn how this attack worked and how to protect yourself from email spoofing.

Phishing attacks are evolving! Cybercriminals now embed HTML in SVG files to bypass detection. Learn how SVG phishing works and how to stay safe.

Phishing attacks using SVG files surged 1800%, exploiting JavaScript and PhaaS kits to bypass MFA and steal credentials, Trustwave warns.

Learn about Precision-Validated Phishing, a sophisticated technique where attackers use real-time email validation to target specific users, making credential theft more effective and harder to detect.

A new "Pick Your Poison" phishing campaign tricks users into choosing between having their credentials stolen or infecting their systems with malware. Cofense analysis reveals how this double-edged attack uses files.fm to deliver malicious payloads.

Enhance email security with Inbound SMTP DANE and DNSSEC. Learn how Microsoft's Exchange Online protects against sophisticated cyberattacks.