 Do Son
CISA adds PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 to the CISA KEV catalog after confirmed RCE and suspected DPRK-linked scanning.
Lazarus Group
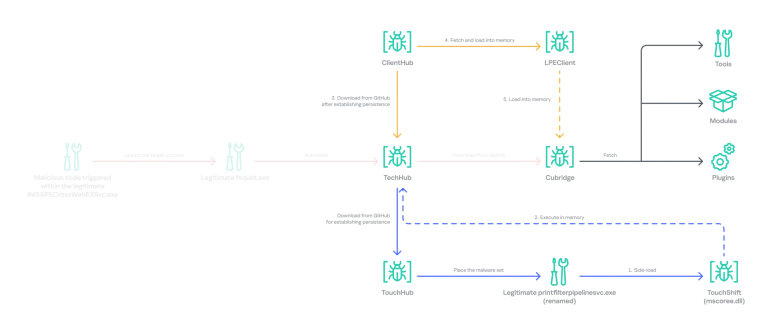
In Operation FlashHole, the Lazarus Group used AI-made lure sites, CrossWeb EX, and GitHub C2 to spy on South Korean firms. Here is how.

Microsoft August 2026 Patch Tuesday fixes 421 flaws, including CVE-2026-68820, a WinSock zero-day exploited in the wild by Lazarus Group.
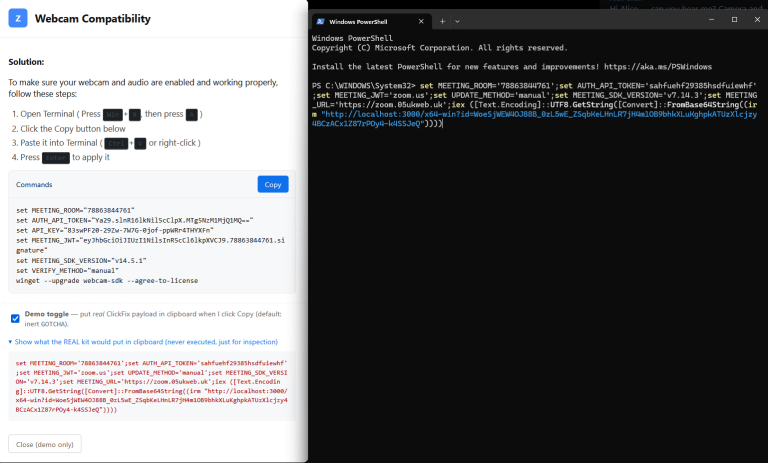
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.

An in-depth PHANTOMPULSE malware analysis reveals a sneaky blockchain C2 channel and AI-assisted coding techniques used by advanced threats.

Fox-IT uncovers a sophisticated Lazarus memory-only toolset used to compromise financial firms via an evasive three-stage malware pipeline.

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.
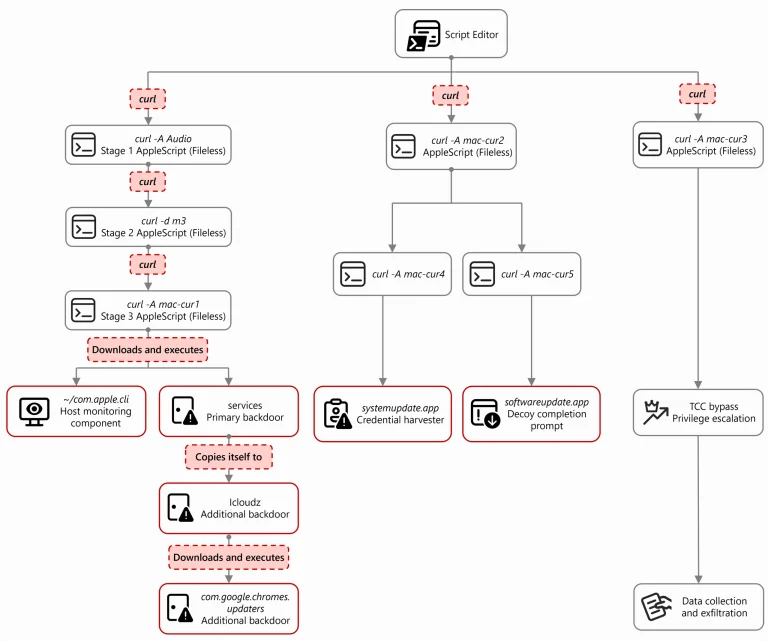
Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!
PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.

DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.
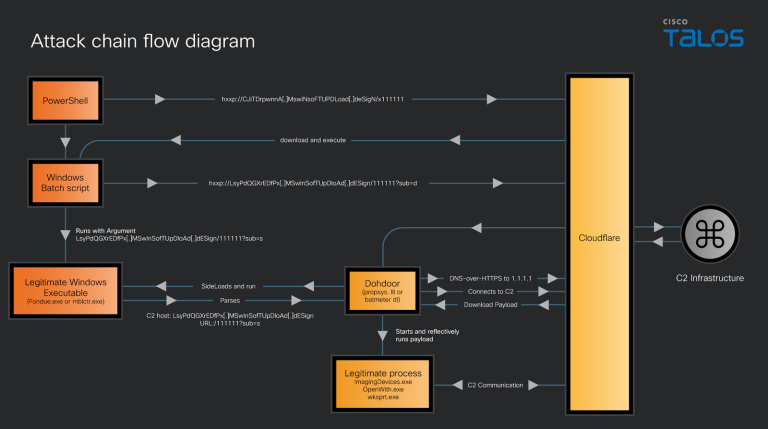
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.

Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.

BlueNoroff hackers use fake "audio issues" on Teams calls to trick macOS users. The "fix" runs terminal commands that steal Keychains. Watch out.

A joint Hunt.io and Acronis report exposes the shared infrastructure behind Lazarus and Kimsuky, revealing the unified web of North Korean hacking.

Amazon foils 1,800+ North Korean hacks, using a 110ms keystroke lag to expose a fake sysadmin operating from an Arizona "laptop farm."

A deep-dive on Lazarus’s ScoringMathTea RAT reveals a full reflective DLL injection system, TEA/XTEA C2 encryption, and a polyalphabetic cipher for API hashing—a highly evasive tool for espionage.

The DOJ announced five guilty pleas and $15M in crypto forfeiture seized from APT38. Facilitators helped North Korean IT workers fraudulently earn $2.2M from 136 US companies to fund the DPRK regime.
Australia imposed sanctions and travel bans on four entities and one individual for engaging in cybercrime to fund North Korea's WMD and missile programs. The regime stole $1.9B in crypto in 2024.

ENKI exposed a Lazarus Group espionage campaign targeting aerospace/defense firms. The new Comebacker variant uses malicious Word macros and ChaCha20/AES to deliver a memory-resident backdoor.