 Do Son
Apple updated macOS 27.3 permissions in Beta 2, letting users restrict Full Disk Access to specific folders and limit automation tools per app.
macOS
Apple announced the permanent Apple Support Community shutdown on November 20, 2026, placing the 28-year-old troubleshooting forum into read-only mode.
Apple tightens macOS Full Disk Access in macOS 27.3, requiring manual app authorization to prevent AI agents from accessing sensitive personal user files.
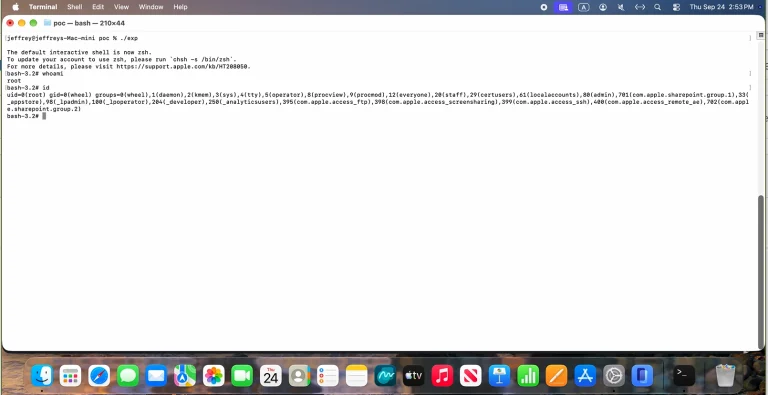
Details and a macOS privilege escalation PoC exploit are public for CVE-2026-112445. Patch macOS now to stop local users from gaining root privileges.
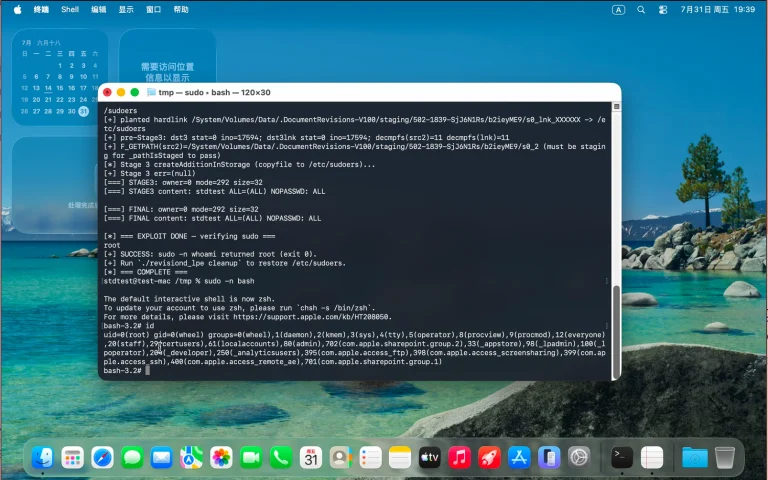
Technical details and a macOS revisiond vulnerability PoC exploit for CVE-2026-112487 are public, allowing root elevation. Update macOS immediately.
PoC and details are public for CVE-2026-84568, a macOS autofs vulnerability enabling root code execution, and a Gatekeeper bypass. Update macOS now.
Apple blocks eMudhra certificates across macOS and iOS after weak intermediate keys compromised trust, with CLI tool bundles slated for future updates.
The Arc browser shutdown arrives December 22, 2026. Export your data now and move to Dia before accounts are deleted.
Explore the new ChatGPT Meetings plugin for macOS. It offers native OS-level audio capture and seamless integration with the ChatGPT Space workspace.
PoC and details released for macOS HFS+ vulnerability CVE-2026-43682, a CVSS 9.8 kernel heap overflow. Update to macOS Tahoe 26.6 now.
Details and a PoC are public for CVE-2026-84543, a macOS SMB kernel vulnerability that lets a malicious SMB server crash Macs. Update macOS now.
Apple patched an exploited Apple zero-day vulnerability. Learn how this Apple zero-day vulnerability impacts devices and install emergency updates now.
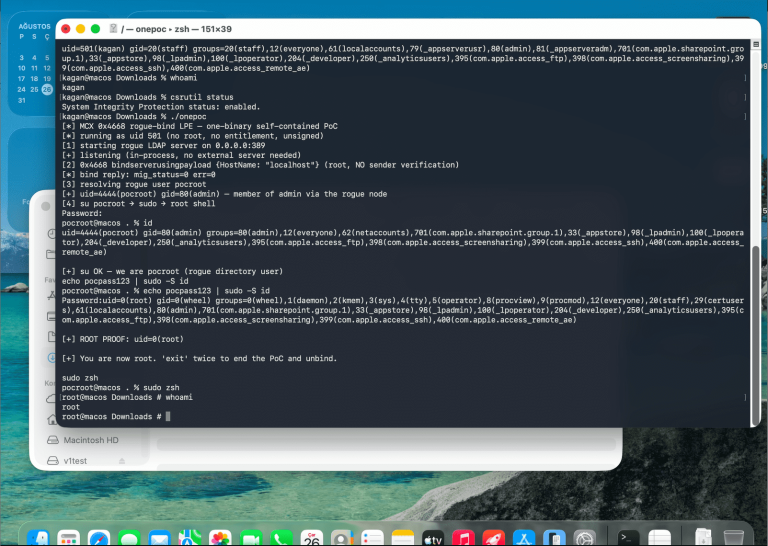
A critical macOS CoreServices vulnerability (CVE-2026-43786) is patched. Apple privilege escalation PoC details are now public.
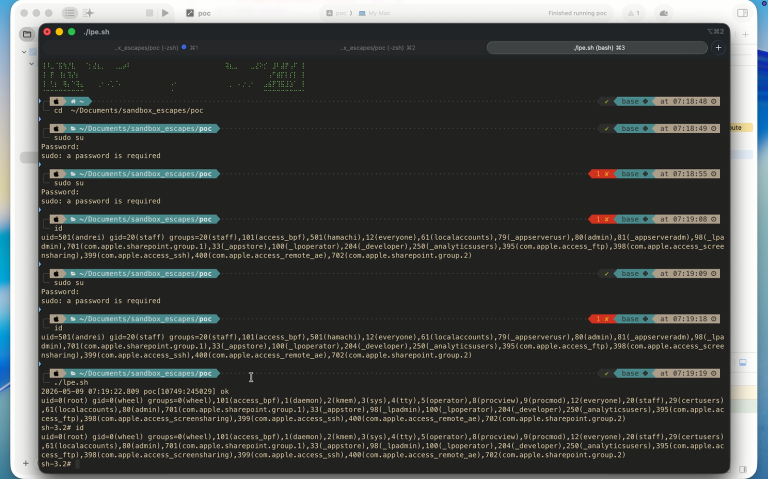
Details and PoC for the critical macOS DesktopServicesHelper vulnerability are public. Learn how CVE-2026-43783 enables root access.
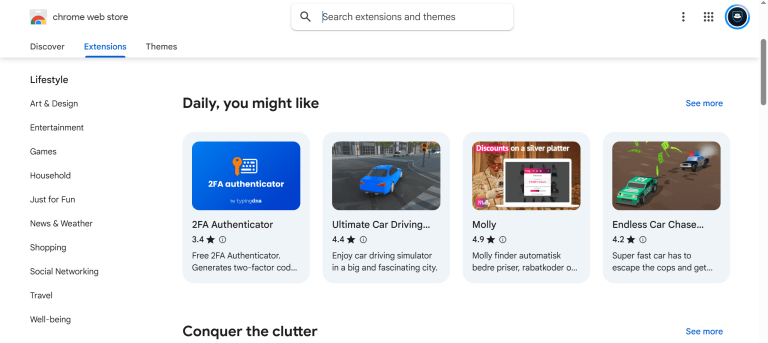
A Chrome extension popup freeze bug on macOS delays 1Password and other extensions by minutes. Google has flagged it high priority but has no fix yet.
Security teams uncovered trojanized fake macOS installers tied to North Korean campaigns that deploy OtterCookie malware on Apple devices.
CVE-2026-43748 (CVSS 9.8) is an Apple ANE kernel out-of-bounds write reachable from a sandbox. Details and macOS/iOS PoC code are public. Update now.

PoC exploit code is public for CVE-2026-43723, an Apple mediaremoted flaw that lets an app gain root privileges. CVSS 7.8. Patch now.
A macOS ClickFix campaign now uses a browser fingerprinting gate to hide AMOS infostealer lures from researchers. See how it works.

Full details and PoC exploit code for CVE-2026-39868 are public. The macOS kernel vulnerability in DTrace lets an app corrupt kernel memory. Patch now.

A macOS privilege escalation flaw gives an unprivileged user root with no user interaction. A full public PoC is out; Apple fixed it in 26.6 with no CVE.