 Do Son
Exim 4.100.1 patches a serious Exim vulnerability set: Proxy Protocol heap flaws, a GnuTLS use-after-free, and SMTP smuggling (CVE-2026-94054). Upgrade now.
Mail Server Security
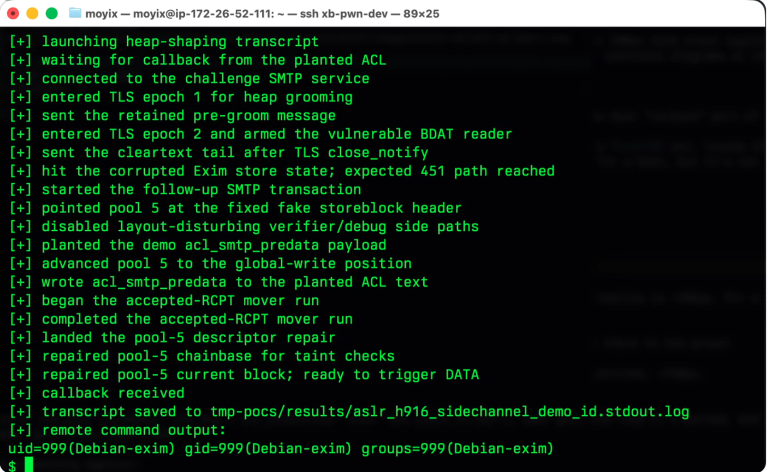
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!