
 Do Son
A new report reveals a phishing campaign using fake ads and login pages to steal credentials from employees in the hospitality and vacation rental industry.
Malvertising

A new report reveals a rise in phishing campaigns that abuse email marketing platforms and cloud services to evade detection and steal credentials from victims.

A new report reveals a global malvertising campaign on Facebook spreading an evolved version of Brokewell malware to steal crypto and bypass 2FA.

A new report from Cisco Talos details PS1Bot, a modular PowerShell-based malware campaign using malvertising to steal data and maintain stealthy persistence.

Check Point Research exposes JSCEAL, a stealthy malware campaign using malvertising and fake apps to steal crypto credentials and wallets via compiled JavaScript payloads.

Malicious scripts disguised as Cloudflare human verification are embedded in WordPress themes, tricking users into executing PowerShell commands that deliver malware.
Attackers exploit JSONP flaws in Google APIs to inject malicious scripts into e-commerce sites, silently redirecting users to fake payment pages.

Beware fake Kling AI sites! A new campaign uses deceptive filenames to trick users into downloading infostealers, stealing crypto and browser data.

A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.

Watch out! Sophisticated Facebook ads lure crypto users to download malware via fake platforms and celebrity endorsements. Bitdefender warns of data theft.
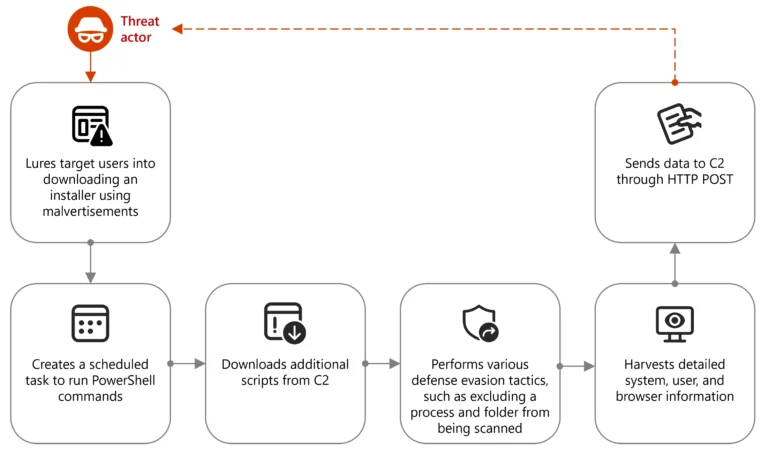
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

Malvertising campaign targets Onfido users via deceptive Google ads, using Evilginx to steal credentials.