 Do Son
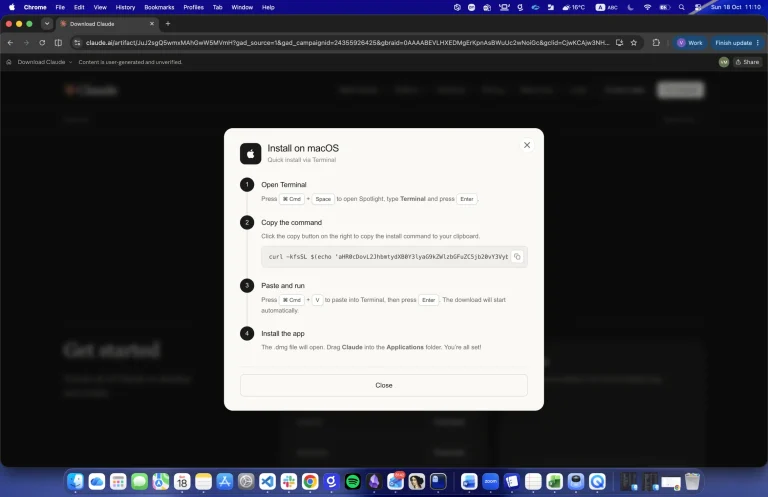
Gen Digital exposes a Claude malware campaign on claude.ai. This fake Download Claude malware campaign uses Google Ads and ClickFix to drop AMOS.
Malvertising
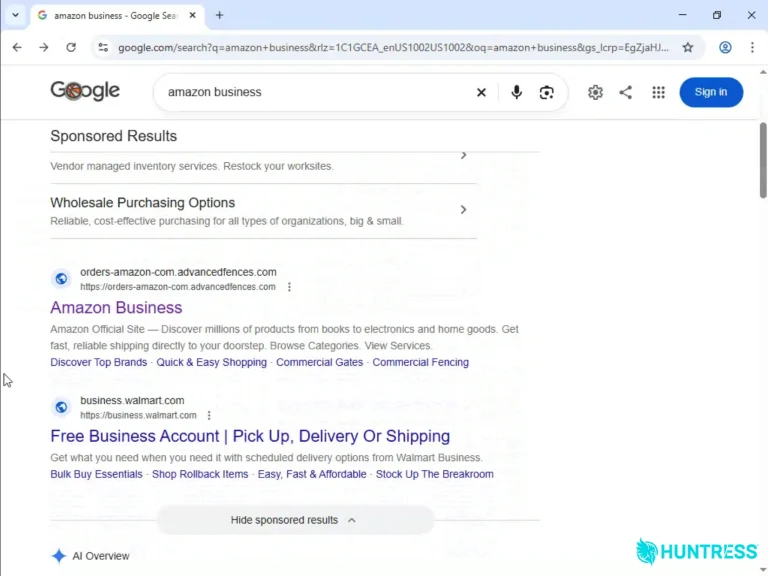
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
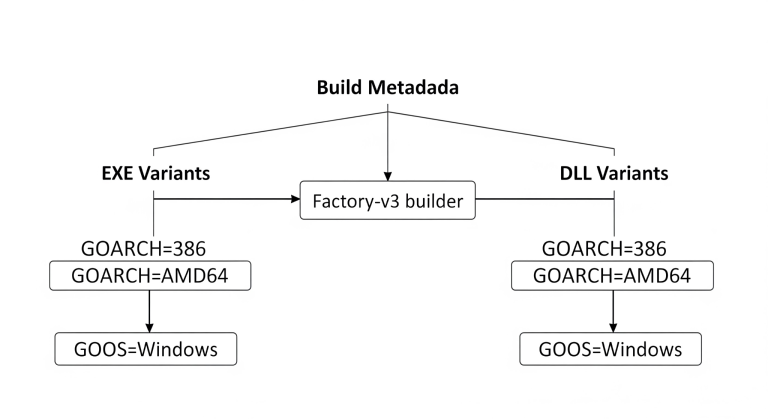
A new Vidar stealer campaign uses the Factory-v3 loader and fake certificates to deploy malware. Learn how attackers hide XMRig and bypass security.

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.
Trend Micro tracked a ClickFix malvertising campaign that abused claude.ai shared chat to deliver the MacSync infostealer to Mac developers.

Threat actors are using AI social engineering lures to distribute malware and steal credentials. Learn how fake ChatGPT and DeepSeek campaigns work.

A massive wave of APAC malvertising scam campaigns floods Meta advertising platforms, targeting health and financial anxieties across 13 countries.

Researchers uncover the Tampered Chef malware cluster disguised as PDF editors and tools. Learn how these stealthy threats bypass corporate defenses.
Sophos X-Ops uncovers a fake Claude AI site (claude-pro.com) distributing an undocumented backdoor via DonutLoader. Protect your team from AI-themed lures.
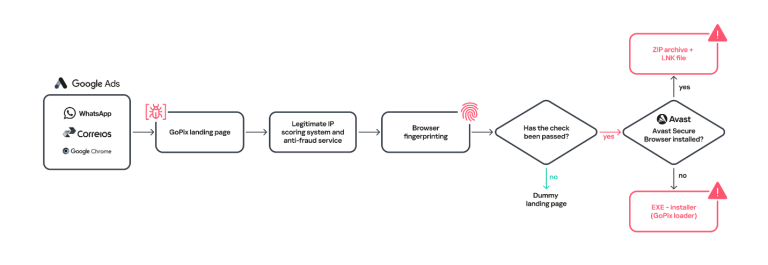
Kaspersky Labs details GoPix, a highly advanced Brazilian banking Trojan using memory-only implants and MitM attacks to target Pix and crypto.
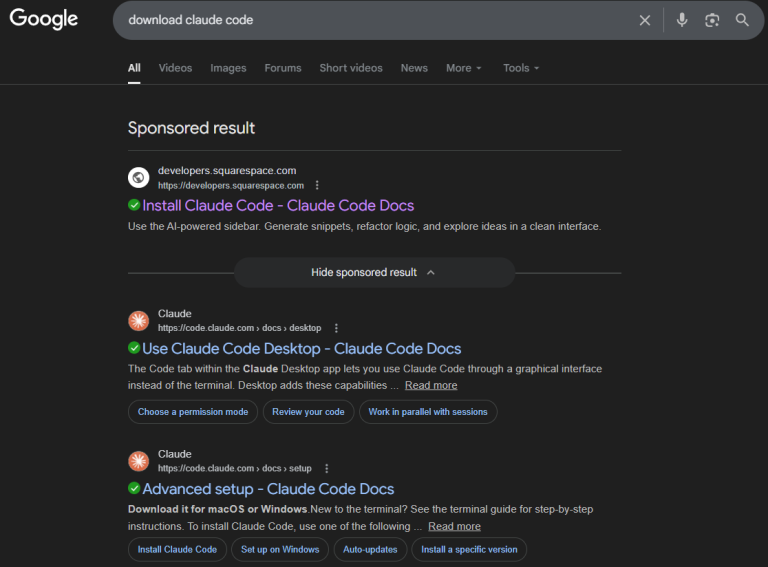
Bitdefender exposes a malvertising campaign targeting developers searching for Claude Code. Fake Google Ads deploy Windows stealers and macOS backdoors.
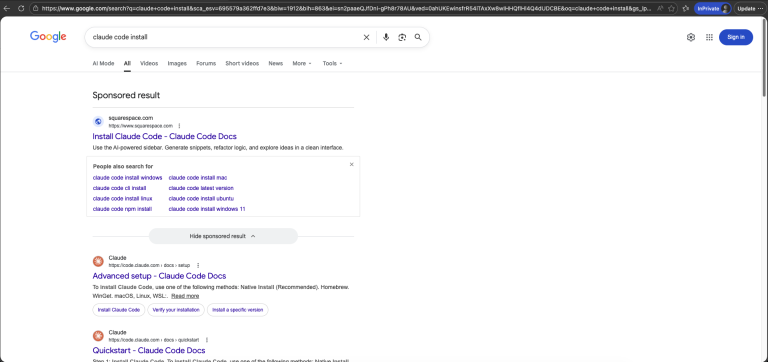
Hackers are targeting AI developers with a fake Claude Code "InstallFix" malvertising campaign, using malicious terminal commands to drop Amatera malware.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.

Varonis uncovers 1Campaign, a sophisticated tool by 'DuppyMeister' that helps hackers bypass Google Ads security to deliver phishing and crypto drainers.
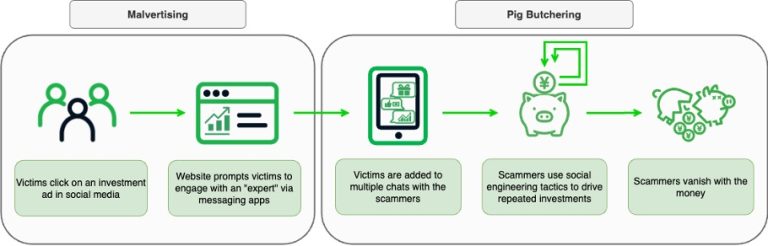
Infoblox Threat Intel exposes a highly scalable hybrid scam merging automated malvertising with "pig butchering" to drain global crypto investors' funds.

Sophos reveals "TamperedChef" malvertising. Fake "AppSuite PDF Editor" uses valid EV certs to deploy infostealers globally. Check your systems now.

Infoblox researchers hijacked a scam network using the "Sitting Ducks" DNS flaw. 57M logs reveal how abandoned domains fuel global push notification spam.

The DOJ seized web3adspanels.org, disrupting a $14M bank takeover scheme that used fake Google and Bing ads to steal thousands of credentials.

Acronis exposed TamperedChef, a global campaign using US shell companies to sign trojanized apps. The malware deploys a stealthy, obfuscated JavaScript backdoor via a scheduled task for long-term persistence.

Rhysida ransomware is abusing Microsoft Trusted Signing to deploy OysterLoader (IAT) via Bing/Teams malvertising. The gang leveraged 40+ certificates to sign malware, bypassing security filters.

The TamperedChef malware campaign used a trojanized PDF editor, delivered via malvertising, to stealthily harvest browser credentials after operating undetected for two months.

A new report reveals a phishing campaign using fake ads and login pages to steal credentials from employees in the hospitality and vacation rental industry.