Skip to content
October 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Microsoft Entra

Microsoft Entra

Attackers Abuse ConnectWise Cloud Backup Credential to Breach Over 300 Microsoft 365 Tenants Microsoft Entra sign-in logs showing ConnectWise Cloud Backup and ConnectWise Cloud Backup breach activity
  • Cybercriminals

Attackers Abuse ConnectWise Cloud Backup Credential to Breach Over 300 Microsoft 365 Tenants

Do Son October 21, 2026 0
TL;DR Threat actors stole a vendor API secret belonging to ConnectWise Cloud Backup (formerly SkyKick) to access...
Read More Read more about Attackers Abuse ConnectWise Cloud Backup Credential to Breach Over 300 Microsoft 365 Tenants
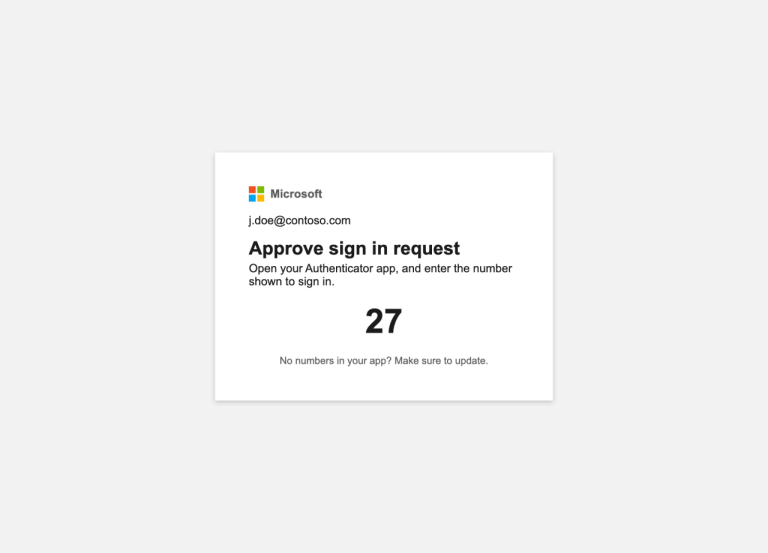
Passkey Phishing Campaign Uses Vishing Calls to Hijack Microsoft Entra Accounts Passkey phishing vishing attack targeting Microsoft Entra passkey enrollment by O-UNC-066
  • Cybercriminals

Passkey Phishing Campaign Uses Vishing Calls to Hijack Microsoft Entra Accounts

Do Son July 15, 2026 0
At a Glance Actor O-UNC-066 (Okta); tracked as CL-CRI-1147 / “Pink” by Palo Alto Unit 42; linked...
Read More Read more about Passkey Phishing Campaign Uses Vishing Calls to Hijack Microsoft Entra Accounts

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2016-20097CVSS 8.7
    Weaver (Fanwei) E-cology 8.0 contains a SQL injection vulnerability in the SignatureDownLoad servlet that allows unauthenticated remote attackers...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2019-25765CVSS 8.7
    ASP-CMS contains a SQL injection vulnerability in the commentList.asp endpoint that allows unauthenticated remote attackers to inject arbitrary...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2019-25776CVSS 8.7
    Weaver E-cology contains an unauthenticated SQL injection vulnerability that allows remote attackers to execute arbitrary SQL queries by...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    CISA KEV📅 Added to KEV: Oct 26, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    CISA KEV📅 Added to KEV: Oct 26, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18450CVSS 9.8
    The BMC does not correctly enforce integrity and encryption requirements for IPMI commands. An attacker may be able...
    📅 Updated: Oct 27, 2026
  • CVE-2026-91323CVSS 9.8
    Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected...
    📅 Updated: Oct 27, 2026
  • CVE-2026-87302CVSS 9.1
    Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected...
    📅 Updated: Oct 27, 2026
  • CVE-2026-110063CVSS 10.0
    Improper link resolution before file access ('link following') in VM Inspector for Azure Virtual Machines allows an unauthorized...
    📅 Updated: Oct 27, 2026
  • CVE-2026-10757CVSS 9.8
    There is a SQL injection vulnerability in Esri ArcGIS Server versions 12.1 and earlier on Windows and Linux...
    📅 Updated: Oct 27, 2026
  • CVE-2026-107656CVSS 9.8
    An authentication bypass using an alternate path or channel vulnerability in Fortinet FortiSandbox 5.0.0 through 5.0.6, FortiSandbox 4.4.0...
    📅 Updated: Oct 27, 2026
  • CVE-2026-109391CVSS 9.2
    Square Squash through commit e73f280 contains an insecure deserialization vulnerability that allows unauthenticated attackers to store crafted YAML...
    📅 Updated: Oct 27, 2026
  • CVE-2026-105223CVSS 9.1
    maclof kubernetes-client 0.17.0 before 0.32.0 disables TLS certificate verification in parseKubeconfig() and parseKubeconfigFile() when a kubeconfig lacks certificate-authority-data,...
    📅 Updated: Oct 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.