 Do Son
CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.
Mirai

Nozomi details the Tengu botnet, a modernized Mirai variant. This IoT malware adds encrypted C2, proxy, anti-analysis, and self-defense to resist removal.
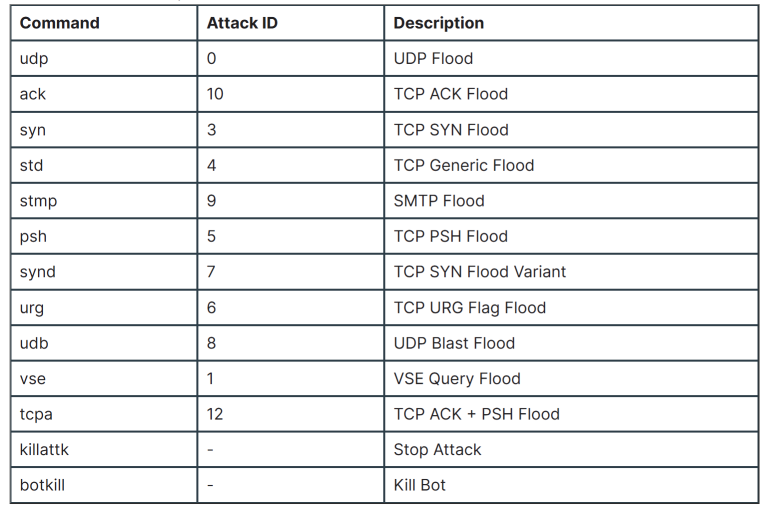
FortiGuard unmasks Nexcorium, a Mirai variant targeting DVRs via CVE-2024-3721. Secure your IoT devices against this multi-arch DDoS botnet. Patch now!
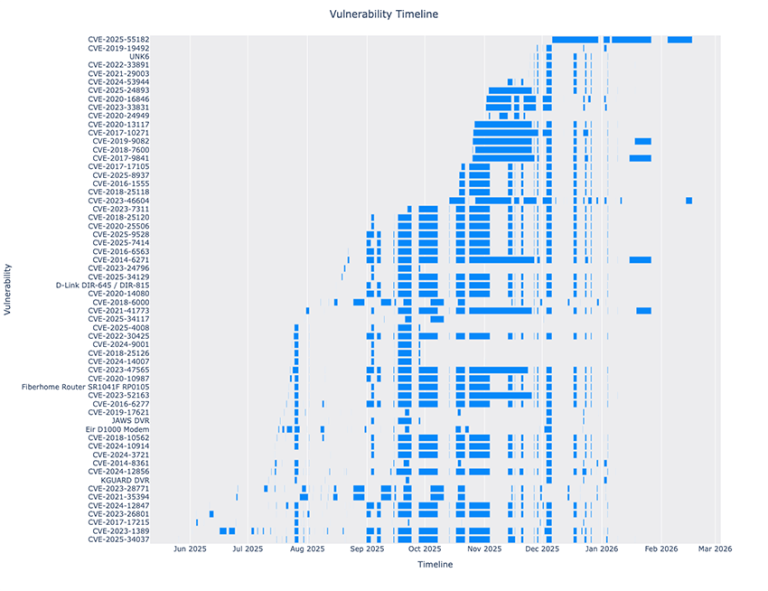
BitSight exposes RondoDox, a relentless IoT botnet using a "shotgun approach" with 174 exploits to hijack residential devices for massive DoS attacks.

Trend Micro discovered RondoDox, a new botnet leveraging 50+ exploits (including the Pwn2Own TP-Link flaw) in an "exploit shotgun" approach to compromise routers, DVRs, and IoT globally.

A new report reveals MystRodX, a stealthy backdoor that uses passive wake-up triggers and multi-layer encryption to operate undetected in networks for months.

RapperBot botnet resurfaces with 50,000+ active bots, now demanding Monero extortion to halt DDoS attacks. The self-proclaimed "rapper" malware targets IoT devices globally.

Akamai reports active exploitation of critical Wazuh RCE (CVE-2025-24016) by multiple Mirai botnets, targeting IoT devices since March 2025.

A new Mirai botnet variant is exploiting CVE-2024-3721 to infect vulnerable DVRs. Learn how this sophisticated attack works and if your surveillance system is at risk.

Stay informed about the security risks of TVT NVMS9000. Learn about a major vulnerability that exposes DVRs to cyber attacks.
Explore the rise of Mirai malware exploiting IoT vulnerabilities in Edimax devices and find out how to protect yourself.

Discover the dangerous Hail Cock botnet and its target: the vulnerable DigiEver DS-2105 Pro DVRs. Learn how to safeguard your devices.

Learn about the active exploitation of the Apache OFBiz vulnerability, its potential impact, and how to mitigate the risks.
Resurgence of Mirai botnet variants, coupled with AI-enhanced DDoS attacks, underscores the critical need for robust cybersecurity measures

The active exploitation of CVE-2024-29973 by a Mirai-like botnet underscores the urgency of applying the necessary security patches
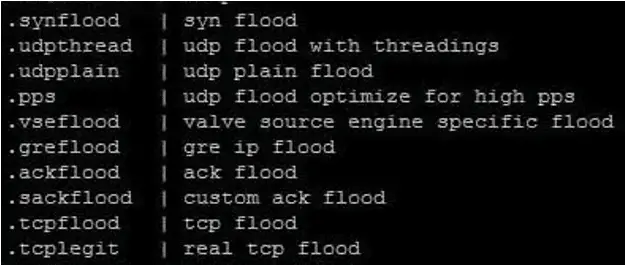
This vulnerability, found in the TP-Link Archer AX21's web management interface, allows hackers to inject malicious code without needing the router's password
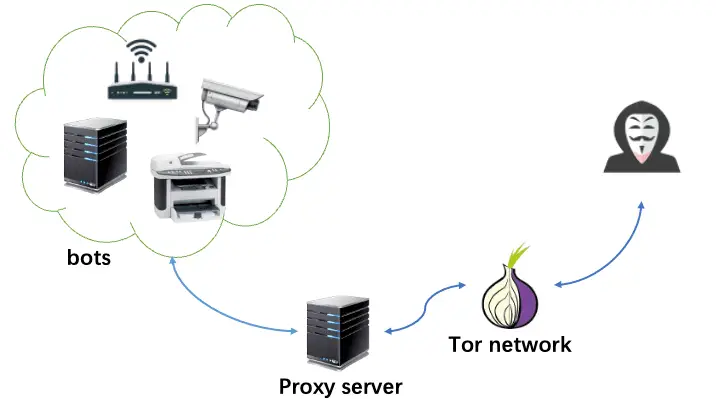
Rimasuta botnet is designed to infiltrate systems and evade detection. It employs advanced data encryption and communication techniques

Unlike Mirai, which is aimed at DDoS attacks, this new worm, dubbed NoaBot, installs crypto miners, enabling attackers to exploit

Security researchers from xlab-qianxin detected Mirai.TBOT, a variant of the original Mirai, operates with distinct characteristics

This vulnerability cataloged as CVE-2023-49897 with a CVSS v3 score of 8.0, allows authenticated attackers to execute OS commands remotely

Utilizing several vulnerabilities, IZ1H9 poses a serious threat, taking full control of compromised devices to form part of its botnet.
Trend Micro posted a blog on Wednesday that their network monitoring system recently detected a large-scale scanning...