
 Do Son
Microsoft uncovers a massive npm dependency confusion attack targeting enterprise infrastructure. Learn how these malicious packages discovered run code.
npm registry
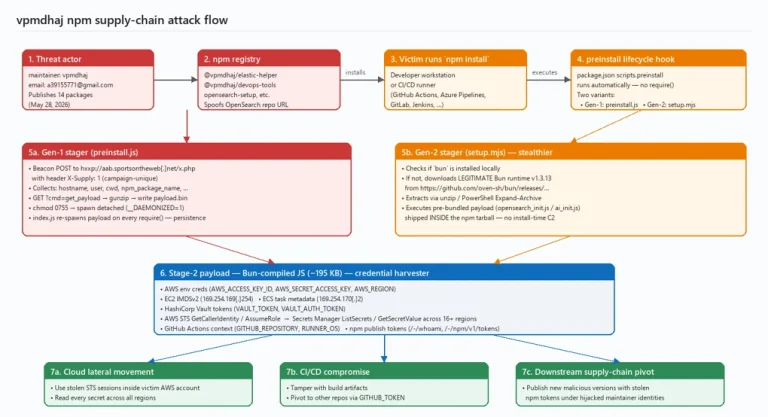
A critical npm supply chain attack exploits lookalike packages to distribute credential harvesting malware. Learn how to protect your cloud assets.

A new npm supply chain attack, "xlsx-to-json-lh," uses typosquatting to enable remote code execution, silently awaiting a "kill switch" to delete project directories.