 Do Son
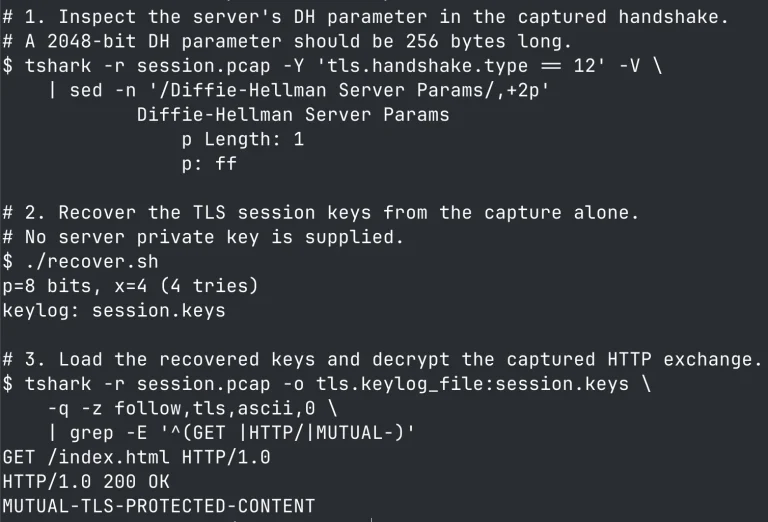
FoxIO releases details and proof-of-concept code for three GoAhead TLS vulnerabilities, including a CVSS 9.1 revoked-certificate bypass. Patch to 6.1.1.
openssl
The OpenSSL 4.1.0 release introduces initial Elbrus e2k architecture support, DTLS 1.3 protocol capabilities, and post-quantum performance upgrades.
Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.
OpenSSL patched 14 OpenSSL vulnerabilities, including high-severity DTLS flaw CVE-2026-84782 that can leak heap memory. Upgrade to 4.0.3 now.
The August 2026 OpenSSL security update fixes 9 flaws, including a QUIC double free (CVE-2026-18798) and a CMS heap overflow. Patch now.
A new OpenSSL HollowByte vulnerability enables remote DoS attacks using just 11 bytes. Learn how to protect your servers against this OpenSSL DoS attack.
A widespread OpenSSL error handling flaw makes apt fail HTTPS in FIPS mode. A stale error queue entry gets misread as fatal. Audit your code.

New OpenSSL security patches address a critical use-after-free bug that introduces an immediate remote code execution risk across enterprise systems.

OpenSSL's April 2026 advisory reveals 7 flaws, including a moderate RSA memory leak (CVE-2026-31790). Learn if your version is affected and how to patch.

HPE patches critical RCE (CVE-2026-23592) in Fabric Composer. Authenticated attackers can seize the OS via backup tools. Update to v7.3.0 immediately.
OpenSSL patches 12 flaws, including high-severity CVE-2025-15467 allowing pre-auth RCE via CMS. Update to 3.6.1/3.0.19 immediately to secure systems.

A newly disclosed vulnerability in the Zabbix Agent and Agent 2 for Windows could allow local attackers...
OpenSSL patches three flaws, including CVE-2025-9230 (RCE/DoS risk) and a SM2 timing side-channel (CVE-2025-9231) that could allow private key recovery on ARM64.

A high-severity flaw (CVE-2025-8069) in AWS Client VPN for Windows allows local users to escalate privileges due to an OpenSSL config file path vulnerability.

A critical Icinga 2 vulnerability (CVSS 9.3) allows malicious certificate impersonation, affecting builds with older OpenSSL. Update now!
Discover the high-severity vulnerability in OpenSSL (CVE-2024-12797) that could allow man-in-the-middle attacks. Learn about the potential consequences and ways to mitigate the risk.
CVE-2024-37404: Critical RCE Flaw Discovered in Ivanti Connect Secure & Policy Secure, PoC Published

CVE-2024-37404: Critical RCE Flaw Discovered in Ivanti Connect Secure & Policy Secure, PoC Published
Stay secure with Ivanti Connect Secure and Policy Secure. Find out about the critical RCE vulnerability CVE-2024-37404 and learn how to protect your systems.

Researchers issued CVE-2023-42465 for SUDO for this vulnerability. This flaw classified as critical has been found in sudo up to 1.9.14.

CVE-2023-5363 is caused by an incorrect cipher key and IV length processing during the initialization of some symmetric ciphers

The implications of CVE-2023-2650 are more pronounced in specific OpenSSL subsystems such as OCSP, PKCS7/SMIME, CMS, CMP/CRMF, and TS

The flaw, tracked as CVE-2023-0286, has been described as a type confusion in X.509 GeneralName that allow an attacker to read memory contents
CVE-2022-3602 could result in a crash or potentially remote code execution depending on the stack layout for any given platform/compiler