 Do Son
Spring Cloud Config fixes a 9.1 CVSS directory traversal (CVE-2026-40982) and a GCP secret leak. Secure your distributed system—upgrade to the latest patches!
Patch Alert

Redis releases critical patches for 5 vulnerabilities, including RCE via the RESTORE command (CVSS 7.7). Secure your self-managed Redis instances immediately!
Apache Wicket 10.9.0 fixes 3 Critical flaws: Path Traversal (CVE-2026-43975), Session Fixation, and Resource Guard bypass. Secure your Java apps and patch now!
Critical 9.0 CVSS flaw in Thymeleaf (CVE-2026-41901) allows SSTI and arbitrary code execution. Secure your Java web apps—upgrade to v3.1.5.RELEASE now!
A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!

A critical 9.6 CVSS flaw in Argo CD (CVE-2026-42880) allows read-only users to extract plaintext Kubernetes secrets via Server-Side Diffs. Patch to v3.3.9 now!
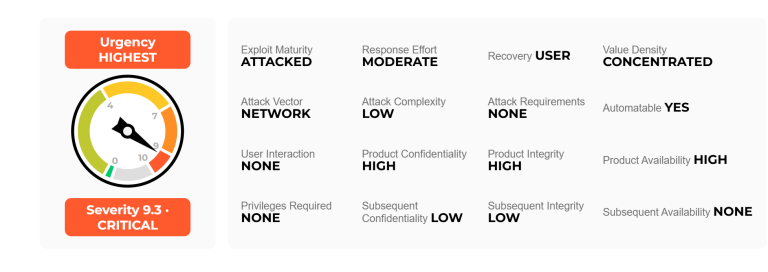
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.

SUSE Rancher v2.14.1 fixes an 8.4 CVSS path traversal flaw (CVE-2026-25705) in UI Extensions. Prevent binary hijacking and host access—upgrade immediately!

Public PoC exploit released for OPNsense! A critical root-level RCE and lockout bypass allow total firewall takeover. Upgrade to OPNsense 26.1.7 immediately.

A critical injection flaw (CVE-2026-40563) in Apache Atlas lets attackers manipulate Gremlin logic to extract restricted enterprise data. Patch to v2.5.0!

Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!

Apache Polaris 1.4.1 fixes critical flaws allowing attackers to bypass S3/GCS boundaries and seize cloud credentials. Patch your Iceberg catalog now!

Apache Neethi v3.2.2 patches critical flaws, including an exponential complexity attack and infinite loops. Secure your Java web services and patch today!

Gotenberg PDF API hit with a rare CVSS 10 flaw. Unauthenticated RCE, file overwrites, and SSRF bypasses discovered. Upgrade to version 8.32 immediately.
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!

MOVEit Automation faces a critical 9.8 CVSS flaw (CVE-2026-4670). Attackers can bypass auth to seize admin control and expose data. Patch immediately.

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!

libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.

Wazuh patches a critical 9.0 CVSS flaw (CVE-2026-30893) in cluster sync. Malicious peers can achieve RCE and lateral movement. Upgrade your clusters now.

NVIDIA patches a critical 8.6 CVSS flaw in NemoClaw. Prompt injection could leak sensitive host secrets. Upgrade to v0.0.18 to secure your AI agent sandboxes.

Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.