
 Do Son
Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.
Patch Alert

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.

Critical Siemens Alert: 9.3 severity XSS flaws hit SIMATIC S7 PLCs. Attackers can hijack sessions via web interfaces. Update to V3.1.6 or follow mitigations.

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.

Urgent: Siemens patches a 9.3 severity Path Traversal (CVE-2026-41551) in ROS#. Attackers can read/write arbitrary files on robotics systems. Update to V2.2.2!
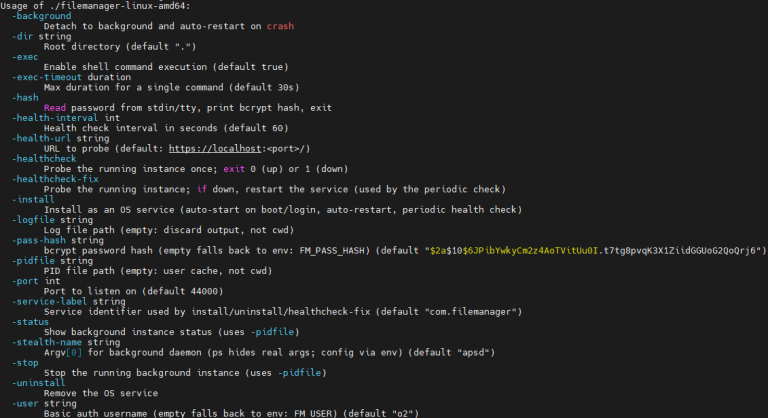
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!

Urgent: Dell patches a 9.8 severity credential flaw (CVE-2026-40636) in ECS and ObjectScale. Secure your enterprise storage by upgrading to version 4.3.0.0.

Apache Tomcat RCE alert: CVE-2026-34486 exploit code and details are now public. A "fail-open" flaw enables RCE via Tribes clustering. Update immediately.
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!
PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!

Urgent: Apache CloudStack patches critical flaws (CVE-2026-25199, CVE-2026-25077) enabling VM hijacking and KVM host RCE. Secure your cloud environment now.

Update cPanel immediately! High-severity vulnerabilities (CVSS 8.8) allow Perl injection and privilege escalation. Protect your hosting environment now.

Protect your Grav CMS deployments. Attackers are chaining CVE-2026-42613 and CVE-2026-42607 to achieve unauthenticated remote code execution. Patch today!
Security researchers expose catastrophic flaws in Sandboxie. CVE-2026-34459 enables a direct sandbox escape to SYSTEM privileges. Update to v1.17.3 today.

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.

Rancher Fleet fixes a 9.9 CVSS flaw (CVE-2026-41050) allowing tenants to bypass ServiceAccount isolation and steal secrets. Upgrade your GitOps engine now!

Zabbix fixes high-severity XSS (CVE-2026-23926) and Oracle injection flaws. Don't let your monitoring tool become a backdoor—upgrade your Zabbix server now!

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!
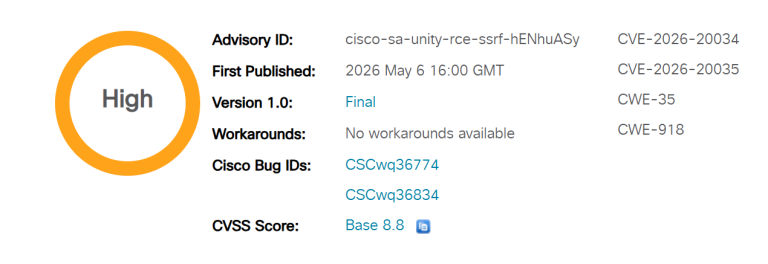
Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
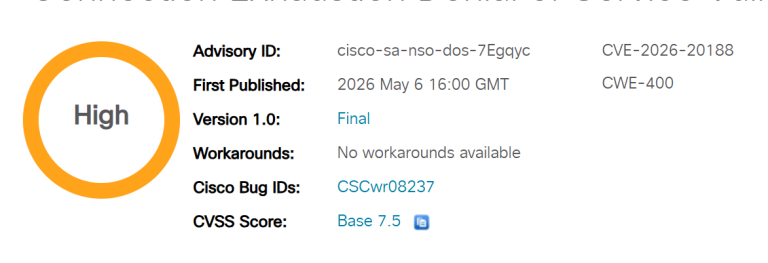
Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!

ArcadeDB 26.4.1 fixes a critical 9.0 CVSS authorization bypass (CVE-2026-44221) that dismantles database isolation. Secure your multi-model data and patch now!