
 Do Son
Discover how Fluffy Wolf phishing attacks target Russian organizations with the new PowerLoader malware to deploy PureRAT and Pay2Key ransomware.
PureRAT
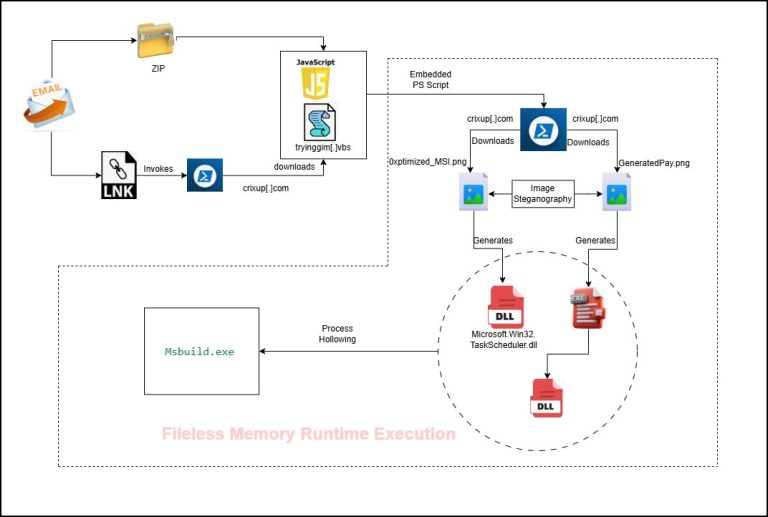
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

Sekoia exposed a campaign exploiting compromised Booking.com/Expedia accounts to deliver PureRAT malware via a ClickFix lure. Attackers use authentic reservation details to steal guest credentials.

Huntress details a multi-stage attack that uses DLL sideloading and obfuscated Python to deliver PureRAT, a commercial-grade remote access trojan linked to PXA Stealer.

eSentire uncovered a sophisticated attack on a US accounting firm, deploying PureRAT via the new Ghost Crypt crypter and a stealthy "Process Hypnosis" injection technique.