 Do Son
Ransomware gangs exploit CVE-2026-0257, a GlobalProtect authentication bypass in PAN-OS, to slip past MFA and open VPN sessions. Patch now.
ReliaQuest
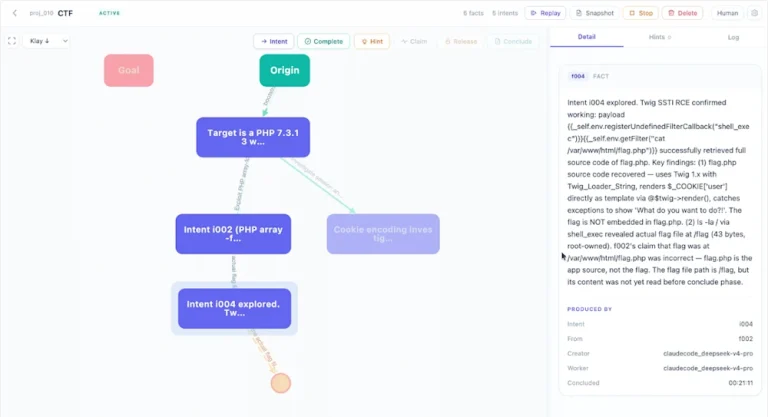
ReliaQuest details an AI agent attack that used one exposed endpoint and the Cairn platform to achieve a full server takeover in under 24 hours.
ReliaQuest found the Gryxa toolkit, AI-built malware that steals crypto credentials and spies on how defenders try to remove it across 324 hosts.
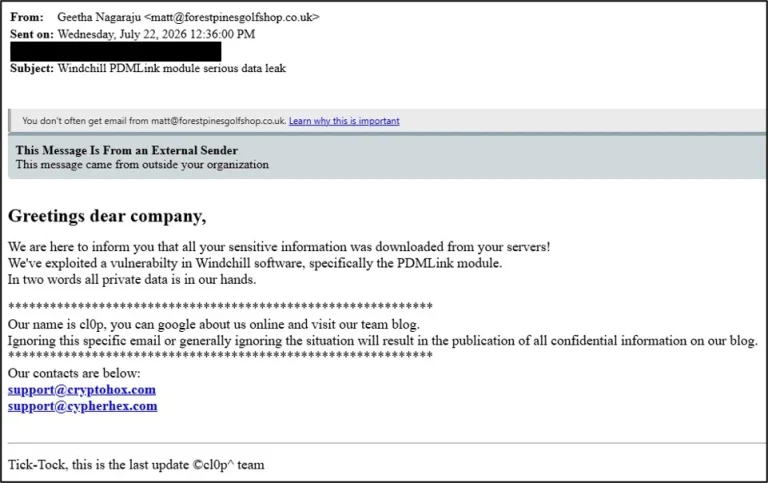
The Clop web shell targets PTC Windchill via CVE-2026-12569, stealing credentials and engineering data in a mass-extortion campaign.
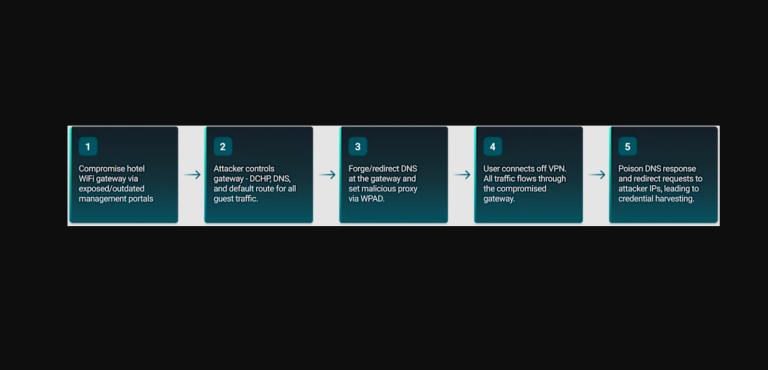
ReliaQuest found hotel Wi-Fi DNS poisoning sending travelers to fake Microsoft 365 pages. Full-tunnel VPN stops the Microsoft 365 account compromise.
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.

ReliaQuest uncovers OP-512, a China-linked cluster using a unique IIS web shell framework with RSA/RC4 encryption and timestomping.

Storm-2603 exploits SmarterMail vulnerability CVE-2026-23760 to deploy Warlock ransomware. Upgrade to Build 9511 immediately to prevent system compromise.

Citrix Bleed 2 (CVE-2025-5777, CVSS 9.2) is actively exploited to hijack sessions and bypass MFA on NetScaler ADC/Gateway. Patch immediately to prevent covert access and data theft.