
 Do Son
Three critical Wazuh manager vulnerabilities (CVSS 9.1) were disclosed with public PoC exploit code, enabling root RCE and admin token forgery.
Root RCE
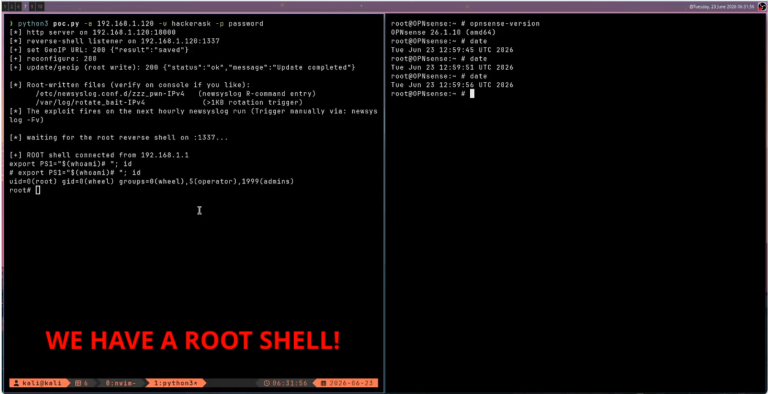
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
A critical Cisco SD-WAN vulnerability is actively exploited in the wild. Learn how to inspect logs and secure your deployment immediately.

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!
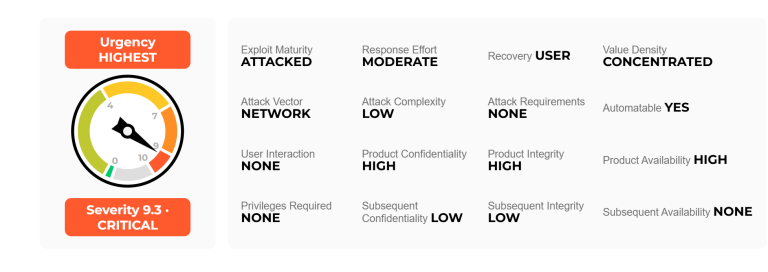
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!

Public PoC exploit released for OPNsense! A critical root-level RCE and lockout bypass allow total firewall takeover. Upgrade to OPNsense 26.1.7 immediately.

Critical Root RCE (CVE-2026-6644) hits ASUSTOR ADM. With PoC code now public, 19,000 NAS devices are at risk. Update to ADM 5.1.3.RGO1 immediately.

CISA adds a CVSS 10 Cisco zero-day and SonicWall exploit chains to its KEV catalog, warning of active exploitation by Chinese APTs and supply chain attacks.