 Do Son
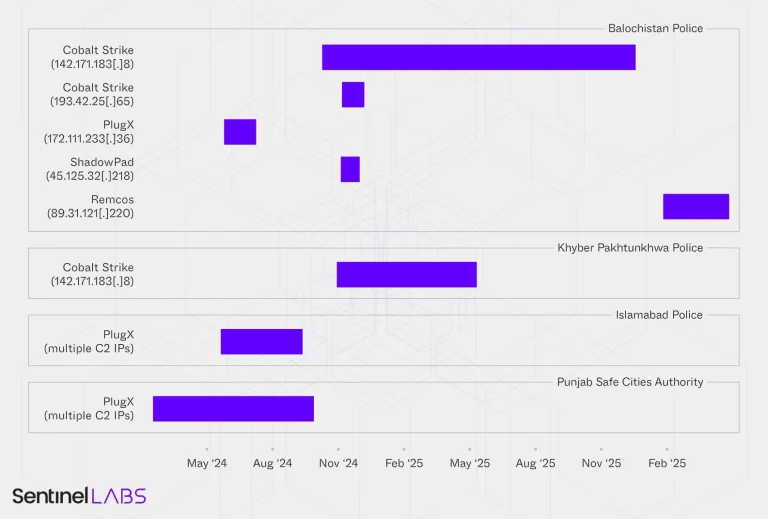
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
SentinelLABS

SentinelLABS reveals fast16, a 2005 framework that predates Stuxnet. It sabotages high-precision calculations in nuclear research by patching math in memory.

A new report reveals that the Lazarus Group is actively monitoring CTI platforms to evade detection and sustain a ClickFix phishing campaign against the cryptocurrency sector.

North Korean APTs are using "NimDoor," a new Nim-based macOS malware, to target Web3/crypto startups via fake Zoom meetings, stealing browser, Keychain, and Telegram data with novel persistence.

SentinelLABS exposes China-nexus APTs (ShadowPad, PurpleHaze) targeting SentinelOne and over 70 organizations in extensive cyber-espionage.