Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Supper Malware

Supper Malware

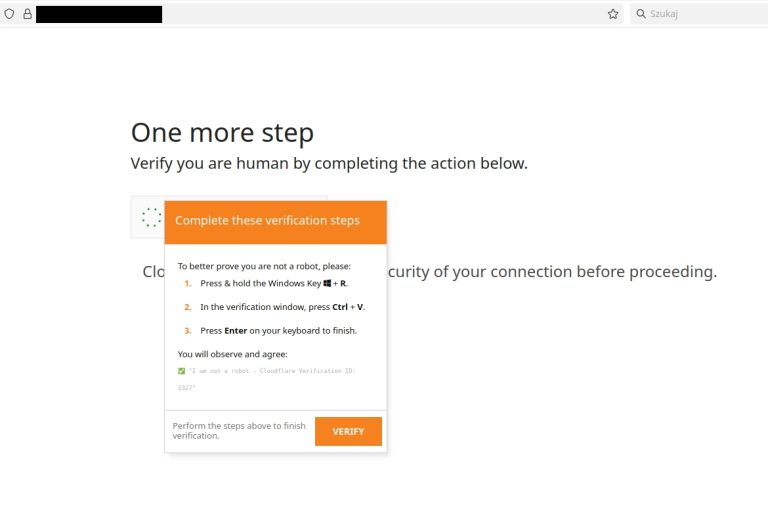
The CAPTCHA Trap: How a Fake “ClickFix” Prompt Unleashed Latrodectus & Supper Malware ClickFix CAPTCHA Latrodectus Malware
  • Malware

The CAPTCHA Trap: How a Fake “ClickFix” Prompt Unleashed Latrodectus & Supper Malware

Do Son February 23, 2026 0
The simple act of verifying you are not a robot has been weaponized into a devastating corporate...
Read More Read more about The CAPTCHA Trap: How a Fake “ClickFix” Prompt Unleashed Latrodectus & Supper Malware
Search

Translation

CVE ALERTS
๐Ÿ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

๐ŸŽฏ

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

๐Ÿ›ก๏ธ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

๐Ÿ™

GitHub Issues
Auto-create alert tickets without duplication.

๐Ÿ“ฌ

Weekly Digest
Clean summaries, eliminating email spam.

๐Ÿท๏ธ

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

๐Ÿ”€

Smart Routing
Route chat channels based on severity levels.

๐Ÿšจ

RBP Tracker
Early warning detection and tracking system.

Subscribe โ€“ $7/mo or try free for 14 days โ†’

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2014-125131CVSS 5.1
    DedeCMS 5.6 and 5.7 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2015-20124CVSS 8.7
    Aspose Importer & Exporter plugin for WordPress before 3.0 contains a path traversal vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2016-20102CVSS 5.1
    JavaMelody before 1.60.0 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by supplying...
    Watchtower Verified📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-112005CVSS 9.2
    WhoDB 0.104.0 before 0.135.0 contains a path traversal vulnerability that allows remote attackers to read and write arbitrary...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114661CVSS 9.0
    OpenRemote 1.2.0 before 1.31.0 contains a missing authorization vulnerability in GatewayServiceResource that allows any authenticated user to start,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-110264CVSS 10.0
    An issue has been discovered in GitLab CE/EE affecting all versions from 7.0 before 18.11.13, 19.0 before 19.0.10,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114575CVSS 10.0
    A flaw has been found in TOTOLINK A950RG 4.1.2cu.5268_B20221104. Affected by this issue is the function UploadCustomModule of...
    📅 Updated: Oct 22, 2026
  • CVE-2026-91403CVSS 9.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    📅 Updated: Oct 21, 2026
  • CVE-2026-105944CVSS 10.0
    Apache Pulsar Manager is a web console for administering Apache Pulsar clusters. It has its own user accounts...
    📅 Updated: Oct 21, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Hereโ€™s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
ยฉ 2017 - 2026 Daily CyberSecurity. All Rights Reserved.