 Do Son
CoreRAT malware powers Core Werewolf attacks on Russian defense and government targets, using fake military PDFs and Telegram phishing.
Telegram Phishing
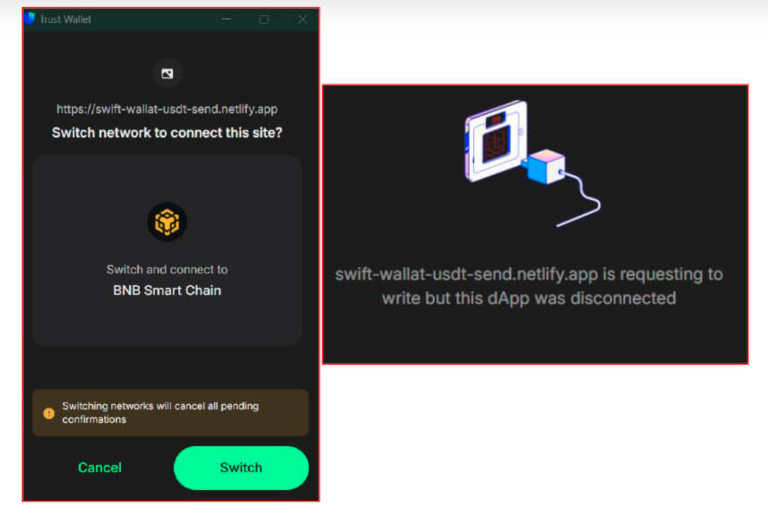
A new QR code "drainer" targets Trust Wallet users on Telegram. It exploits the ERC-20 approve mechanism to wipe USDT. Learn how to protect your assets now.