 Do Son
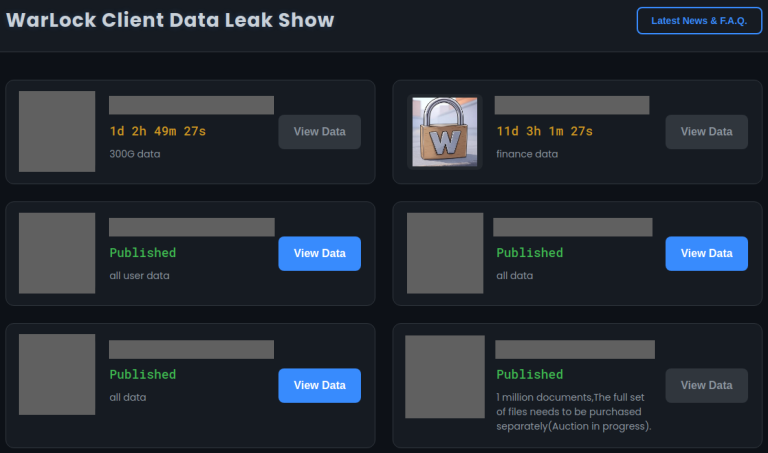
The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
ToolShell

GOLD SALEM (Storm-2603) is exploiting SharePoint via ToolShell then abusing the Velociraptor DFIR tool as a ransomware precursor. The group deploys Warlock and LockBit 3.0 variants, often targeting critical infra.

CISA issues an urgent warning about "ToolShell," a sophisticated exploit chain targeting SharePoint servers with multiple vulnerabilities to install webshells and steal crypto keys.

An unauthenticated SharePoint RCE chain dubbed ToolShell (CVE-2025-49704, CVE-2025-49706) is being actively exploited globally, granting attackers full control of on-premise servers.