 Do Son
TP-Link router assembly moves to the US via a Key Tronic partnership, aiming for FCC compliance and Wi-Fi 8 production in Mississippi.
TP-Link
Discover the new critical Tapo C325WB vulnerabilities exposing TP-Link cameras. Learn how to patch these Tapo C325WB vulnerabilities and secure your video.
TP-Link vulnerabilities include Tapo camera vulnerabilities like CVE-2026-102369 (CVSS 8.7) plus router and Deco flaws. Update firmware now.
A high-severity TP-Link Kasa vulnerability (CVE-2026-76784) allows unauthorized smart home device control. Apply the latest firmware patch immediately.
TP-Link patched an unauthenticated OS command injection flaw (CVE-2026-9254) and other risks like CVE-2026-16348 and CVE-2026-78541 in Archer routers.
TP-Link patches CVE-2026-75616, an Archer C20 command injection flaw that can lead to full device compromise. Update firmware now.
Three high-severity TL-MR6400 router flaws, including CVE-2026-17250, expose devices to code execution. Update your TP-Link firmware now to stay secure.
CVE-2026-19586 (CVSS 9.3) is a pre-authentication OS command injection in TP-Link Omada gateways running OpenVPN Server. Patch the firmware now.
TP-Link patched 5 TP-Link router vulnerabilities in ISP-managed mesh, router, and modem lines, including auth bypass and command injection.
CVE-2026-9044 is a command injection flaw in TP-Link Archer AXE75 OpenVPN, CVSS 8.5. Update to firmware 1.5.6 Build 20260623 now.
A TP-Link TL-WR940N flaw, CVE-2026-12935, allows unauthenticated remote code execution via an RTSP stack buffer overflow. Update the router firmware now.
TP-Link Kasa vulnerability CVE-2026-9770 (CVSS 8.6) lets local attackers intercept admin credentials on EC70 and EC71 cameras. Update firmware now.
A CVSS 8.7 TP-Link router command injection flaw allows unauthenticated remote code execution. Patch CVE-2026-11834 to stop this DHCP option vulnerability.

A critical Archer MR600 command injection vulnerability surfaces within the WireGuard client configuration. Update your TP-Link firmware now.
A critical TP-Link router vulnerability affects Archer models. Download the latest CVE-2026-5509 patch immediately to secure your network environment.

The FCC extends firmware update deadlines to Jan 1, 2029, for foreign drones and routers. Discover how this shift impacts DJI, TP-Link, and US cyber defense.
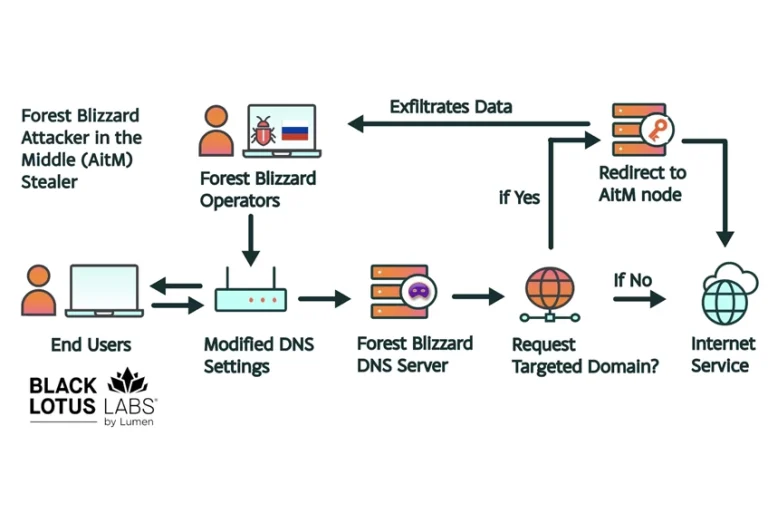
Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.
TP-Link urges Archer AX53 v1.0 users to update firmware to fix 5 critical flaws, including OS command injection & file leaks. Secure your network now!

NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.
TP-Link warns of high-severity flaws (CVSS 8.7) in Tapo C520WS cameras. Attackers can bypass auth or blind your security. Update to firmware 1.2.4 now!
A critical 8.5 CVSS command injection flaw (CVE-2025-15568) in TP-Link Archer AXE75 routers allows complete root-level network takeover. Patch immediately.
TP-Link discloses command injection flaws in Archer BE230 routers (CVE-2026-0630). Authenticated attackers can gain root access. Update firmware now.