 Do Son
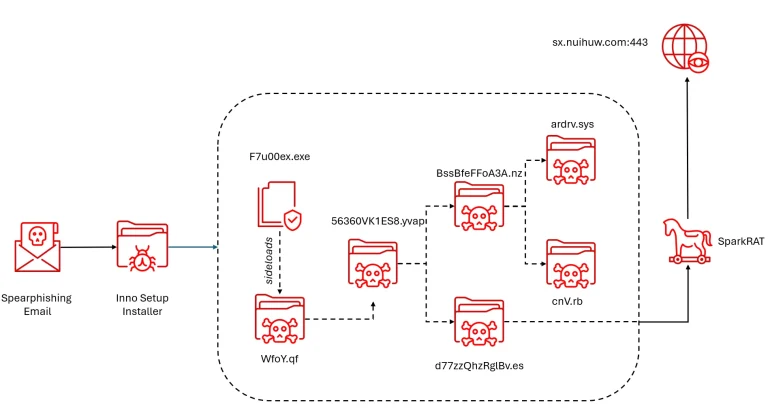
A Cambodia malware campaign hides SparkRAT in PNG files and abuses a vulnerable driver to kill antivirus, Acronis TRU reports.
vulnerable driver

Acronis exposed DragonForce's evolution: the ransomware is compiled with MinGW, uses BYOVD drivers to terminate EDR, and contains fixes to prevent decryption of its Conti V3 derived codebase.

A new report reveals the Silver Fox APT group is abusing a Microsoft-signed vulnerable driver to disable endpoint security and deploy the ValleyRAT backdoor.